US Agencies Warn of Cyberattacks Threatening Industrial Refrigeration

Share
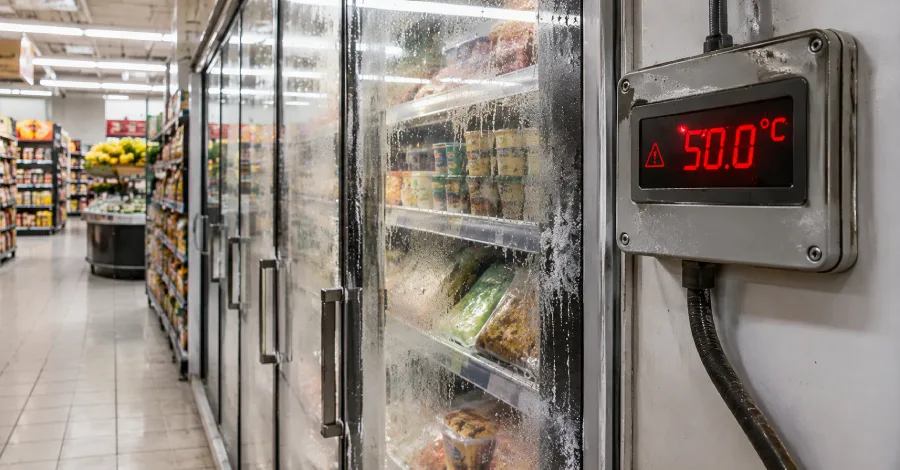
US government agencies have issued a global warning about active cyberattacks targeting industrial refrigeration and cold-chain monitoring systems. Threat actors are exploiting vulnerabilities in unpatched or internet-accessible controllers, risking significant service disruptions, fire hazards, and substantial inventory losses.
These malicious activities aim to force refrigeration units into continuous heating modes. Such attacks could lead to the spoilage of temperature-sensitive goods, equipment damage, and critical fire risks in industrial facilities. Sectors reliant on cold storage, such as food processing, pharmaceuticals, and logistics, face a direct threat.
Organisations operating industrial refrigeration and cold-chain systems are urged to review their cybersecurity postures. Key recommendations typically include patching all known vulnerabilities, securing internet-facing operational technology (OT) systems, implementing robust network segmentation, and enhancing monitoring for unusual activity on controller networks. Strong access controls are also advised to prevent unauthorised remote access.
The warning underscores the increasing targeting of industrial control systems (ICS) and OT environments by cybercriminals. While specific threat actors were not named, the agencies highlighted the active and global nature of these campaigns, emphasising the need for heightened vigilance.