Ledger has ordered distributors across Southeast Asia and Hong Kong to suspend hardware wallet sales following supply-chain tampering incidents.
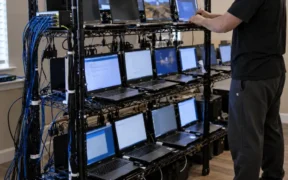
U.S. authorities have dismantled over 40 laptop farms and charged 14 individuals involved in a North Korean remote IT worker fraud scheme.
Attackers are continuing to exploit critical gaps in multi-factor authentication (MFA) coverage, leveraging stolen credentials to compromise systems such as VPNs, RDP, and Windows logons that often remain protected by only a single password.
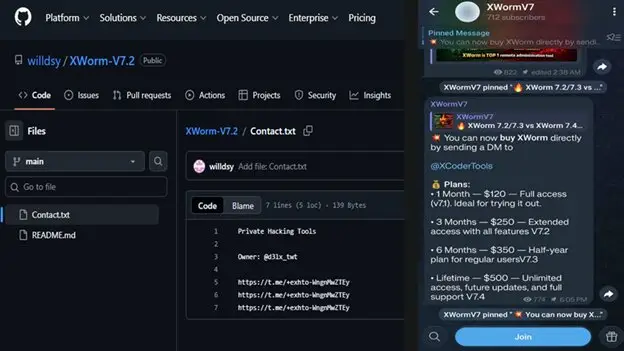
The XWorm Remote Access Trojan (RAT) has evolved into a sophisticated surveillance platform, according to cybersecurity firm Netskope. New plugins enable location tracking, live audio streaming, and the hijacking of authenticated browser sessions, bypassing multi-factor
Ledger has confirmed that hardware implants in its signers, sold through a reseller, allowed attackers to intercept 24-word recovery phrases. On-chain investigators estimate losses at $86 million.