



How Hotels Should Handle Access Requests Under Data Protection Law

Share
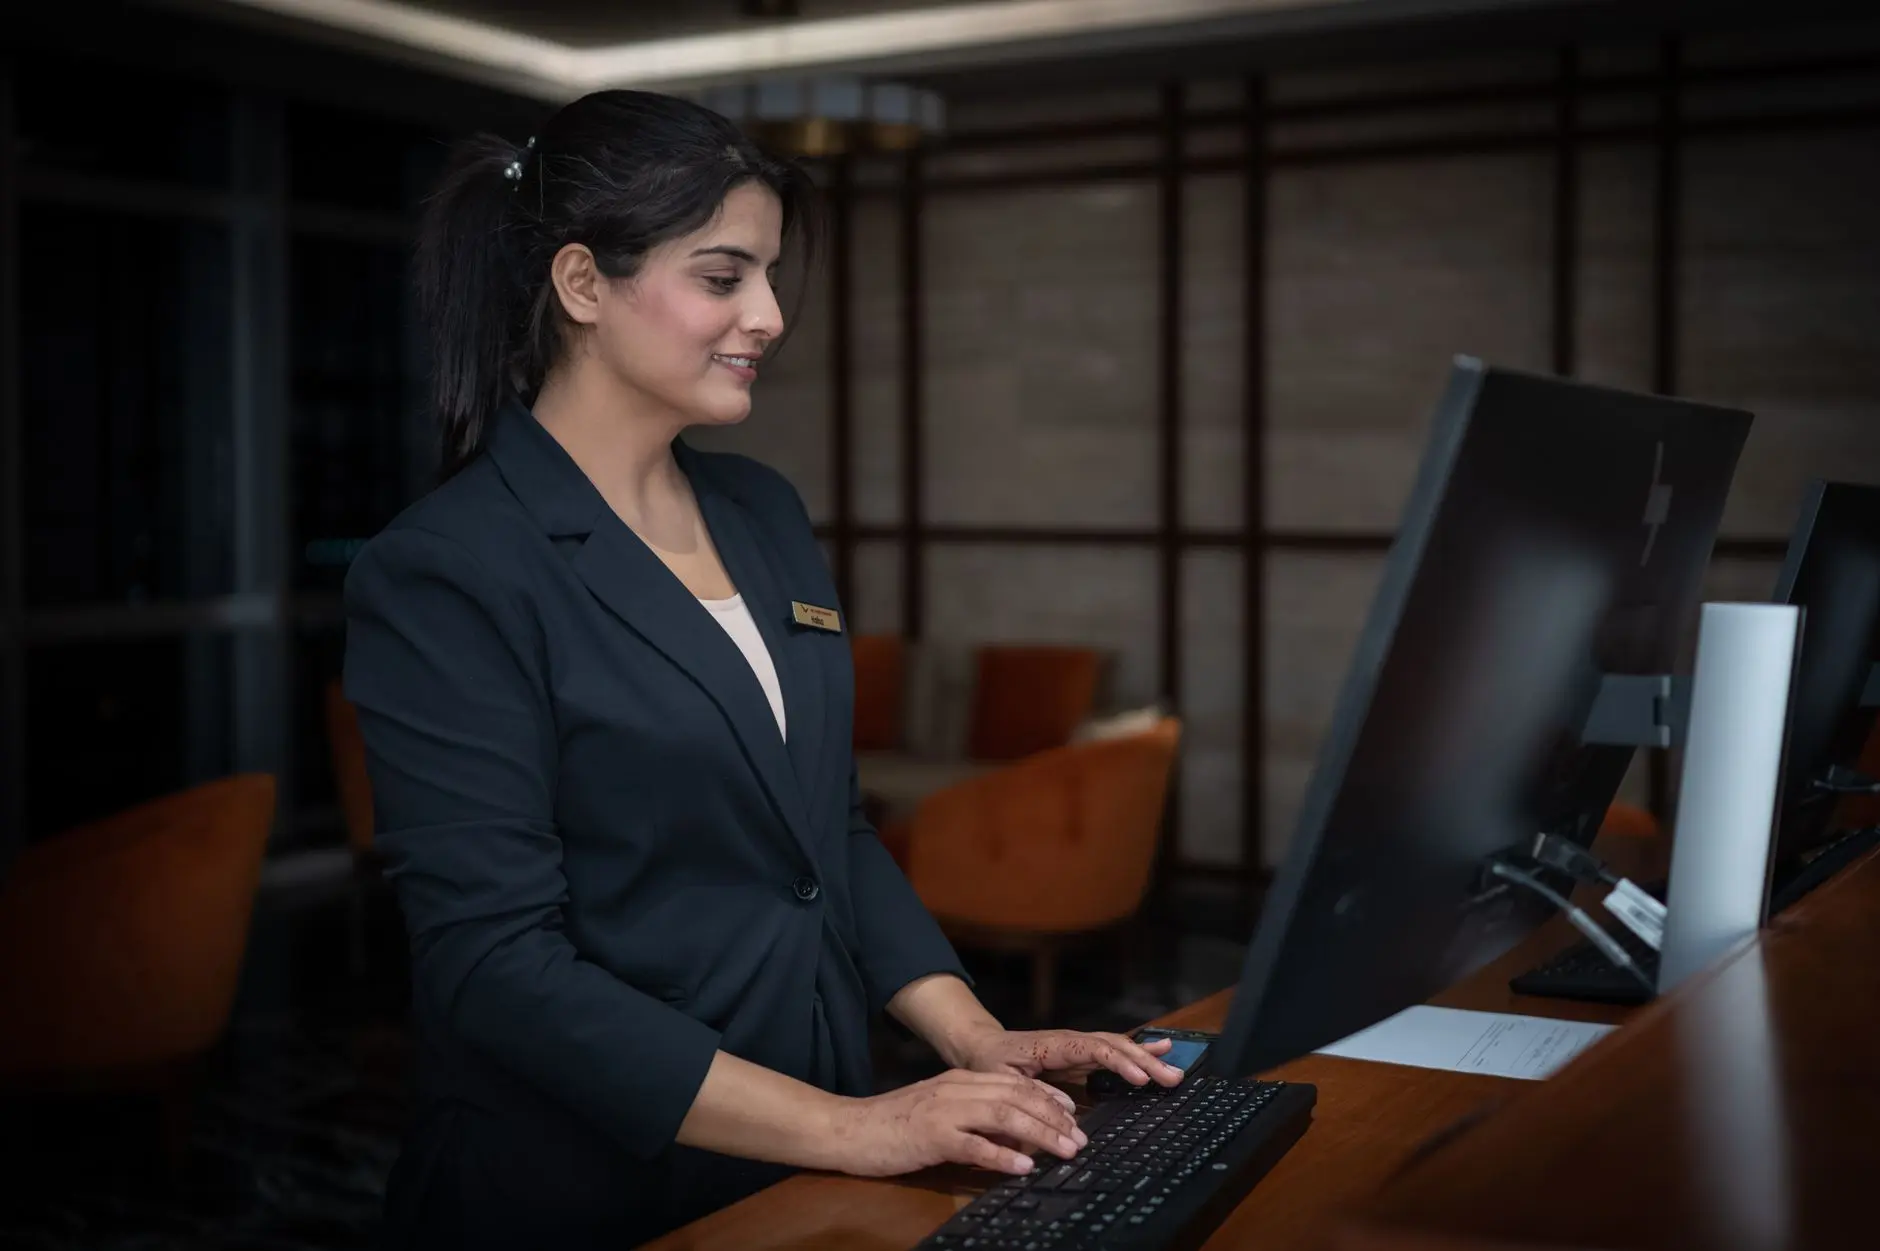
When a guest requests their personal data from a hotel, the front desk or general manager is rarely prepared. Unlike tech firms or financial institutions, hospitality providers collect a massive array of offline and online information, ranging from Wi-Fi login logs and spa bookings to room preferences and closed-circuit television footage. Understanding how hotels handle access requests law obligations is no longer optional. Under modern frameworks like the General Data Protection Regulation (GDPR) and the California Consumer Privacy Act (CCPA), failing to respond correctly to a Data Subject Access Request (DSAR) can trigger severe regulatory investigations and steep financial penalties.
The Unique Data Challenges Faced by Hospitality Businesses
Hotels operate in a decentralized environment where information lives across multiple systems. A single guest’s stay involves property management software, point-of-sale terminals in restaurants, third-party booking engines, housekeeping logs, and physical keycard access records. When an individual demands a copy of their personal data, compliance teams must pull records from disparate silos within tight statutory deadlines, typically one month.
According to the Information Commissioner’s Office, organizations must verify the identity of the requester and provide a concise, transparent, and easily accessible copy of all personal data held, free of charge in most circumstances.
As privacy expert Max Schrems notes, ‘Data protection rights are meaningless if organizations make it operationally impossible for individuals to access what is stored about them.’ For hotels, bridging the gap between customer service and legal compliance requires clear internal procedures and robust staff training.
Real-World Scenario: The Divorcing Couple and CCTV Footage
Consider a frequent business traveler requesting all data held by a major resort chain over a two-year period. Alongside booking histories and loyalty program points, the guest specifically demands access to security camera footage from the lobby and elevators, claiming it is necessary for a personal legal dispute. The hotel now faces a delicate balancing act: fulfilling the guest’s statutory rights while protecting the privacy of other guests and staff captured on the same video recordings.
Under data protection legislation, hotels are permitted to redact or blur the images of third parties before releasing CCTV footage. If redaction is technically impossible or disproportionately difficult, the hotel must evaluate whether it is reasonable to disclose the footage without third-party consent. Having a structured workflow for handling these complex scenarios prevents hasty disclosures that could violate other guests’ privacy.
Step-by-Step Compliance Checklist for Hotels
To ensure smooth operations and regulatory compliance, hoteliers should implement a standardized process for managing incoming requests. The following framework outlines essential operational steps.
| Stage | Action Item | Responsible Department |
|---|---|---|
| 1. Receipt | Log the request date and verify the identity of the requester. | Front Desk / Legal |
| 2. Discovery | Search property management systems, loyalty databases, and Wi-Fi logs. | IT / Operations |
| 3. Review | Redact third-party personal data and exempt internal business notes. | Compliance / Legal |
| 4. Delivery | Transmit data securely to the guest within statutory timeframes. | Guest Relations |
Key Data Sources to Review During a Request
When hotels handle access requests law requirements, staff must know where guest data resides. Failing to check a specific system can lead to incomplete disclosures, which constitutes a regulatory violation.
- Property Management Systems (PMS): Stores past stays, billing addresses, room preferences, and special requests.
- Loyalty and Rewards Programs: Tracks spending habits, birthday details, reward redemptions, and communication preferences.
- Point-of-Sale (POS) Outlets: Records restaurant tabs, spa treatments, and mini-bar purchases linked to a room folio.
- Physical and Digital Security: Includes keycard swipe logs, parking gate entries, and temporary CCTV recordings.
For broader insights on compliance frameworks, review our resources on data protection principles and corporate compliance strategies tailored for customer-facing industries.
Frequently Asked Questions
Can a hotel charge a fee for processing an access request?
In most jurisdictions, initial access requests must be fulfilled free of charge. Hotels can only charge a reasonable fee if a request is manifestly unfounded, excessive, or repetitive.
What happens if a hotel ignores a guest access request?
Ignoring a request violates data protection laws and exposes the hotel to formal complaints filed with data protection authorities, potentially resulting in substantial fines and reputational damage.
How long should CCTV footage be kept?
Hotels should retain security footage only as long as necessary for security or legal purposes, typically between 7 to 30 days, unless a specific preservation hold is requested.
Conclusion
Balancing guest hospitality with stringent legal mandates is a core challenge for modern hoteliers. When hotels handle access requests law guidelines effectively, they build long-term digital trust and protect their brand reputation. By auditing data storage silos, training frontline staff, and establishing secure redaction protocols, hospitality businesses can turn regulatory obligations into a competitive advantage.








Leave a Reply