



What Universities Should Know About ISO 27001 and Privacy Readiness

Share
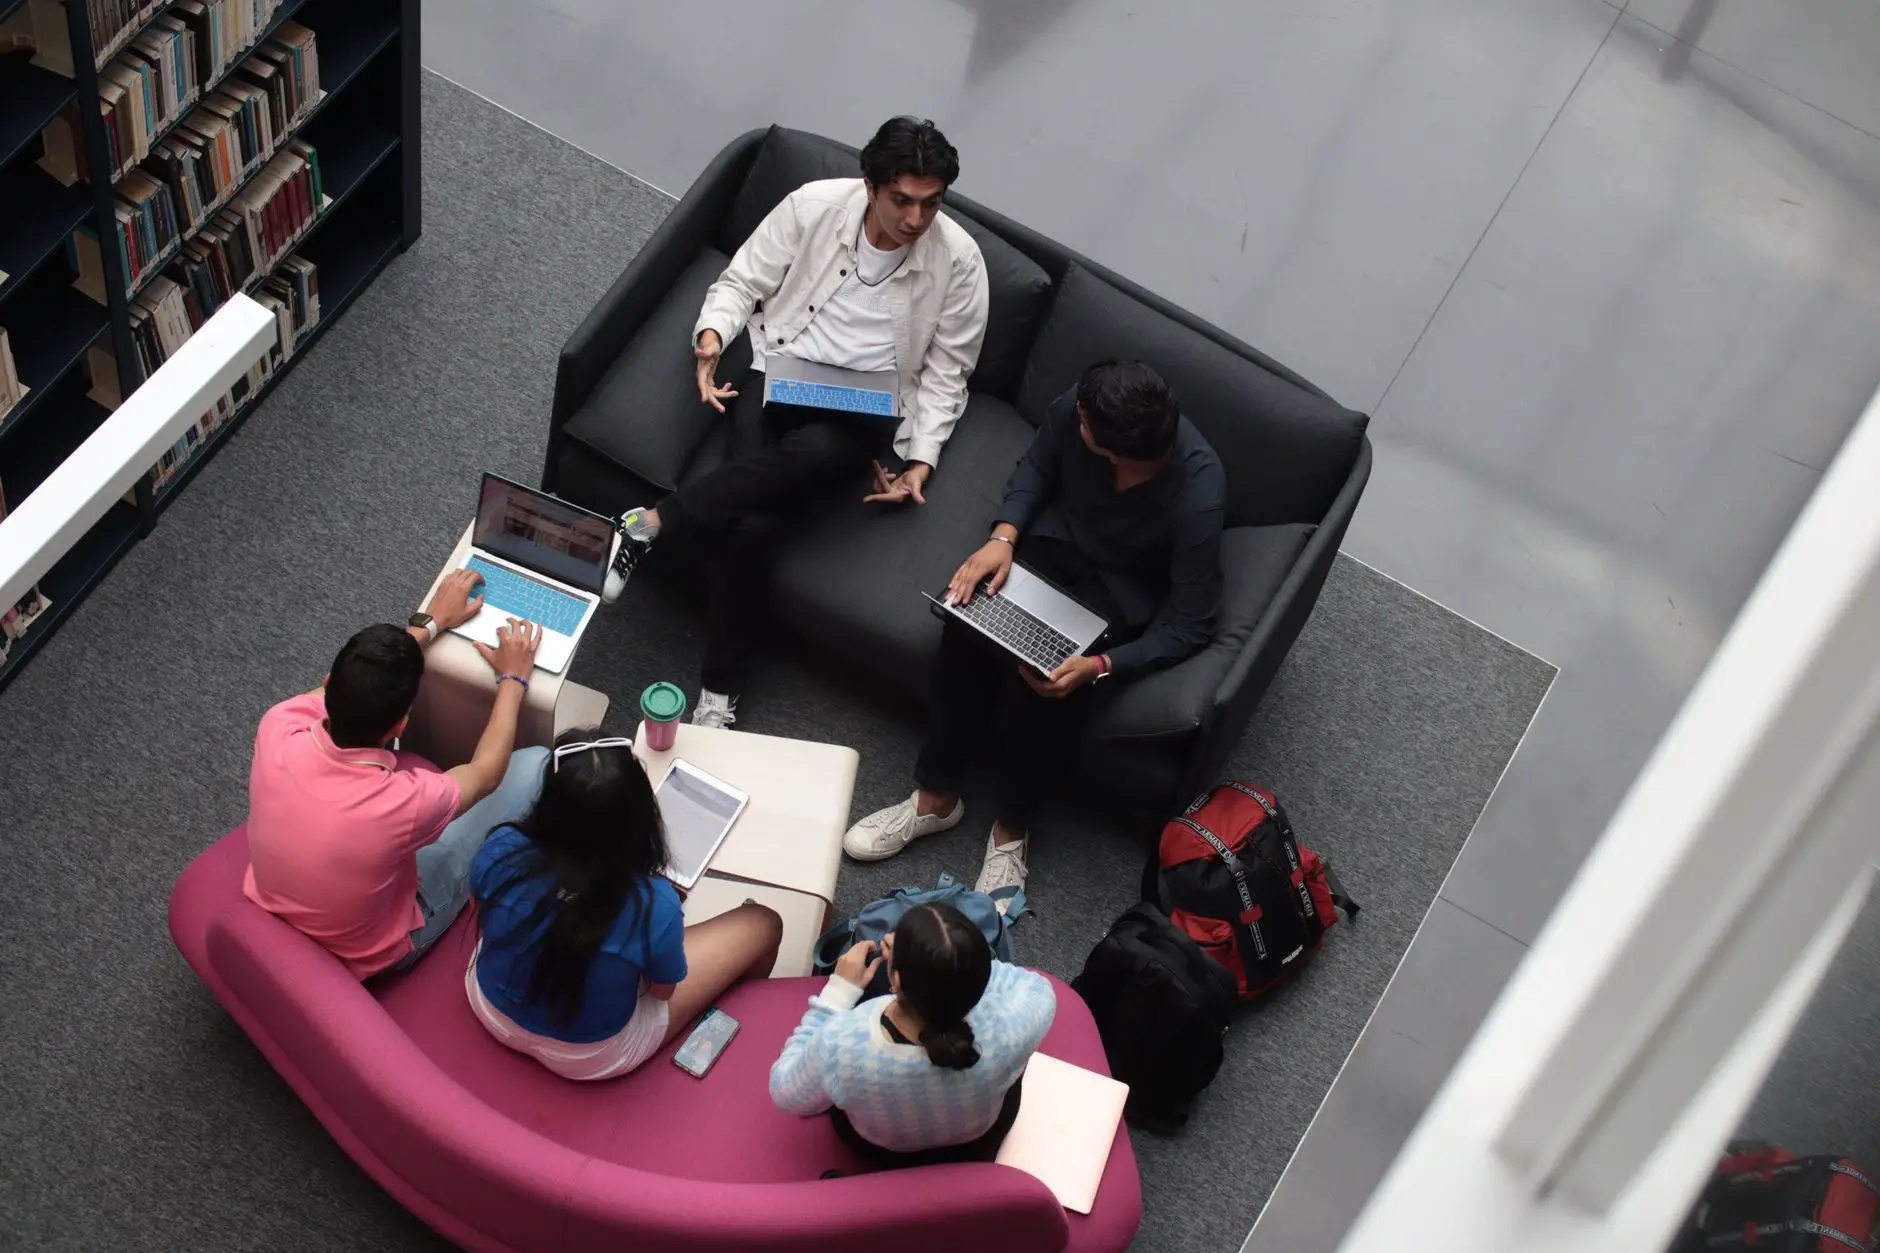
Higher education institutions operate as unique ecosystems. They function simultaneously as academic hubs, public enterprises, vast housing networks, and advanced research facilities. Because universities handle massive volumes of personal data, intellectual property, and financial records, they represent high-value targets for cybercriminals. To secure these assets, compliance teams and academic leaders must understand how regulatory frameworks interact with operational standards.
Achieving structural security requires more than basic IT defenses. When universities want to know ISO 27001 readiness, they must look deep into how administrative departments, research labs, and third-party vendors handle information assets. Building a resilient Information Security Management System (ISMS) protects institutional reputation and fulfills growing legal obligations.
The Unique Security Challenges Facing Higher Education
Universities face security dynamics that corporate enterprises rarely encounter. Open networks, academic freedom, decentralized department structures, and high staff turnover create continuous vulnerabilities. Research groups often share data globally with partner universities, grant agencies, and private corporations, complicating data protection protocols.
Furthermore, student information systems store sensitive demographics, financial aid applications, and medical records from campus clinics. A single unsecured server in a physics department can expose thousands of personal records. Security must balance protection with the open collaboration essential to academic inquiry.
What Is ISO 27001 and Why It Matters for Universities
Published by the International Organization for Standardization, ISO 27001 provides a globally recognized framework for establishing, implementing, maintaining, and continually improving an ISMS. Rather than prescribing rigid technical rules, the standard uses a risk-based approach tailored to an institution’s specific threat landscape.
For university leadership, adopting ISO 27001 brings clear advantages:
- Standardized Risk Management: Identifies vulnerabilities across disparate departments systematically.
- Grant Eligibility: Satisfies strict cybersecurity prerequisites required by government and defense research grants.
- Regulatory Alignment: Bridges the gap between security controls and privacy laws like GDPR or FERPA.
- Trust Building: Assures students, faculty, and international partners that data remains secure.
Mapping Privacy Readiness to ISO 27001 Controls
Privacy and information security are distinct yet deeply intertwined. Information security focuses on protecting data from unauthorized access, disruption, or destruction, while privacy focuses on the lawful, transparent handling of personal information. ISO 27001 addresses privacy readiness by integrating security controls that safeguard personal data throughout its lifecycle.
| ISO 27001 Domain | Higher Education Application | Privacy Impact |
|---|---|---|
| Asset Management | Cataloging student databases and research repositories. | Ensures all personal data locations are known and accounted for. |
| Access Control | Restricting administrative grades and clinical data. | Prevents unauthorized staff from viewing sensitive student records. |
| Supplier Relationships | Vetting cloud providers and educational software vendors. | Protects data shared with third parties under strict processing terms. |
| Incident Management | Detecting and reporting research data breaches quickly. | Meets regulatory reporting windows for compromised personal data. |
Real-World Scenario: Securing Collaborative Research
Consider a mid-sized university managing a multi-million-dollar medical research grant involving human genomic data. Without an ISO 27001 framework, different research labs might use unencrypted cloud drives, personal laptops, and insecure email chains to share files. If an external auditor or grant partner discovers these gaps, the university risks losing funding and facing severe compliance penalties.
By initiating ISO 27001 readiness assessments, the institution centralizes data governance. IT teams mandate multi-factor authentication, enforce encryption standards for all research endpoints, and train researchers on secure data-sharing practices. The result is a secure environment that satisfies grant requirements without hindering scientific progress.
Actionable Steps for University Compliance Teams
Embarking on an ISO 27001 journey can feel overwhelming for institutions accustomed to decentralized management. Compliance officers and IT directors can follow this practical checklist to build momentum:
- Secure executive buy-in from university presidents, provosts, and the board of trustees.
- Define the scope of the ISMS, determining whether to cover the entire institution or start with high-risk units like medical centers or administrative offices.
- Conduct a comprehensive asset inventory to map where personal data and intellectual property reside.
- Perform a formal risk assessment to identify threats, vulnerabilities, and potential impact levels.
- Establish clear policies for incident response, password management, and data retention.
- Engage external auditors for a gap analysis before pursuing official certification.
Frequently Asked Questions
Is ISO 27001 mandatory for all universities?
ISO 27001 is a voluntary standard. However, many funding bodies, government agencies, and industry partners increasingly mandate certification as a prerequisite for handling sensitive research and grants.
How long does ISO 27001 implementation take in higher education?
Due to decentralized structures and complex organizational cultures, full implementation typically takes between twelve to twenty-four months depending on the initial scope.
How does ISO 27001 support student privacy rights?
By enforcing rigorous access controls, data encryption, and secure disposal methods, ISO 27001 ensures that personal student and staff data remains protected against unauthorized exposure.
Conclusion
As cyber threats grow more sophisticated and regulatory expectations tighten, higher education institutions must evolve past informal security measures. Evaluating universities Know ISO 27001 Readiness provides a clear roadmap for protecting institutional assets, preserving research integrity, and safeguarding student privacy. Embracing structured information security ensures that universities remain safe havens for discovery and education in the digital age.









Leave a Reply