



How HR Teams Should Think About AI Governance Before Using AI Tools

Share
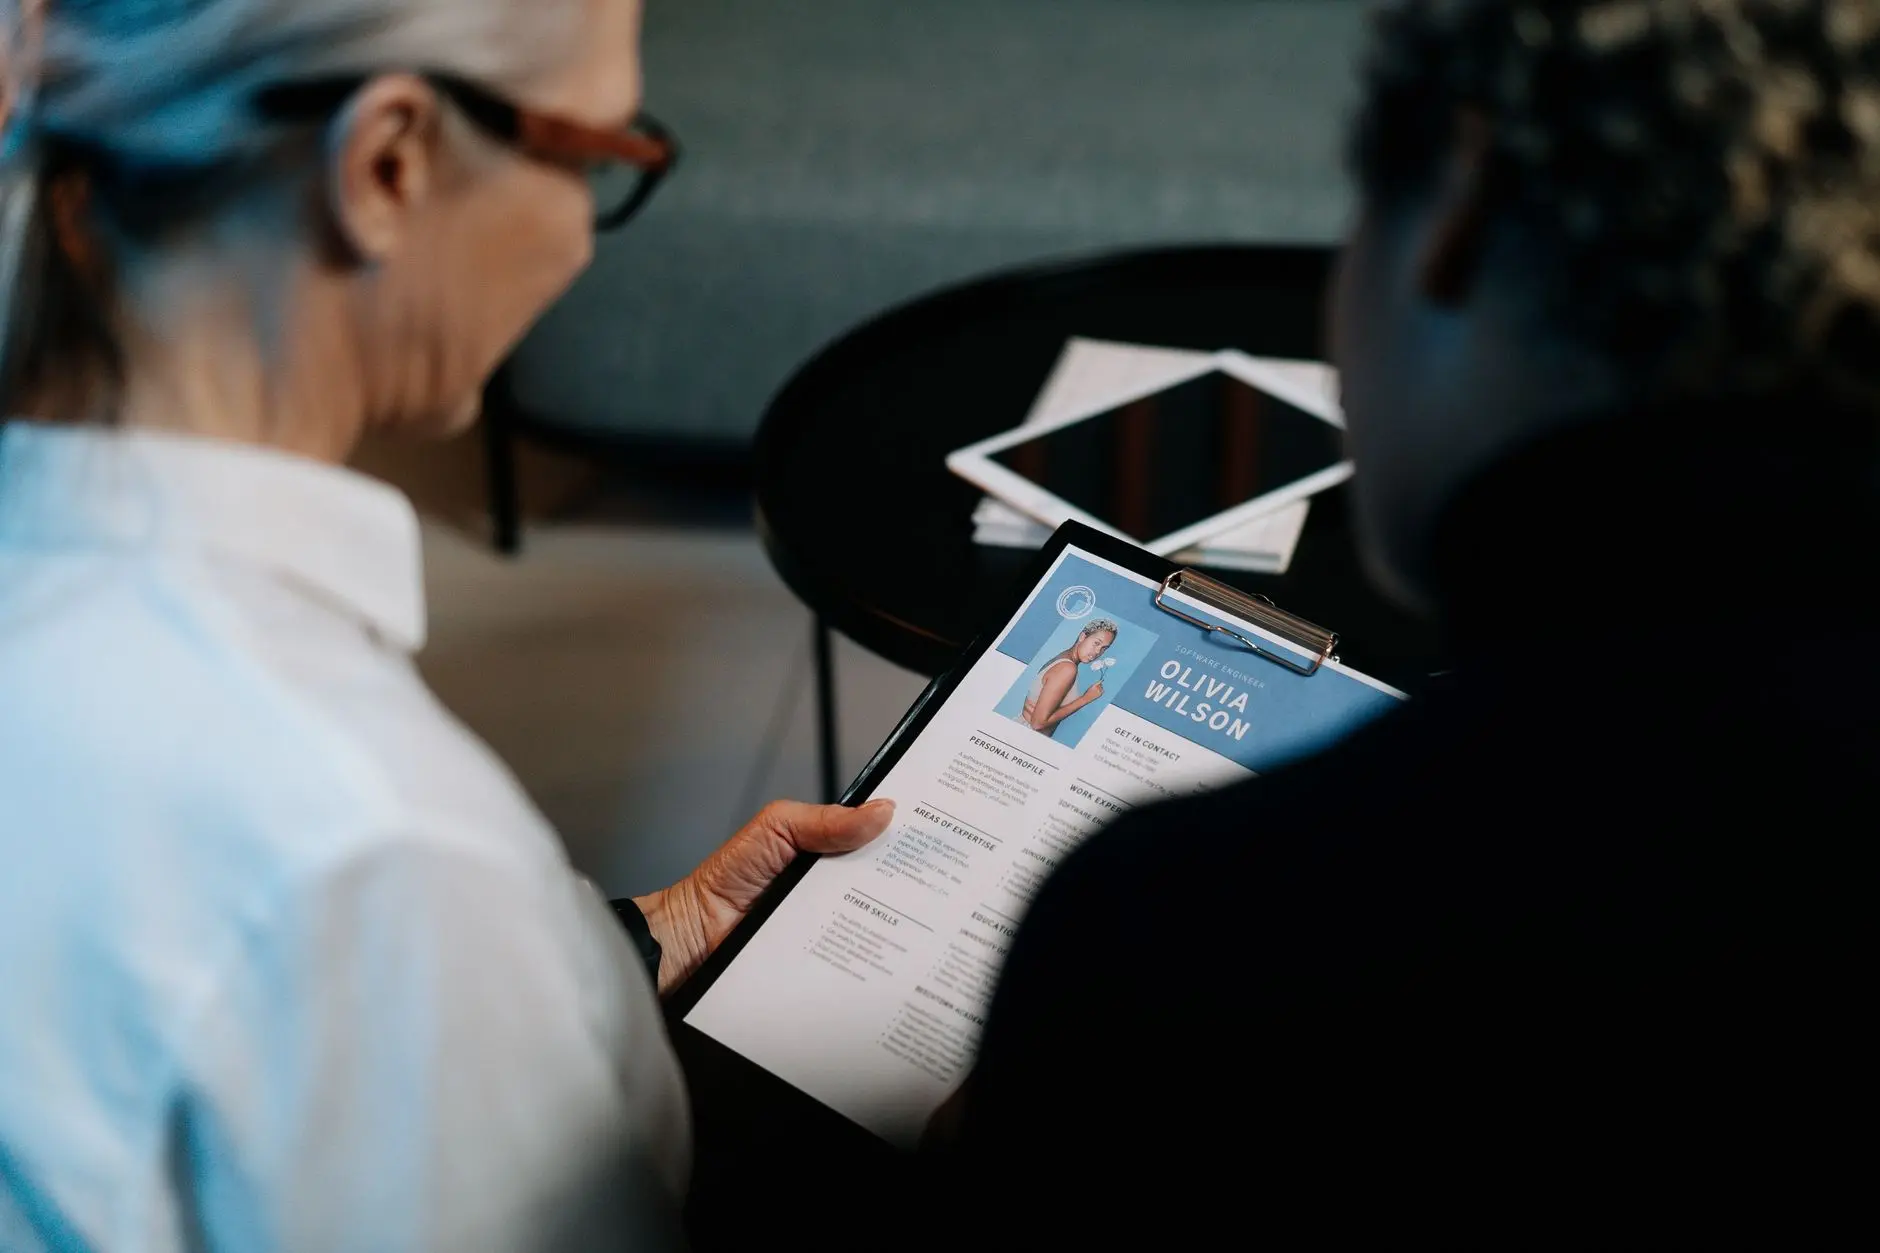
The Shift Toward Automated Hiring
Human resources departments are deploying artificial intelligence tools faster than ever. From automated resume screening and chatbot initial interviews to sentiment analysis during video assessments, technology promises unprecedented efficiency. Yet, before any software touches a candidate pool, HR teams think AI governance using structured frameworks that protect both organizational integrity and applicant rights. Rushing into deployment without rigorous oversight exposes companies to severe regulatory penalties, reputational damage, and discrimination lawsuits.
Under strict regulatory frameworks like the European Union Artificial Intelligence Act, employment and worker management systems are explicitly classified as high-risk applications. This means that human resources software does not just require standard operational testing. It demands documented compliance, transparent algorithmic logic, continuous monitoring, and strict adherence to data protection principles.
Understanding the Core Legal and Ethical Risks
When organizations rush to adopt machine learning without preparation, they frequently stumble into well-documented pitfalls. Recruitment algorithms learn from historical hiring data, which often contains decades of human bias. If a model evaluates past successful hires, it may inadvertently penalize candidates based on gender, age, ethnicity, or socioeconomic background. This turns systemic bias into automated discrimination.
Furthermore, processing candidate data through third-party cloud tools triggers strict obligations under privacy legislation. HR departments must ensure that candidate consent is valid, data minimization is practiced, and proper data processing agreements are in place. Ignorance of how a vendor algorithm works does not shield an enterprise from liability when a discriminatory output occurs.
How HR Teams Think AI Governance Using a Practical Framework
Building a defensible governance model requires cross-functional collaboration between human resources, legal counsel, IT security, and compliance officers. Rather than viewing technology as a plug-and-play solution, teams must evaluate every tool through a multi-layered risk assessment lens.
1. Inventory and Categorize All AI Tools
You cannot govern what you do not track. HR leaders must compile a comprehensive inventory of all software utilizing machine learning or automated decision-making. This includes resume parsers, performance evaluation predictors, and compensation benchmarking algorithms.
2. Enforce Human Oversight and Intervention
No automated tool should ever hold absolute authority over hiring, promotion, or termination decisions. A qualified human professional must review algorithmic recommendations. As noted by data protection authorities, meaningful human oversight is a legal requirement, not a suggestion.
3. Audit for Bias and Discrimination Regularly
Algorithm testing must be continuous. Independent third-party audits help detect disparate impact before discriminatory hiring patterns harm real applicants.
| AI Tool Type | Potential Risk | Governance Action Required |
|---|---|---|
| Resume Screening Software | Gender or ethnic bias from historical data | Regular disparate impact audits and diverse training data review |
| Video Interview Analyzers | Discrimination against neurodivergent candidates or accents | Strict validation, optional alternatives, and human-only review |
| Performance Predictors | Surveillance creep and privacy violations | Data minimization, clear notice, and employee consent policies |
Real-World Scenario: The Cost of Unvetted Tech
Consider a mid-sized technology firm that deployed an automated resume-ranking tool to manage thousands of incoming software engineering applications. Within six months, internal reviews revealed that the system systematically downgraded resumes containing specific women-led college organizations and non-traditional career paths. Because the HR department failed to establish governance protocols or test the vendor algorithm prior to deployment, the company faced regulatory investigations and severe public scrutiny regarding discriminatory hiring practices.
To avoid similar crises, modern organizations must integrate data protection principles directly into their recruitment pipelines from day one.
Key Questions HR Leaders Must Ask Vendors
Before signing any software contract, procurement and HR teams should demand transparency from technology vendors by asking critical questions:
- What specific datasets were used to train this machine learning model?
- How does the software handle data privacy requests, such as the right to erasure?
- Can the vendor explain how the algorithm reaches its scoring decisions?
- What indemnification provisions protect our organization if the tool produces biased outcomes?
“Artificial intelligence in the workplace is not merely an HR tech upgrade; it is a fundamental restructuring of worker rights and organizational accountability that demands proactive regulatory alignment.” – Privacy and Employment Law Researcher
Frequently Asked Questions
Is employee consent enough to deploy AI recruitment tools?
No. In an employment context, power imbalances mean consent is rarely freely given. Organizations must rely on legal bases other than consent, such as legitimate interests or contractual necessity, while strictly adhering to transparency obligations.
Are internal HR tools exempt from external regulations?
No. Whether a tool is built in-house or purchased from a third-party vendor, if it impacts workers or applicants within regulated jurisdictions, it must comply with applicable artificial intelligence and data protection laws.
Conclusion
Adopting technological solutions in the workplace offers remarkable efficiencies, but convenience must never outpace responsibility. When HR teams think AI governance using robust risk assessments, transparent vendor evaluations, and mandatory human oversight, they protect their candidates, their employees, and their organization’s long-term reputation.








Leave a Reply