

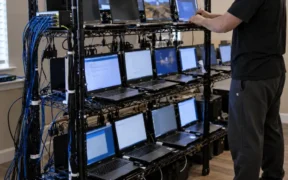
U.S. authorities have dismantled over 40 laptop farms and charged 14 individuals involved in a North Korean remote IT worker fraud scheme.
Billion-dollar companies are more than twice as likely to knowingly leave high or critical security vulnerabilities unpatched compared to smaller firms, according to new research from software supply chain security firm Chainguard.
SAP has released its October 2026 security updates, patching 20 vulnerabilities across multiple products. Among them is a maximum-severity OAuth2 Server-Side Request Forgery (SSRF) flaw in the Cloud SDK for Python, tracked as CVE-2026-89111, that
Several European retail companies, including Ahold Delhaize and The Foschini Group (TFG), have recently confirmed cyber incidents. H&M is investigating potential claims, while ASOS detailed a prior customer data breach.
Attackers are continuing to exploit critical gaps in multi-factor authentication (MFA) coverage, leveraging stolen credentials to compromise systems such as VPNs, RDP, and Windows logons that often remain protected by only a single password.











