



Oracle PeopleSoft Zero-Day Exploited by ShinyHunters is Three Flaws

Share
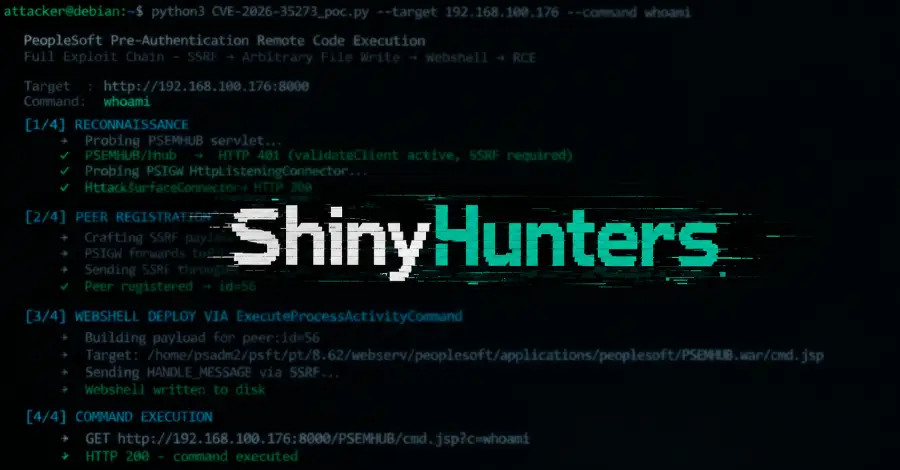
A critical zero-day vulnerability in Oracle PeopleSoft, which the ShinyHunters cybercrime group has actively exploited since May, has been identified as a chain of three distinct flaws rather than a single vulnerability. Cybersecurity researchers who reported the issues confirmed the new details this week.
Oracle addressed all three vulnerabilities in a single patch released in June, identifying the composite flaw as CVE-2026-35273. The root cause of the exploitation chain is a server-side request forgery (SSRF) vulnerability that allows attackers to reach an internal management interface because PeopleSoft is configured to trust its own loopback address.
The ShinyHunters group has been leveraging this unpatched weakness for months, indicating a sophisticated understanding of Oracle PeopleSoft’s internal architecture to bypass security controls. Oracle PeopleSoft is a suite of enterprise resource planning (ERP) software used by large organisations for functions such as human resources, finance, and supply chain management, making its security critical for maintaining business continuity and protecting sensitive data.
Organisations running affected versions of Oracle PeopleSoft applications should ensure they have applied all available security updates, particularly those released by Oracle in June, to mitigate the risk of ongoing exploitation. The presence of the SSRF vulnerability highlights common pitfalls in application design where internal network trust assumptions can create avenues for external compromise.












Leave a Reply