



uCreator Android Spyware Targets Telegram 2FA and WeChat Accounts

Share
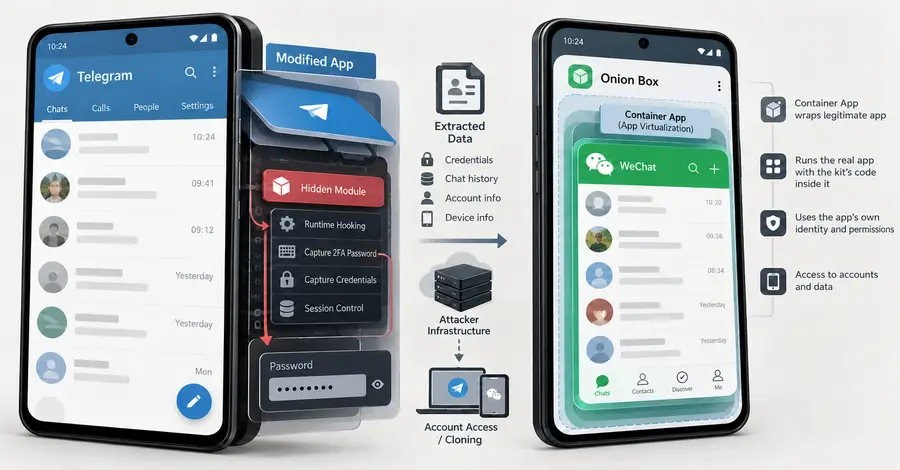
A new rentable Android spyware kit known as uCreator is being used to hijack Telegram and WeChat accounts by embedding malicious code within tampered versions of the messaging applications. The kit allows attackers to steal two-factor authentication (2FA) passwords and clone user accounts, posing a significant risk to digital identity and private communications.
According to findings from security researcher Ovi, the uCreator kit operates by hiding its malicious payload inside working copies of Telegram and WeChat. These infected versions are typically distributed through third-party websites and unofficial app stores rather than legitimate platforms like Google Play. Once installed, the spyware can intercept sensitive data directly from the compromised applications.
Telegram 2FA Theft and the Baohuo Connection
The Telegram component of the uCreator kit is designed to capture 2FA passwords, effectively bypassing one of the primary security layers intended to protect user accounts. Technical analysis indicates that this portion of the spyware shares significant code similarities with Baohuo, a known backdoor previously identified by security researchers at Doctor Web.
By leveraging this backdoor, attackers can gain unauthorised access to Telegram sessions, allowing them to monitor messages and potentially take over the account entirely. The reuse of Baohuo code suggests a refinement or rebranding of existing malware families to target specific messaging platforms more effectively.
WeChat Account Cloning and Container Apps
In addition to Telegram, uCreator specifically targets WeChat users. The spyware employs two distinct methods to compromise these accounts. In some instances, the malicious code is injected directly into a modified WeChat application. In others, the malware authors utilise a “container” app—a secondary environment that runs WeChat within the kit makers’ own software—to monitor activity and extract account data.
This container-based approach allows the spyware to clone WeChat accounts, giving attackers the ability to impersonate victims or access historical chat logs and contact lists without the user’s knowledge. This method is particularly effective at evading standard mobile security detections that only scan for modified APK files.
Risk Mitigation and Distribution
The primary infection vector for uCreator is the manual installation of tampered software. Users are typically lured into downloading these versions through social engineering or by seeking “modded” versions of apps that promise additional features not found in the official releases.
To mitigate the risk of uCreator and similar Android spyware, security experts recommend that users only download applications from official sources, such as the Google Play Store. It is also advised to verify that Google Play Protect is active on the device, as it provides a baseline defence against known malware signatures. Users who suspect their accounts may have been compromised should immediately terminate all active sessions within their Telegram or WeChat settings and reset their 2FA credentials.










Leave a Reply