

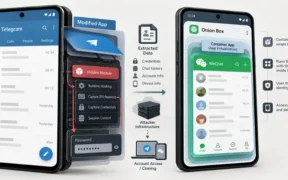
Researchers have identified uCreator, a rentable Android spyware kit that steals Telegram 2FA codes and clones WeChat accounts through tampered apps.
The RatHat Android banking trojan has evolved into a sophisticated malware-as-a-service operation, using Google Gemini to rank high-value victims and navigate banking apps.

MantaxOtax is a dual-threat Android malware that uses ransomware to encrypt files and spyware to steal sensitive data, including SMS and WhatsApp messages.

The Gigabud Android banking trojan uses cloned work profiles to isolate banking apps, allowing fraudsters to bypass detection and execute transactions on seemingly clean devices.












