



PHP Issues Fresh Windows Security Update to Fix Brotli Code Execution Flaw

Share
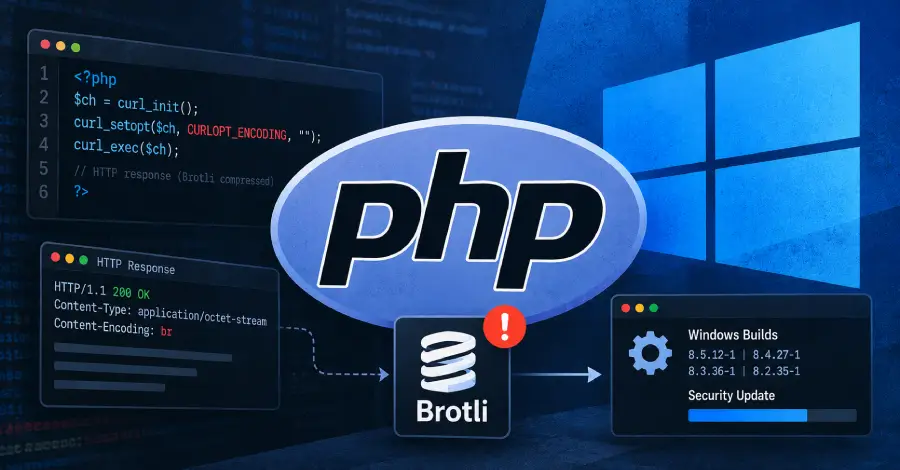
The PHP project has rebuilt its official Windows distribution packages for PHP versions 8.2 through 8.5 to address a memory corruption vulnerability in the bundled Brotli compression library.
Tracked as CVE-2026-111497, the flaw could allow a remote attacker to corrupt system memory and potentially execute arbitrary code. The patch represents the second Windows security update released for the runtime environment within five days.
cURL Extension Vector
The PHP development team indicated that the vulnerability can be reached when the cURL extension automatically decompresses HTTP responses carrying compressed Brotli payloads. By default, automatic response decompression remains turned off in cURL, limiting exposure to systems where developers have explicitly enabled the functionality.
Because official PHP binaries for Windows package third-party dependencies directly alongside the core runtime, Windows installations must be updated using the rebuilt binaries to ensure the fixed Brotli library is deployed.
System administrators and software developers relying on PHP on Windows platforms should apply the updated builds available through the official PHP downloads portal. Systems running Linux or custom-compiled versions should verify that the underlying system Brotli software library is patched to a secure version.











Leave a Reply