

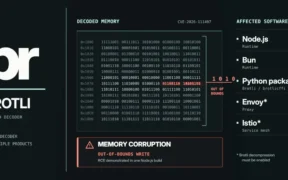
A memory-corruption flaw in Google’s Brotli decoder has been identified, impacting Node.js, Bun, and Python packages. The vulnerability could lead to remote code execution through maliciously crafted compressed data.

CISA has added critical vulnerabilities in Collabora Online Built-in CODE Server and Arista VeloCloud Orchestrator to its Known Exploited Vulnerabilities catalogue following evidence of active exploitation.
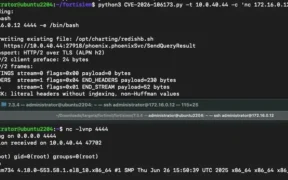
A public exploit has been released for a critical unauthenticated remote code execution flaw impacting Fortinet FortiSIEM.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a critical warning regarding a pre-authentication remote code execution (RCE) vulnerability in MikroTik RouterOS. Tracked as CVE-2026-84411, the flaw allows unauthenticated attackers to gain root
Google Threat Intelligence Group (GTIG) research indicates that vulnerabilities identified with AI assistance are significantly more prone to enabling remote code execution (RCE). Disclosures and exploitation have seen a rapid acceleration in 2026, with AI












