



Critical Cisco Secure Email Gateway Zero-Day Under Active Exploitation

Share
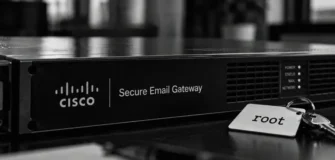
Cisco has warned that a critical zero-day vulnerability affecting its Secure Email Gateway appliances is being actively exploited in the wild. The flaw, identified as CVE-2026-76461, allows unauthenticated attackers to execute arbitrary commands on the underlying operating system with root privileges.
The vulnerability, which carries a CVSS score of 9.8, stems from an email parsing issue within the AsyncOS software. Attackers can trigger the exploit by sending a specially crafted email containing malicious SQL statements to a targeted user.
Affected Systems and Scope
The security hole affects both the physical and virtual versions of the Cisco Secure Email Gateway in any configuration. Cisco has confirmed, however, that the Secure Email and Web Manager and the Secure Web Appliance are not impacted by this vulnerability.
Cisco warned that because threat actors can obtain root privileges, they may be able to remove or hide indicators of compromise (IoCs) to cover their tracks during an intrusion.
CISA Response and Remediation
The US Cybersecurity and Infrastructure Security Agency (CISA) added the flaw to its Known Exploited Vulnerabilities (KEV) catalogue on Monday. CISA has instructed federal organisations to remediate the vulnerability by 17 September 2026.
Cisco’s Product Security Incident Response Team (PSIRT) became aware of the exploitation in September 2026. While the company has released indicators of compromise, the specific threat actors responsible for the attacks remain unknown.
This incident follows recent warnings regarding other Cisco vulnerabilities, including flaws in the Secure Firewall Management Center (FMC) that were exploited by both state-sponsored hackers and cybercriminals.









Leave a Reply