



Persistent AI Coworkers Break Enterprise Identity Security Models

Share
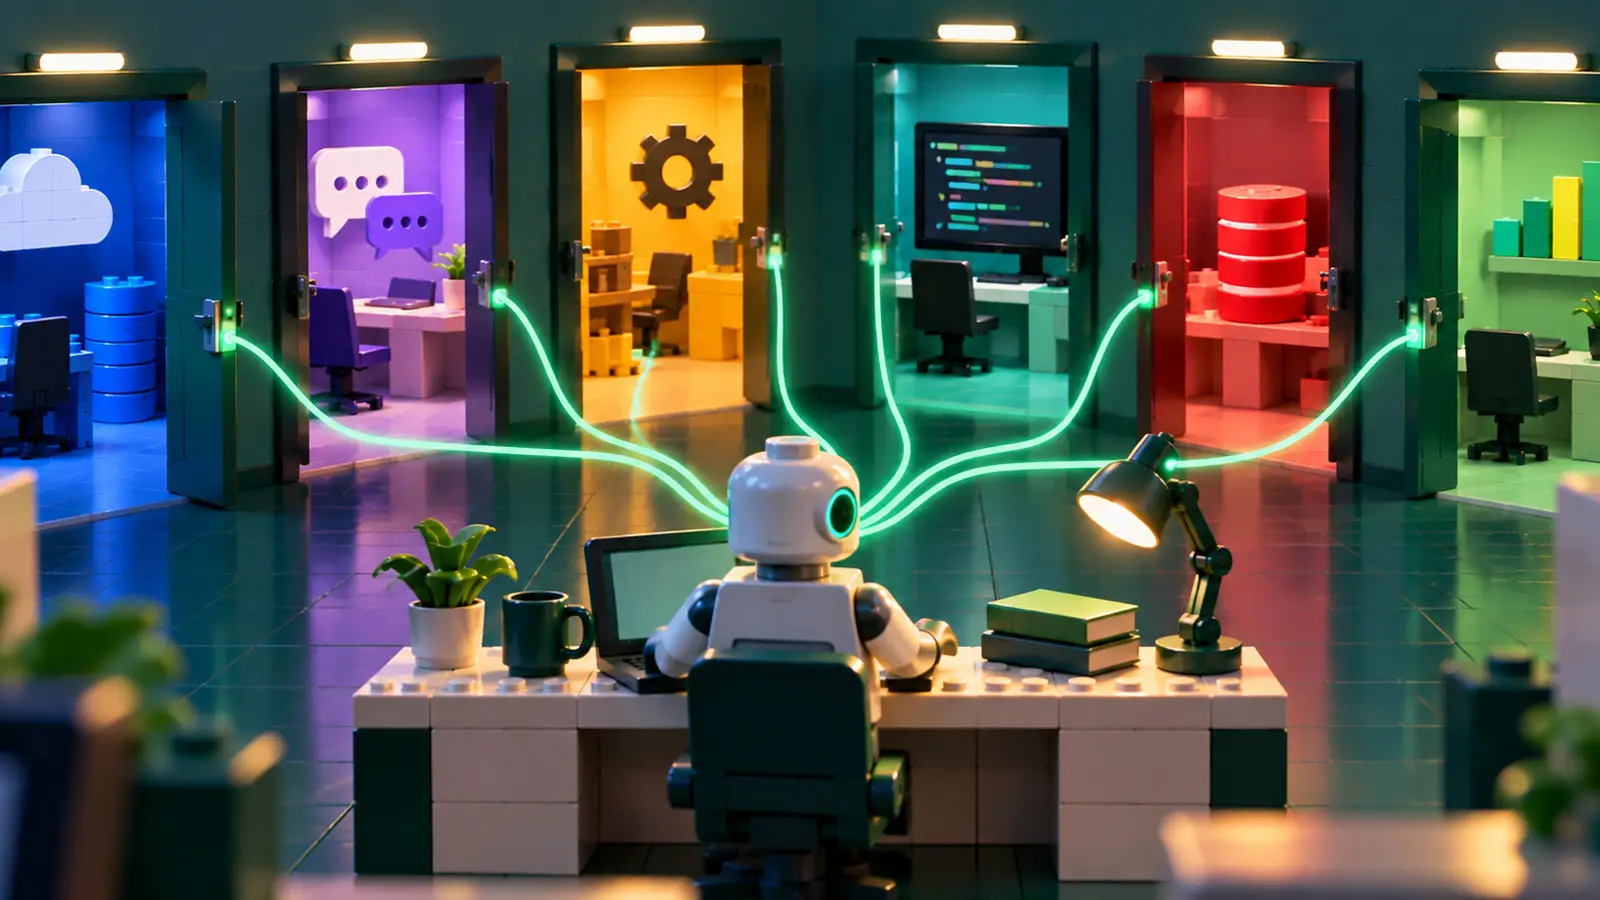
The emergence of persistent artificial intelligence (AI) agents operating as "digital colleagues" is rapidly challenging fundamental identity and access management (IAM) security models in organisations. According to cybersecurity firm Token Security, whose Co-Founder and CEO Itamar Apelblat has highlighted this shift, these AI "coworkers," designed for continuous operation and independent action, often inherit human credentials, creating significant risks that current security frameworks are ill-equipped to handle.
Traditional AI security has evolved through distinct waves. The first involved session-scoped chats, where the primary risk was the AI’s output. This progressed to task-scoped agents, where the focus shifted to the actions the AI performed, often with a human-in-the-loop. The impending "third wave" removes the human from continuous oversight, leaving AI agents with persistent access that behaves like a standing privilege.
Apelblat warns that this shift makes it crucial for organisations to adapt their security approaches. Unlike simpler agents that borrow credentials temporarily, persistent AI coworkers necessitate their own identities, designated human owners, precisely scoped permissions, and robust lifecycle controls.
The Challenge of Persistent AI Coworkers
Currently, many widely deployed AI agent platforms, including those from Anthropic and OpenAI, do not issue agents dedicated credentials. Instead, they rely on mechanisms such as OAuth grants, in-session hand-offs, or service accounts, often placing humans as the primary entity in audit trails. Developers might hand an agent a static bearer token via APIs, but this falls short of a proper, manageable identity.
This reliance on borrowed human credentials leads to several critical security vulnerabilities:
- Standing Privileges: An AI coworker’s continuous access effectively becomes a standing privilege, similar to a human’s, but without the same oversight mechanisms.
- Access Creep: Over time, persistent agents accumulate access from various projects. While a long-standing problem for human identity governance, this will be exacerbated for machines due to the speed of accumulation and an agent’s propensity to utilise all granted access, potentially combining minor grants into an unintended broad reach.
- Tainted Audit Logs: When an AI agent acts under user-granted privileges, audit trails typically record the human user as the actor, making security investigations and attribution extremely difficult.
- Human Burden and Risk: The expectation for humans to confirm sensitive actions frequently is both inefficient and a security risk due to attention fatigue.
Industry leaders acknowledge the need for agents to access company resources to be effective. Tara Seshan, who leads product for ChatGPT Work and Codex at OpenAI, has highlighted in August 2026 that an agent’s utility largely depends on its access to data, cloud infrastructure, and reliability, akin to a human colleague needing access to essential work tools. She also described agents spawning sub-agents and collaborating, which further underscores the need for distinct identity models.
While Google demonstrated a Workspace agent named "Chip" with its own Workspace account, role, and permissions at I/O in May 2024, such a model has not been widely deployed. Instead, most current offerings involve agents inheriting human authority.
New Approaches to AI Identity
Some identity platform vendors have begun to adapt. Microsoft has introduced Entra Agent ID for first-class agent identities with human sponsors, and Okta has added agent identities to its Universal Directory with short-lived, scoped tokens. SailPoint and CyberArk also offer comparable solutions, though these are often confined to their own vendor ecosystems.
For platform-agnostic security, identity controls remain the de facto checkpoint for policy enforcement. Organisations should take proactive steps to secure their AI coworkers:
- Detect Shadow Coworkers: Identify unregistered agents by monitoring authentication traffic.
- Assign Unique Identities: Provide every persistent agent with its own distinct identity. This is essential for distinguishing AI actions from human actions in audit logs.
- Establish Human Ownership: Assign a human owner to each agent to prevent orphaned agents with live credentials.
- Scope Access Precisely: Grant access directly to the agent based on its specific job function, not the broader permissions of the human who launched it.
- Implement Lifecycle Controls: Define clear expiration conditions, such as team disbandment or an employee’s departure, or an idle period after which the agent’s access automatically expires.
This "third wave" of AI demands a fundamental shift in how organisations approach digital identity and access management. Securing these new digital colleagues requires giving them their own "badges" – distinct, manageable identities – before they are given their jobs.












Leave a Reply