



What SMEs Know NDPA and Data Privacy: A Practical Guide

Share
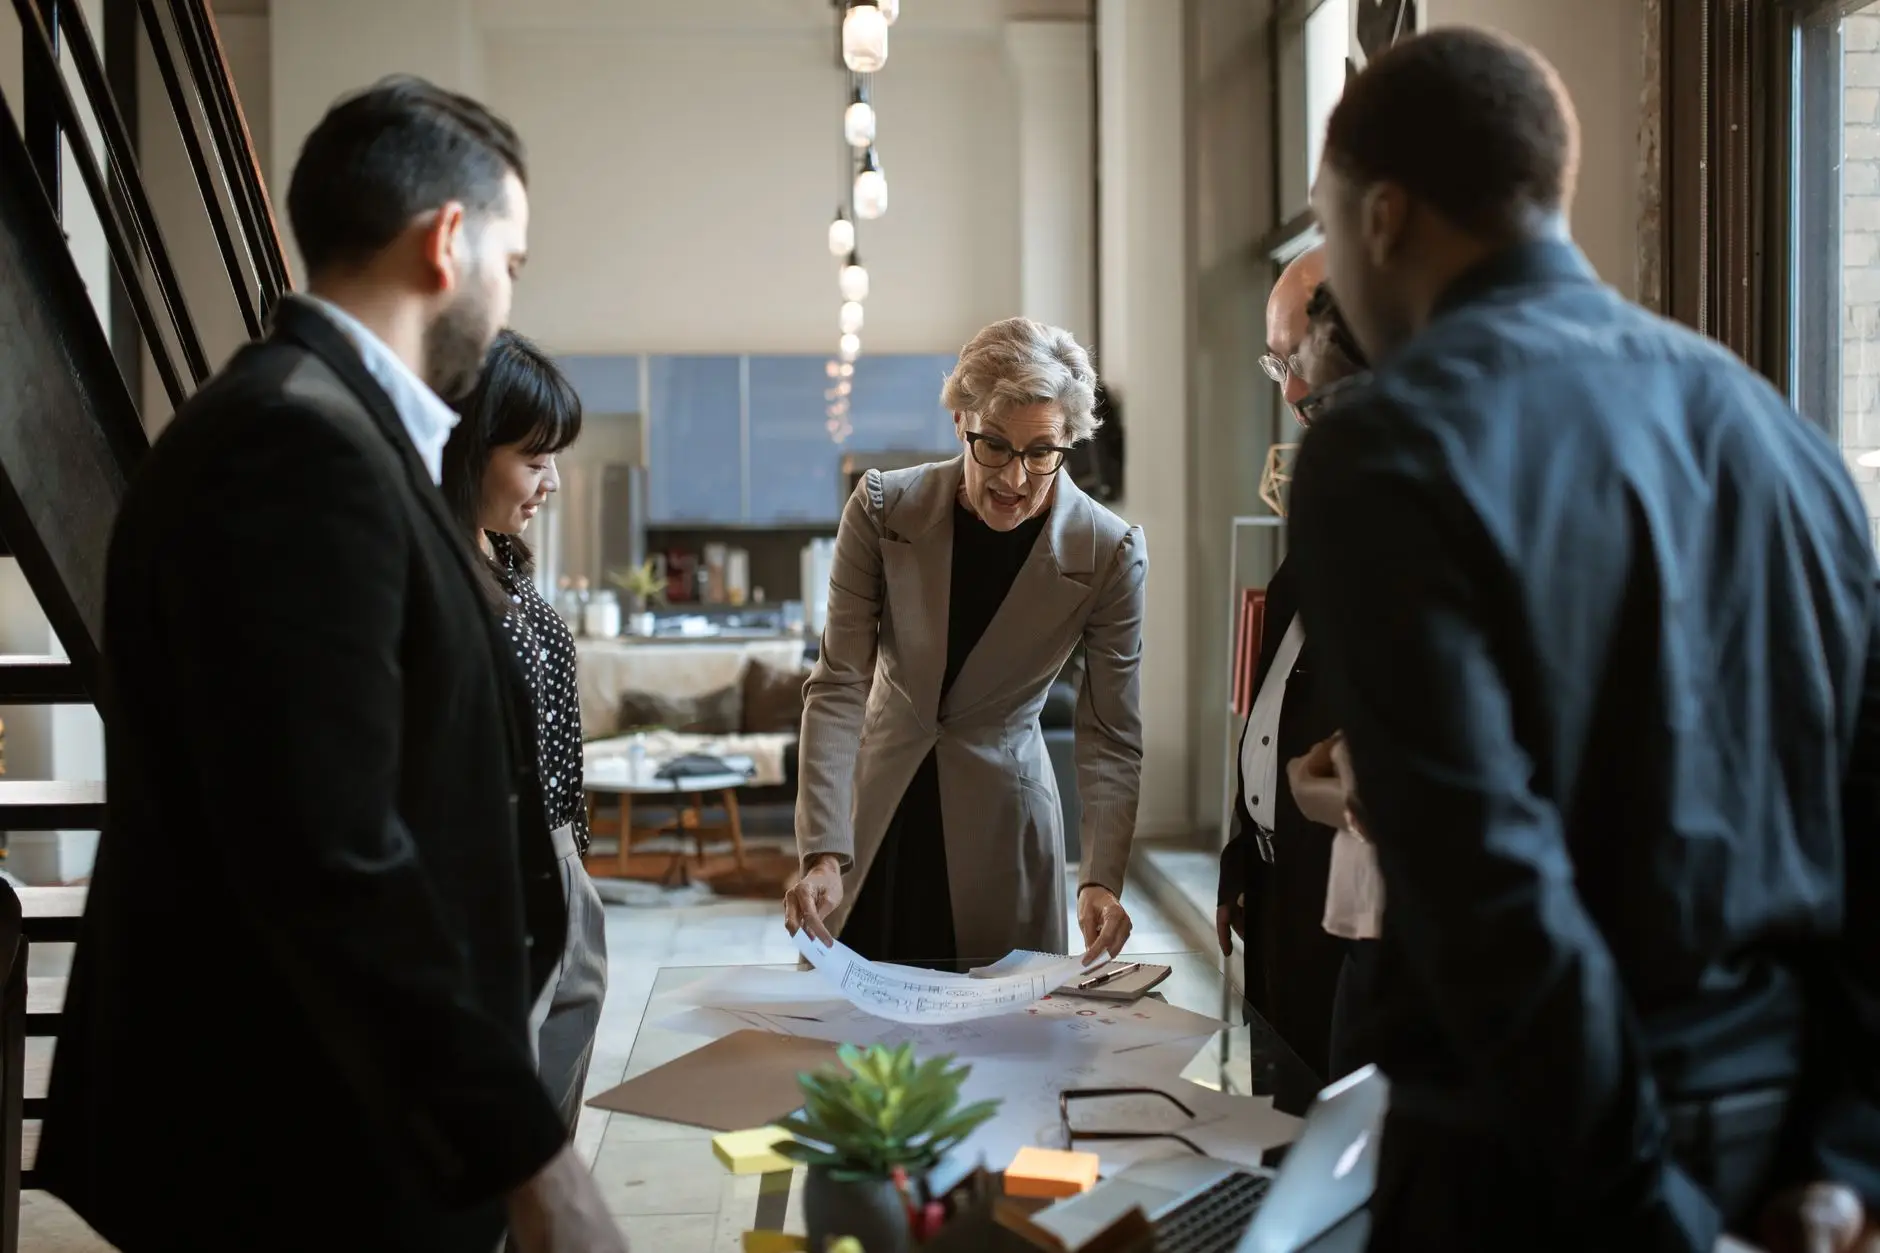
Small and medium-sized enterprises often assume that stringent data privacy laws only apply to large multinational corporations with sprawling legal departments. However, modern legislative frameworks, including the Nigeria Data Protection Act, apply to any organization processing the personal data of data subjects, regardless of company size. When examining what SMEs Know NDPA obligations, business leaders frequently discover that compliance is not just a legal checkbox, but a core pillar of operational trust.
Regulators across emerging digital markets are ramping up enforcement. According to reports from data protection authorities, thousands of organizations handle customer records, employee profiles, and digital identifiers daily. Without structured data protection practices, a single overlooked vulnerability can trigger severe financial penalties and reputational damage that halts business growth.
Understanding the Core Obligations Under the NDPA
The Nigeria Data Protection Act establishes a comprehensive framework for safeguarding personal information. For growing businesses, understanding these legal mandates prevents costly missteps. Compliance begins with recognizing that data ownership rests with the individual, while companies act merely as custodians.
Business leaders must establish lawful bases for processing personal data. Whether collecting customer email addresses for a newsletter or processing payroll details for staff, every data collection point requires explicit consent, contractual necessity, or legal obligation. Ignoring these principles exposes enterprises to regulatory investigations.
Practical Real-Life Scenario: The E-Commerce Oversight
Consider a mid-sized online retail startup that collects customer shipping addresses, phone numbers, and payment preferences. The firm stores this data on an unencrypted cloud server to save costs. When a routine security audit reveals the oversight, the company faces potential scrutiny from the Nigeria Data Protection Commission. By implementing basic encryption and drafting a clear privacy policy, the founders transform a massive liability into a compliant, trustworthy e-commerce operation.
Key Requirements Every Business Leader Must Address
Translating legislation into daily business operations requires a clear roadmap. Founders and compliance officers should focus on foundational steps that directly address regulatory scrutiny.
- Data Mapping: Identify where personal information enters, travels through, and exits your organization.
- Privacy Notices: Provide transparent, easy-to-understand notices informing customers how their data is used.
- Data Subject Rights: Establish reliable workflows to handle requests for data access, correction, or deletion.
- Vendor Risk Management: Ensure third-party software providers and contractors adhere to strict data security standards.
Comparison of Compliance Approaches for SMEs
| Approach | Key Action | Risk Level |
|---|---|---|
| Reactive | Addressing privacy only after a breach or complaint occurs. | High Financial and Reputational Risk |
| Proactive | Conducting data audits and training staff regularly. | Low Risk and High Consumer Trust |
Expert Perspective on Regulatory Enforcement
As regulatory bodies increase oversight, industry experts emphasize that compliance must evolve alongside technological innovation. Dr. Vincent Olatunji, National Commissioner of the Nigeria Data Protection Commission, has repeatedly noted that data privacy is vital for sustainable economic development, stating that trust is the ultimate currency in the digital economy.
Compliance is no longer an optional corporate luxury. It is the baseline requirement for entering modern digital markets and retaining consumer confidence.
For resource-constrained teams, starting small yields significant results. Appointing an internal data protection champion, conducting a simple data inventory, and securing customer databases form the foundation of a robust privacy program.
Frequently Asked Questions
Does the NDPA apply to micro-enterprises with fewer than ten employees?
Yes. The law applies to any entity processing personal data within its jurisdiction, regardless of employee headcount. While compliance obligations scale with the volume and sensitivity of data processed, no business is entirely exempt.
What are the penalties for non-compliance?
Penalties can include substantial financial fines, public reprimands, and mandatory operational audits by the regulator, depending on the severity of the data infraction.
Conclusion
Mastering what SMEs Know NDPA compliance entails allows growing businesses to protect their bottom line while building enduring customer loyalty. By treating data privacy as an operational asset rather than a bureaucratic hurdle, business leaders position their enterprises for sustainable success in a privacy-first world.












Leave a Reply