

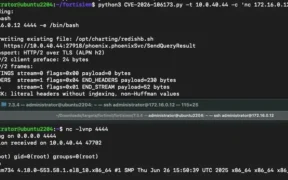
A public exploit has been released for a critical unauthenticated remote code execution flaw impacting Fortinet FortiSIEM.
Billion-dollar companies are more than twice as likely to knowingly leave high or critical security vulnerabilities unpatched compared to smaller firms, according to new research from software supply chain security firm Chainguard.
Attackers are continuing to exploit critical gaps in multi-factor authentication (MFA) coverage, leveraging stolen credentials to compromise systems such as VPNs, RDP, and Windows logons that often remain protected by only a single password.
Many Chief Information Security Officers (CISOs) struggle to confidently answer board questions regarding an organization's overall security posture, financial exposure, and improvement trends. This challenge stems from fragmented security data across numerous tools that lack
Persistent AI agents, acting as "digital colleagues," are challenging traditional identity and access management. This "third wave" of AI demands dedicated identities, scoped permissions, and robust lifecycle controls to prevent new security risks.












