



What Public Agencies Should Know About NDPA and Data Privacy

Share
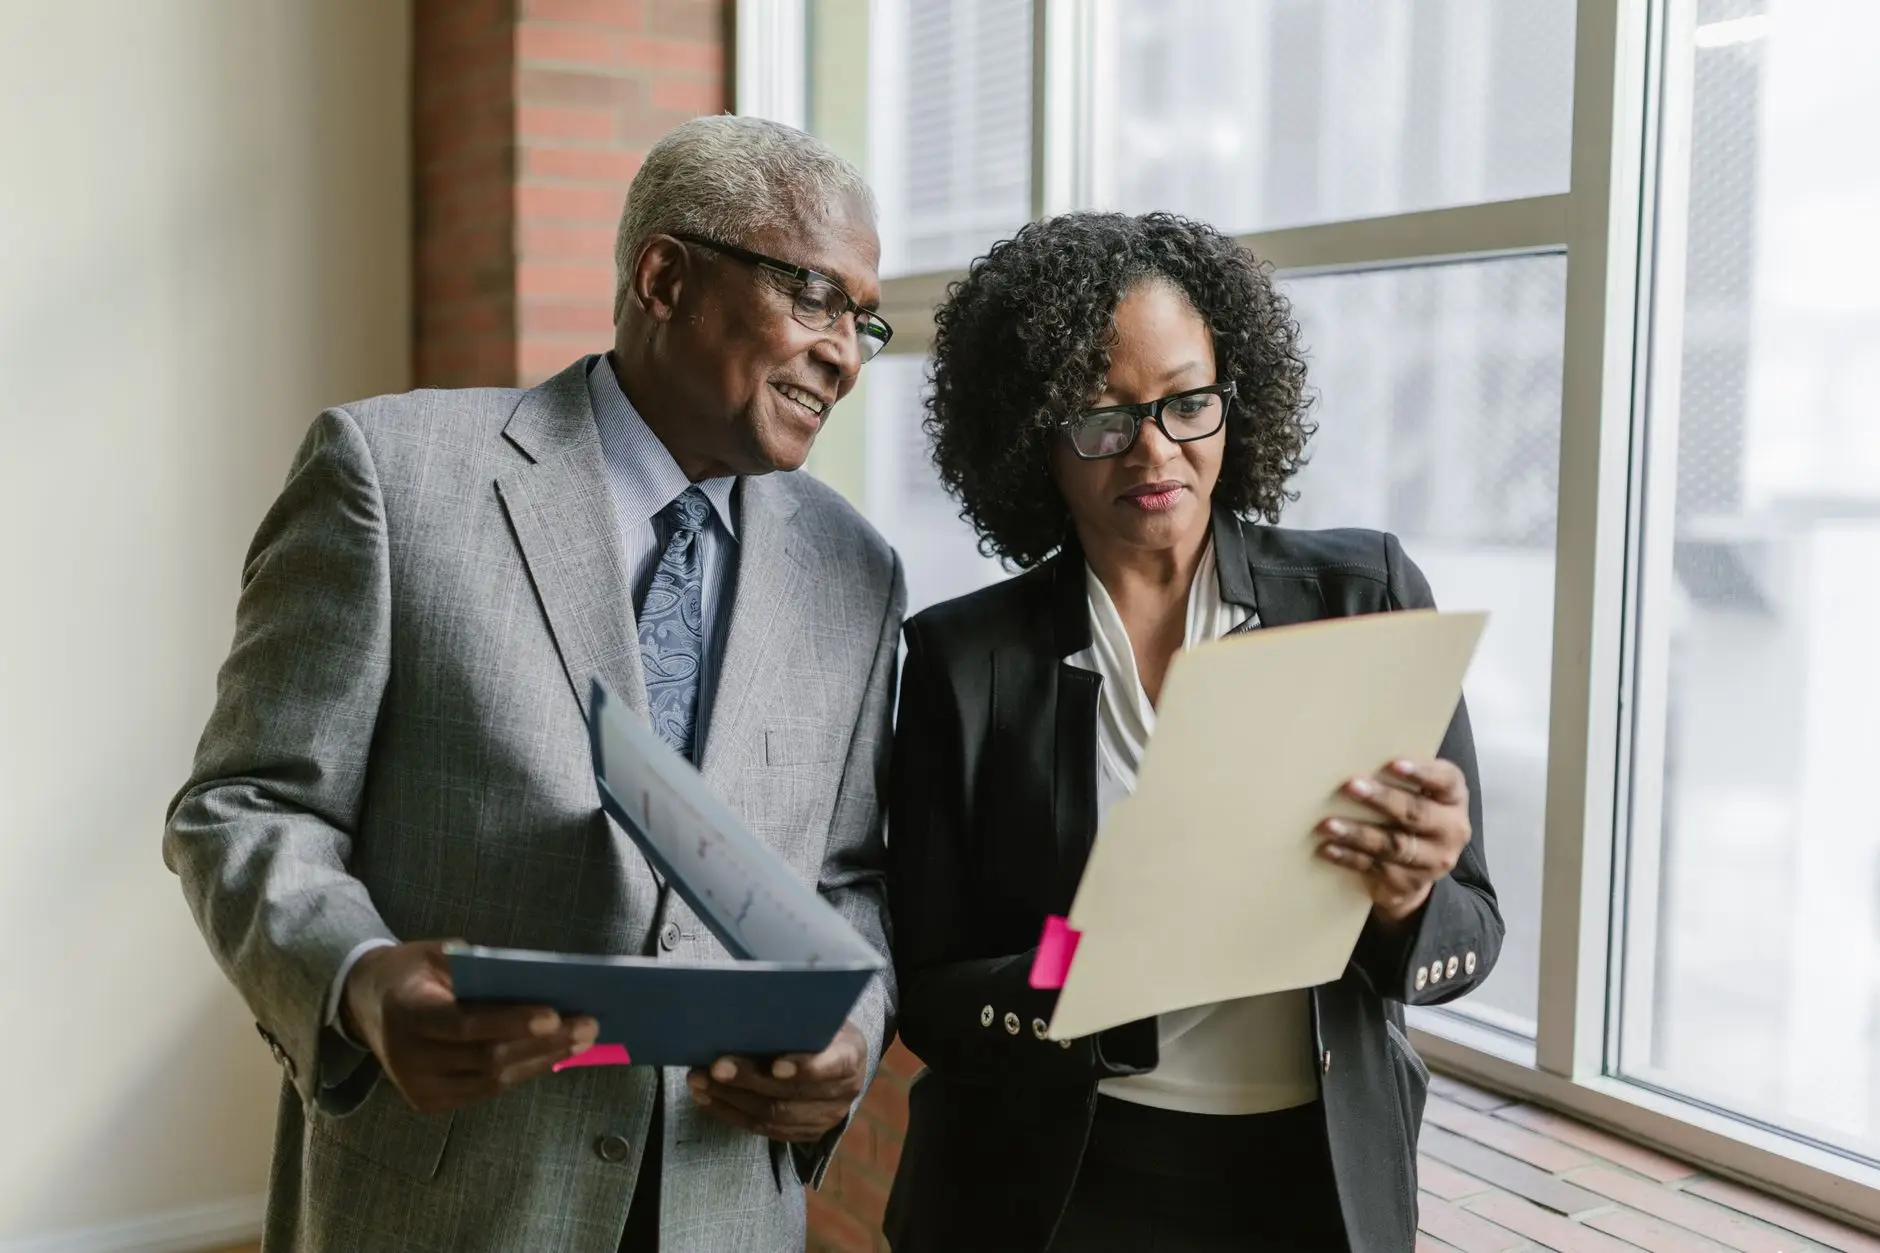
Government institutions and public sector organizations collect, process, and store massive volumes of citizen data every single day. From tax records and civil registry entries to healthcare databases and social welfare applications, public sector bodies represent the largest data controllers in many jurisdictions. Because of this monumental responsibility, legislative frameworks like the Nigeria Data Protection Act (NDPA) and similar global standards apply strictly to government bodies just as they do to private enterprises.
Many government officials assume that public service exemptions apply to statutory data collection. However, modern privacy laws demand strict accountability, transparency, and robust security safeguards from every entity handling personal information. Understanding these statutory obligations is no longer optional for civil servants, agency directors, and IT procurement teams.
Why Public Agencies Must Prioritize NDPA Compliance
When citizens interact with public agencies, they share sensitive data out of legal necessity, not commercial choice. This power imbalance heightens the ethical and legal duty of care required from government offices. Under data protection regulations, public sector bodies must demonstrate lawful processing grounds, implement technical security measures, and respect the fundamental rights of data subjects.
Failing to secure citizen databases can result in severe institutional embarrassment, loss of public trust, and administrative penalties imposed by regulators like the Nigeria Data Protection Commission. Furthermore, data leaks in public registries expose vulnerable citizens to identity theft, financial fraud, and targeted scams.
Core Data Protection Principles for Government Bodies
Compliance begins with embedding core data protection principles into daily agency operations. Public agencies must operationalize specific statutory requirements across all departments:
- Lawfulness and Fairness: Collecting personal data only when authorized by statutory mandate or explicit public interest grounds.
- Purpose Limitation: Using citizen data strictly for the specific administrative purpose for which it was originally gathered.
- Data Minimization: Gathering only the exact personal information required to execute a specific public service or administrative duty.
- Storage Limitation: Retaining citizen records only as long as necessary to satisfy legal retention schedules or public archiving laws.
- Integrity and Confidentiality: Deploying robust cybersecurity controls, encryption, and access permissions to protect databases from unauthorized access.
Key Requirements Every Public Agency Must Meet
Transitioning from traditional paper-based record keeping to modern digital governance requires structured administrative and technical controls. Public agencies must implement the following framework to ensure full regulatory alignment.
| Compliance Requirement | Operational Action | Responsible Department |
|---|---|---|
| Data Protection Officer (DPO) | Appoint a certified DPO to oversee compliance and liaise with regulators. | Executive Management |
| Data Protection Impact Assessment (DPIA) | Conduct DPIAs before deploying new surveillance or citizen database systems. | ICT and Legal Units |
| Vendor Risk Management | Audit third party software vendors and cloud service providers handling public data. | Procurement and IT |
| Data Subject Access Rights | Establish clear workflows for citizens requesting access to or correction of records. | Public Relations and Legal |
Real-Life Scenario: The Cost of Overlooking Citizen Privacy
Consider a hypothetical state health agency that launches a digital portal to track public vaccination records. Eager to deploy the service quickly, the agency neglects to conduct a proper security audit or data protection impact assessment. Within weeks, misconfigured cloud storage exposes the names, home addresses, and medical history of two million residents.
Beyond the immediate regulatory investigation, the agency faces intense public backlash, loss of citizen participation in public health initiatives, and costly emergency remediation expenses. This scenario illustrates why compliance must be baked into every digital transformation project from day one.
Actionable Steps for Agency Leaders
Public sector executives and IT managers looking to secure their operations against regulatory breaches should follow a structured roadmap:
- Conduct a Comprehensive Data Audit: Map every database, spreadsheet, and physical filing system across the agency to identify what personal data exists and where it flows.
- Update Privacy Notices: Ensure every digital portal, website, and paper form features a clear privacy notice explaining how citizen data is collected and used.
- Train Civil Servants: Mandate annual data protection and data protection training for all administrative staff and IT personnel.
- Establish Incident Response Plans: Create a rapid notification protocol to report data breaches to regulators and affected individuals within statutory timeframes.
Public trust is the ultimate currency of governance. When citizens surrender their personal information to the state, they expect absolute fidelity, security, and respect for their privacy rights.
Frequently Asked Questions
Are public agencies exempt from privacy laws?
No. While public agencies process data in the public interest, data protection laws explicitly cover government bodies, requiring them to safeguard personal data and respect citizen rights.
Do public agencies need to appoint a Data Protection Officer?
Yes. Because public authorities process large volumes of sensitive citizen data on a regular basis, appointing a qualified DPO is typically a mandatory legal requirement.
What happens if a public agency suffers a data breach?
The agency must investigate the incident, mitigate the exposure, and notify the regulatory commission as well as affected data subjects in accordance with statutory reporting rules.
Conclusion
Adhering to data protection laws is not merely a bureaucratic hurdle for government offices. It is a fundamental pillar of modern democratic governance. By understanding what public agencies know NDPA mandates, institutional leaders can build resilient digital systems, protect vulnerable citizen data, and foster enduring public trust in the digital age.












Leave a Reply