



How Policy Changes Affect Universities and Higher Education Data Compliance

Share
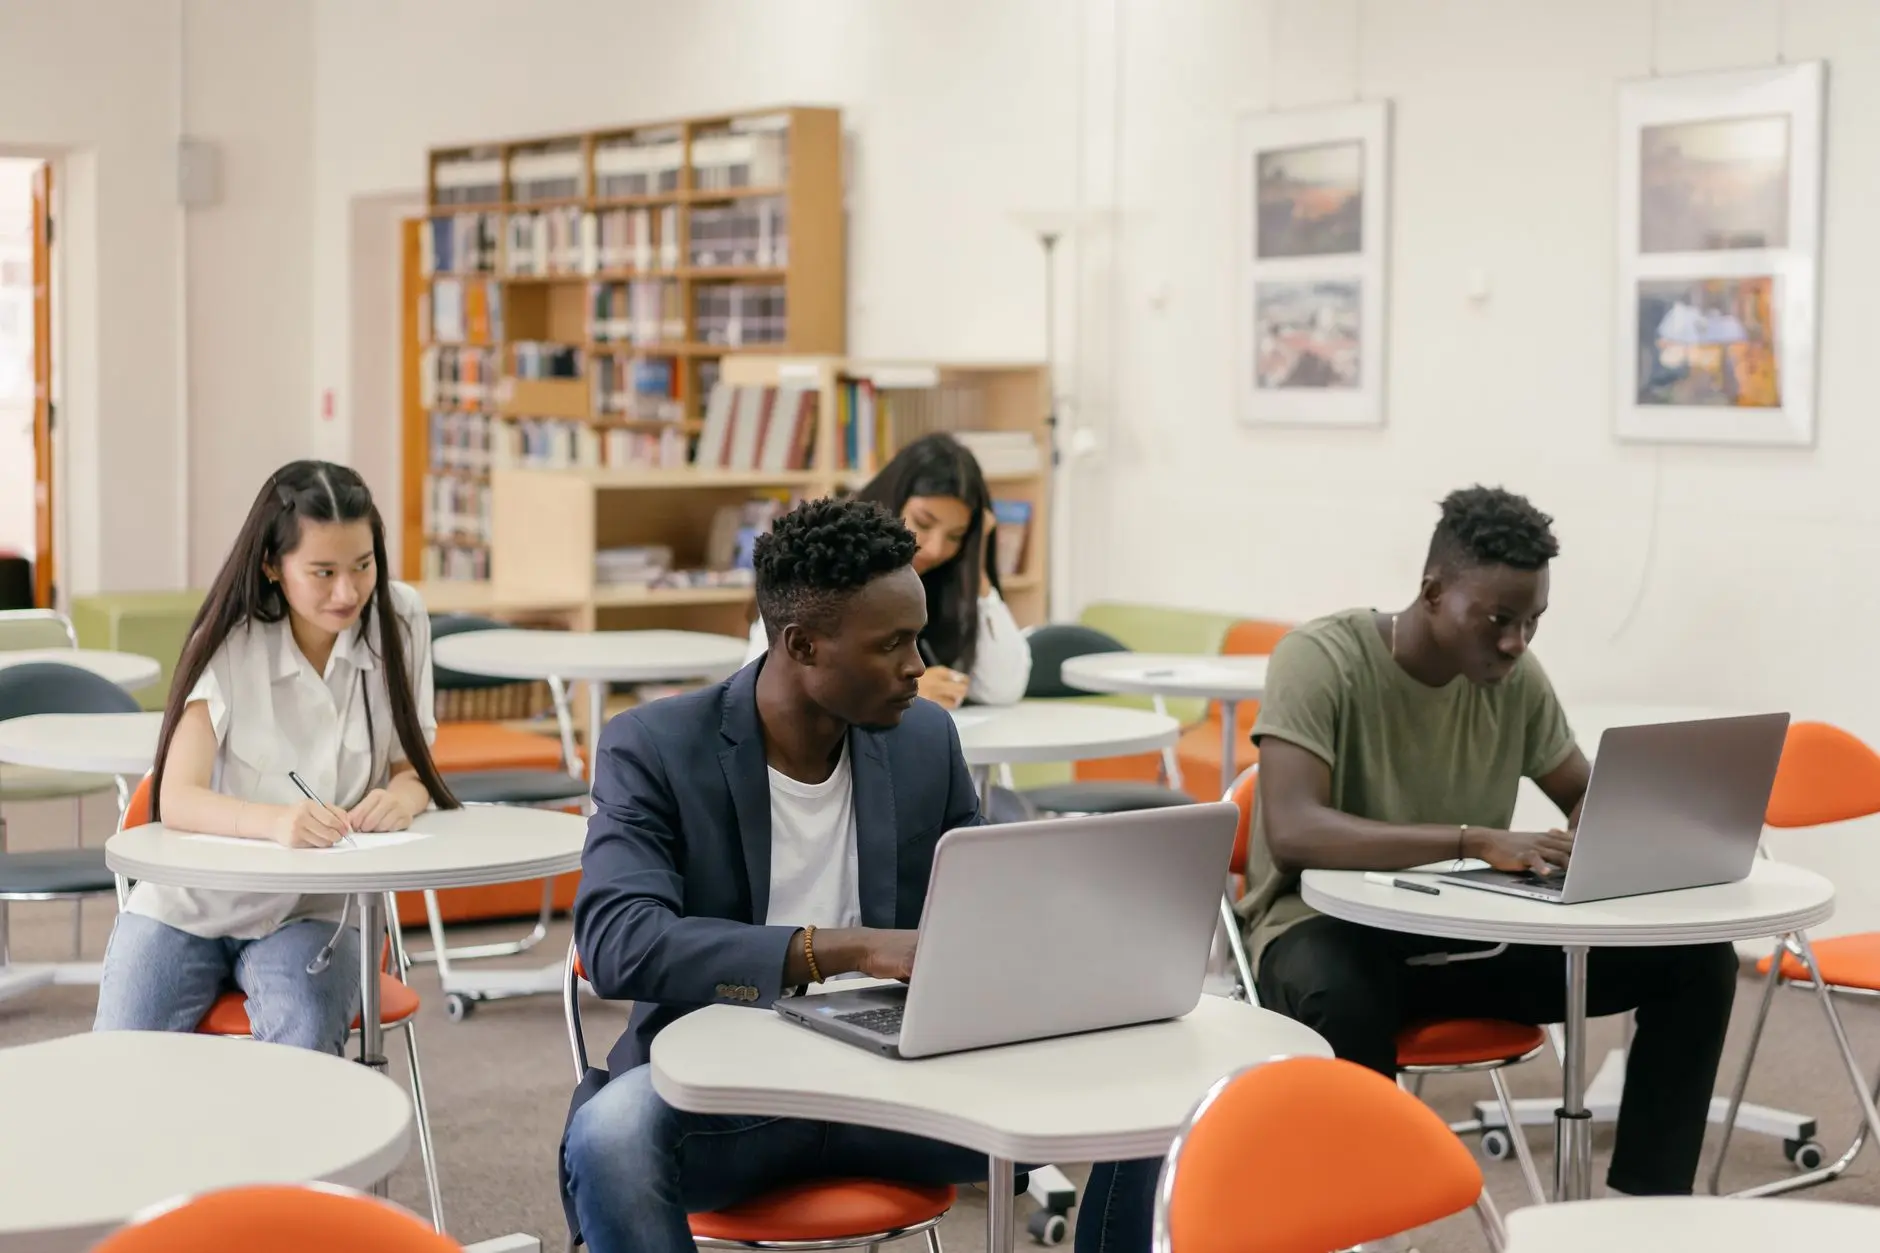
Higher education institutions operate as unique digital ecosystems. They collect, process, and retain vast quantities of sensitive data, ranging from academic records and financial aid documents to cutting-edge medical research and biometric identifiers. Because of this complex data footprint, modern privacy policy changes carry immense operational weight for academic administrators.
When global regulations, federal frameworks, or state statutes shift, universities cannot simply update a website footer link. They must restructure research pipelines, overhaul student portals, and renegotiate vendor agreements. Understanding how these regulatory adjustments ripple through campus networks is essential for institutional leaders, legal counsels, and campus technologists.
The Expanding Regulatory Scope in Higher Education
For decades, campus compliance largely meant adhering to sector-specific statutes like the Family Educational Rights and Privacy Act in the United States or equivalent educational confidentiality laws globally. Today, broad omnibus regulations like the European Union General Data Protection Regulation and a patchwork of state privacy laws apply simultaneously to modern universities.
When these broader laws undergo revision, they often intersect awkwardly with legacy educational frameworks. For instance, a regulatory expansion concerning data minimization can conflict with federal requirements for long-term financial aid auditing or alumni tracking. As data protection authorities issue stricter interpretations of valid consent, universities find that traditional implied consent models used during student enrollment are no longer legally sufficient.
How Policy Changes Affect Universities Operationally
Academic institutions are decentralized by design. Individual departments, research labs, and administrative offices frequently procure their own software tools without centralized IT oversight. When new privacy rules mandate stricter vendor accountability, uncovering and auditing shadow IT across a sprawling campus becomes a massive undertaking.
| Compliance Area | Traditional Approach | Modern Requirement Under New Policies |
|---|---|---|
| Student Consent | Implied via enrollment | Granular, explicit, and freely given |
| Data Retention | Indefinite storage of records | Strict minimization and automated deletion |
| Vendor Oversight | Basic software licensing | Rigorous Data Processing Agreements |
| Research Data | Siloed lab management | Centralized governance and encryption |
Furthermore, research universities manage multi-million-dollar grant programs. Funding bodies increasingly tie grant disbursements to robust cybersecurity and data governance standards. A failure to adapt internal privacy policies to meet revised federal or international mandates can result in immediate grant suspensions or the loss of eligibility for future research funding.
Real-World Impact: The Research Data Dilemma
Consider a mid-sized research university conducting clinical trials on wearable health devices. Under older regulatory frameworks, participant data could be pooled and shared freely with international partner universities. Recent compliance mandates and cross-border data transfer restrictions have upended this model.
Following strict updates to international data protection enforcement, the university had to halt a joint European research project until every participating student and community participant signed newly drafted, explicit consent forms. Furthermore, the institution had to implement zero-knowledge encryption for all transferred datasets. This scenario demonstrates how high-level legal adjustments translate directly into paused projects, unexpected legal fees, and administrative bottlenecks.
Academic institutions are uniquely vulnerable to regulatory shifts because they balance open research sharing with strict personal data obligations. Adapting to new policies requires a cultural shift toward proactive digital stewardship.
Actionable Steps for Campus Compliance Teams
Navigating constant regulatory evolution requires a structured, institutional approach. University administrators and compliance officers should immediately implement the following mitigation strategies:
- Conduct Comprehensive Data Mapping: Identify every system holding student, faculty, and research data to understand precisely where sensitive information resides.
- Revise Vendor Management Protocols: Ensure all third-party learning management systems, cloud storage providers, and SaaS vendors sign updated Data Processing Agreements.
- Modernize Privacy Notices: Replace dense, legalistic privacy statements with clear, layered notices that explain data collection practices in plain language.
- Establish Cross-Functional Governance Committees: Form a working group including legal counsel, IT security, registrar staff, and academic senate representatives to review upcoming regulatory changes.
Frequently Asked Questions
Do international privacy laws apply to US universities?
Yes. If a university actively recruits students from regions like the European Union or collects data from individuals located abroad, it may fall under the territorial scope of international laws such as the GDPR, regardless of where the physical campus is located.
How do policy changes affect student data rights?
New regulations typically strengthen student rights regarding data access, portability, and deletion. Universities must establish streamlined digital portals allowing students to exercise these rights efficiently.
What is the biggest compliance risk for universities today?
Unmonitored shadow IT and decentralized data collection across various academic departments represent the greatest vulnerability during regulatory audits.
Conclusion
As legislative bodies worldwide tighten data protection standards, universities must transition from reactive compliance to proactive digital governance. Recognizing how policy changes affect universities allows institutional leaders to protect institutional funding, safeguard student trust, and maintain academic freedom in an increasingly regulated digital era.







Leave a Reply