



How Privacy Policy Changes Affect Healthcare Providers

Share
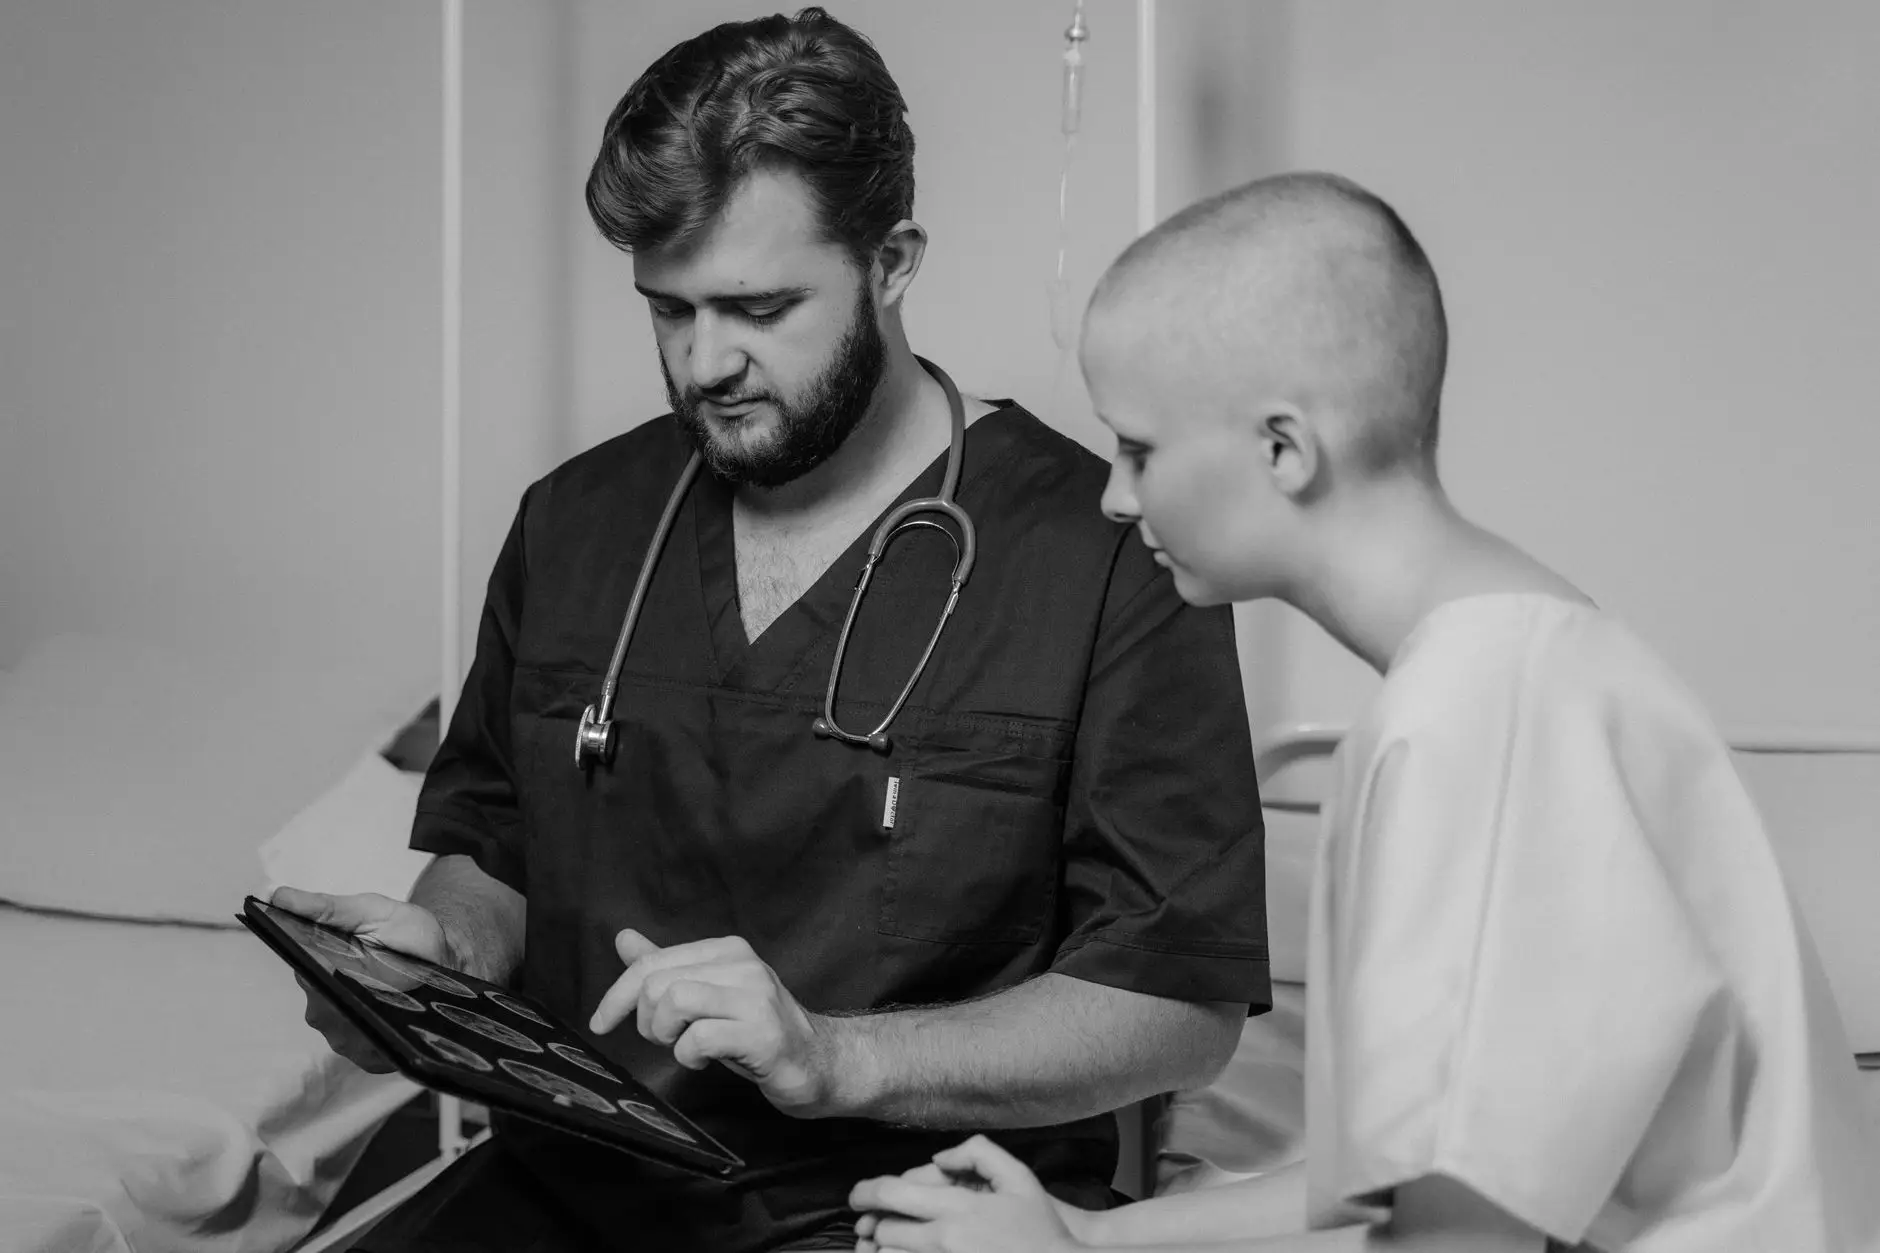
When regulatory bodies rewrite the rules governing digital information, medical practices feel the impact almost immediately. For clinics, hospitals, and digital health startups, evolving privacy policy changes affect healthcare providers in ways that go far beyond basic administrative adjustments. These legal shifts redefine how patient intake forms are designed, how electronic health records are shared between specialists, and how third-party analytics tools track website visitors seeking medical advice.
Healthcare organizations historically relied on traditional frameworks like the Health Insurance Portability and Accountability Act (HIPAA) in the United States or regional data protection acts globally. However, modern privacy policy changes now bridge traditional medical regulations with broader consumer privacy laws, artificial intelligence governance, and strict cross-border data transfer rules. Navigating this complex regulatory environment requires clinical leadership and compliance officers to rethink their operational workflows from the ground up.
The Core Drivers Behind Modern Privacy Policy Changes
Regulatory scrutiny on medical institutions has intensified due to the widespread adoption of telehealth apps, wearable health monitors, and cloud-based practice management systems. Regulators have noticed that many patient portals and clinic websites unknowingly share visitor IP addresses and browsing behavior with social media giants and marketing platforms via tracking pixels.
As a result, updated privacy policies enforce stricter definitions of personally identifiable information and protected health information. Organizations can no longer rely on ambiguous consent banners. Explicit, granular opt-in mechanisms are becoming mandatory, shifting the burden of proof directly onto healthcare providers to demonstrate how patient data flows through their digital ecosystems.
How Policy Shifts Impact Daily Clinical Operations
When new regulations take effect, administrative teams and IT departments face immediate operational challenges. Patient onboarding, appointment scheduling, and billing systems must be audited to ensure compliance with updated mandates.
| Operational Area | Previous Approach | New Regulatory Requirement |
|---|---|---|
| Patient Intake | Broad consent embedded in general terms of service. | Granular, unbundled opt-in for marketing and analytics. |
| Website Tracking | Unrestricted use of third-party tracking pixels. | Complete audit and removal of unauthorized trackers sharing health queries. |
| Telehealth Software | Standard video tools with basic encryption. | Verified business associate agreements and end-to-end audit logs. |
As noted by digital health regulatory analyst Dr. Marcus Vance, “Institutions that treat privacy compliance as a once-a-year checklist item will struggle to survive modern enforcement actions. Privacy policy changes demand continuous architectural visibility into every data touchpoint.”
Real-World Impact: The Telehealth Compliance Challenge
Consider a mid-sized regional mental health clinic that rapidly deployed a popular virtual counseling platform during recent years. While the platform allowed therapists to see patients remotely, it integrated third-party analytics plugins to track user acquisition metrics. Under updated regulatory guidance regarding web tracking technologies, the clinic inadvertently transmitted patient appointment booking inquiries to advertising networks.
When regulatory bodies issued updated enforcement notices regarding tracking pixels on medical websites, the clinic faced severe scrutiny. Compliance teams had to hastily overhaul their website architecture, remove unauthorized marketing scripts, and notify patients about unauthorized data disclosures. This scenario illustrates how seemingly minor policy refinements regarding digital tracking can trigger major operational crises for unprepared healthcare entities.
Actionable Steps for Healthcare Providers
To mitigate legal risks and protect patient trust, healthcare administrators must take proactive measures. Strengthening organizational data protection protocols involves several key implementation steps:
- Conduct Comprehensive Data Audits: Map every data collection point across websites, mobile applications, and physical intake desks to identify where protected health information resides.
- Review Vendor Agreements: Ensure all software vendors, cloud providers, and marketing agencies sign updated business associate agreements that reflect current legal liabilities.
- Redesign Consent Workflows: Replace pre-checked consent boxes with clear, unambiguous opt-in choices for any data processing that extends beyond direct medical treatment.
- Train Clinical Staff: Educate front-desk personnel, billing teams, and IT staff on recognizing evolving privacy rights and handling data subject inquiries correctly.
Frequently Asked Questions
Do general consumer privacy laws apply to healthcare providers?
Yes. While medical providers are primarily governed by sector-specific laws like HIPAA, many modern privacy statutes apply to healthcare websites, patient portals, and wellness apps, particularly regarding online tracking and consumer marketing data.
What happens if a clinic fails to update its privacy disclosures?
Failing to update privacy disclosures to reflect current data practices can lead to regulatory investigations, substantial financial penalties, class-action lawsuits, and severe reputational damage among patients.
Conclusion
The intersection of digital technology and healthcare regulation means that privacy rules will continue to evolve rapidly. Understanding how privacy policy changes affect healthcare providers allows medical organizations to transition from reactive compliance to proactive risk management. By auditing digital assets, securing vendor relationships, and respecting patient consent rights, healthcare providers can safeguard their patients while maintaining operational resilience in a digital-first world.









Leave a Reply