



What Schools Should Know About NDPA and Data Privacy Compliance

Share
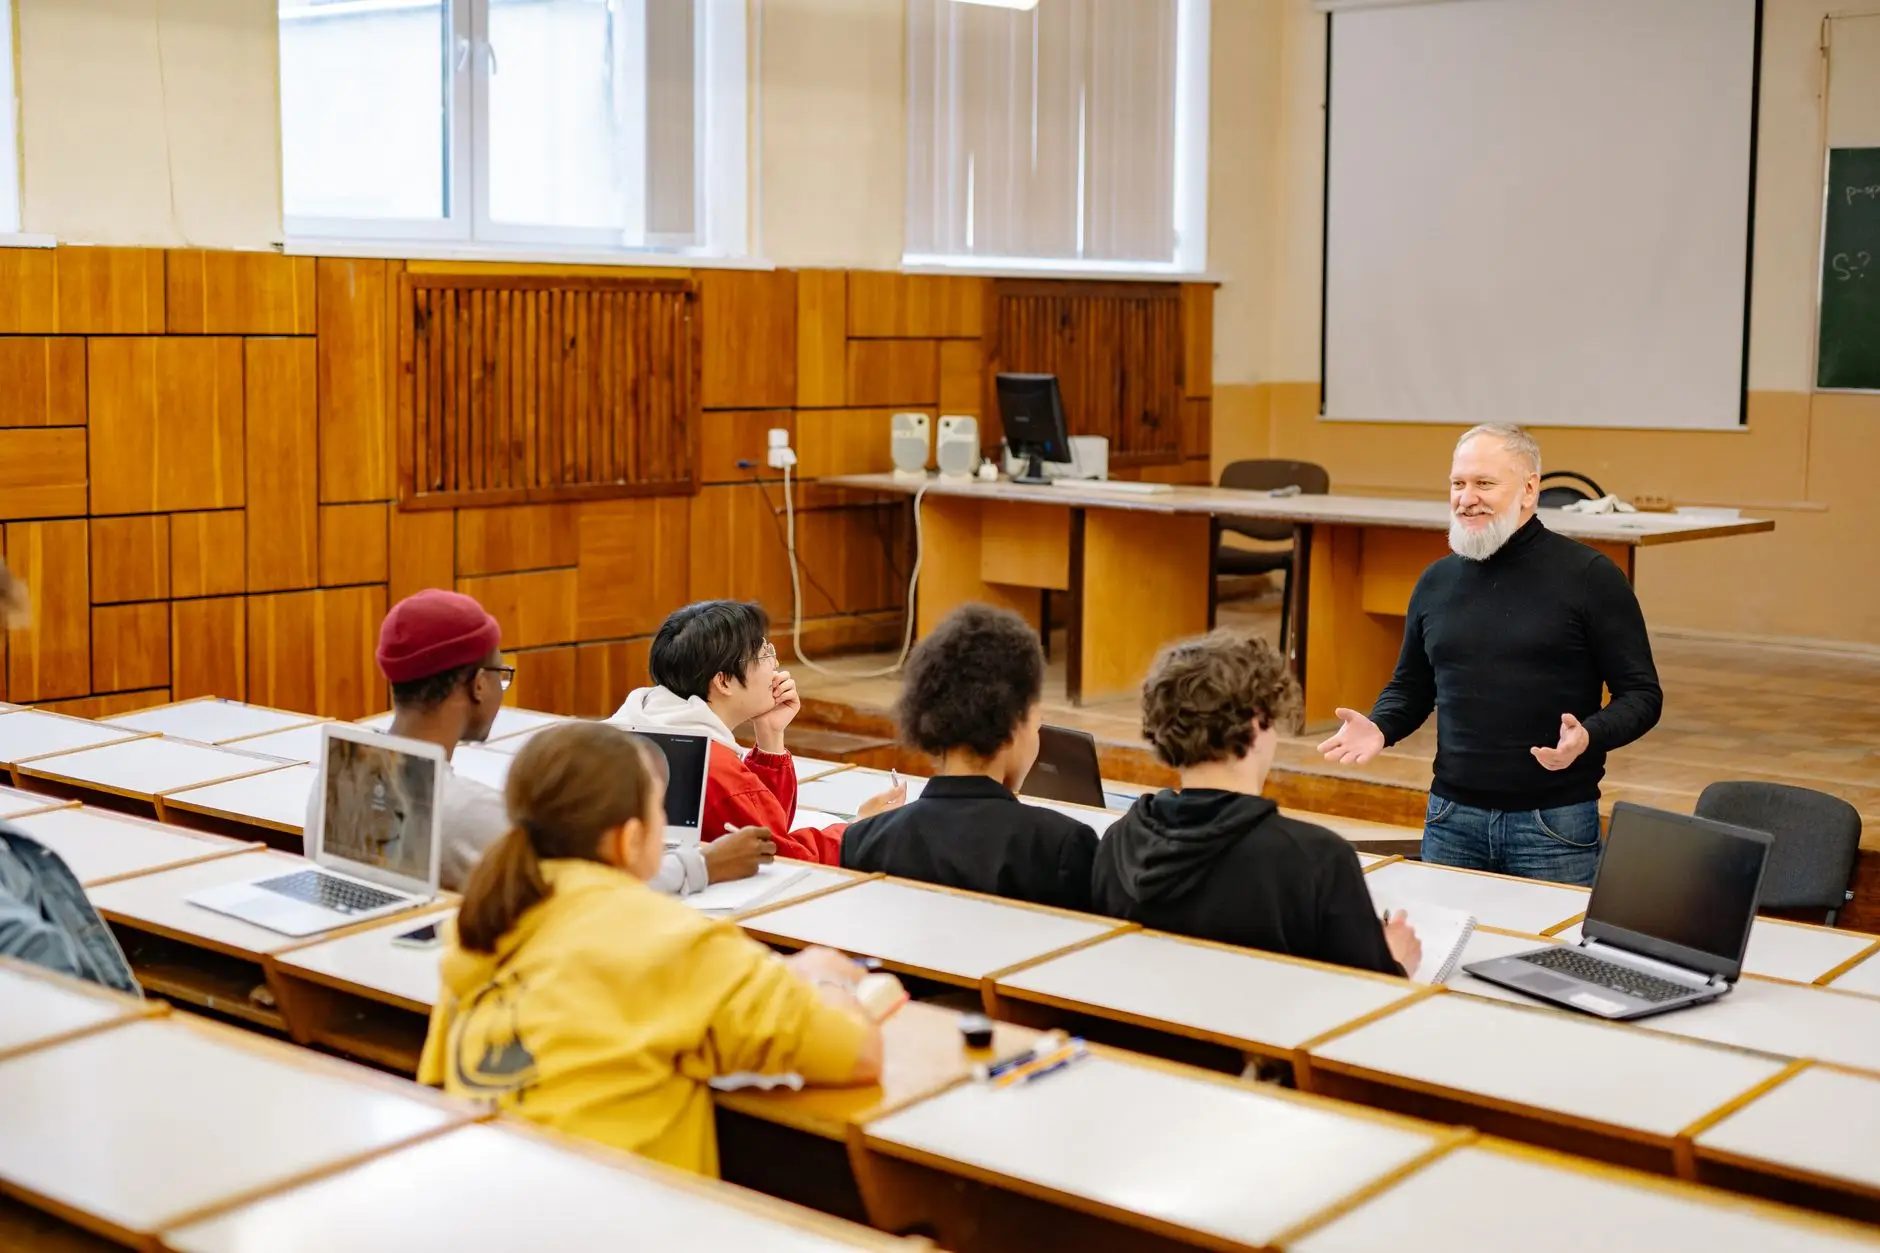
Educational institutions collect vast amounts of sensitive information every single day. From student report cards and medical histories to biometric attendance logs and home addresses, modern learning environments function as massive data repositories. Yet, many educators and administrators remain unaware of their strict legal obligations under modern privacy statutes. If you work in education, understanding why schools Know NDPA regulations is no longer optional; it is a core operational requirement.
The Growing Data Footprint of Modern Education
Classrooms have transformed dramatically over the last decade. Interactive whiteboards, cloud-based learning management systems, mobile grading apps, and remote virtual classrooms mean that student information flows freely across digital networks. While these tools enhance learning, they also expand the attack surface for cyber threats and increase regulatory exposure. When educational facilities process personal data, they act as data controllers under the law. This means they bear full responsibility for how that information is collected, stored, shared, and eventually destroyed.
According to reports from the Nigeria Data Protection Commission, public and private institutions face mounting scrutiny regarding how they handle minor data subjects. Children and students require heightened legal protection due to their developmental vulnerability. When institutions fail to implement adequate security safeguards, the fallout can lead to identity theft, financial fraud, and severe reputational damage.
Core Obligations for Educational Institutions
Compliance with data protection legislation requires a structured approach to institutional administration. Schools must move beyond basic password protection and establish robust internal policies. Here are the core duties every administrator must address:
- Lawful Basis for Processing: Schools must establish a clear legal basis, such as parental consent or statutory educational mandates, before collecting student data.
- Data Minimization: Institutions should only collect information that is strictly necessary for educational and administrative purposes.
- Vendor Risk Management: Third-party educational technology vendors must sign data processing agreements that guarantee strict confidentiality and security standards.
- Data Subject Rights: Parents and legal guardians possess the right to access, correct, or request the deletion of their children’s records.
Real-Life Scenario: The Third-Party Vendor Trap
Consider a mid-sized secondary school that partners with a foreign software provider to host an online math portal. The platform requires students to register using their full legal names, email addresses, and birth dates. Six months later, the software vendor suffers a database misconfiguration, exposing thousands of student records online. Because the school failed to conduct a vendor due diligence assessment or establish a formal data processing agreement, the institution faces direct regulatory investigations and angry inquiries from parents. This scenario highlights why schools Know NDPA standards must vet every single piece of educational software brought into the classroom.
NDPA Compliance Requirements for Schools
| Requirement | Description | Action Step |
|---|---|---|
| Consent Management | Valid parental consent for minors | Update enrollment forms with clear opt-in clauses |
| Security Safeguards | Technical measures to protect records | Enforce encryption and multi-factor authentication |
| Staff Training | Educating employees on data safety | Conduct mandatory annual privacy workshops for teachers |
| Incident Response | Protocol for handling data leaks | Establish a clear breach notification workflow |
Actionable Checklist for School Administrators
To bridge the gap between educational goals and legal accountability, leadership teams should execute the following steps immediately:
- Conduct a comprehensive data audit to map out where student and staff records are stored.
- Review all software subscriptions and third-party vendor contracts for compliance clauses.
- Designate a qualified data protection officer or compliance lead within the administration.
- Implement strict access controls so only authorized teachers view sensitive student files.
- Establish clear protocols for responding to parental access requests within statutory timeframes.
Frequently Asked Questions
Are private schools exempt from data protection laws?
No. Both public and private educational institutions process personal data and must comply with applicable data protection regulations.
How do schools handle data consent for young children?
For minors below the statutory age of majority, consent must be obtained directly from a parent or legal guardian in a clear and verifiable manner.
What happens if a school suffers a data breach?
The institution must notify the relevant regulatory authority within the mandated statutory window and inform affected data subjects if there is a high risk to their rights.
Conclusion
Educational institutions exist to shape the future, but failing to secure student records can jeopardize that very future. By ensuring that schools Know NDPA rules inside and out, administrators can build a secure, trusted, and legally compliant environment for students, parents, and staff alike. Proactive data protection is no longer just a legal hurdle; it is a fundamental pillar of modern educational integrity.










Leave a Reply