



What Healthcare Providers Should Know About NDPA and Data Privacy

Share
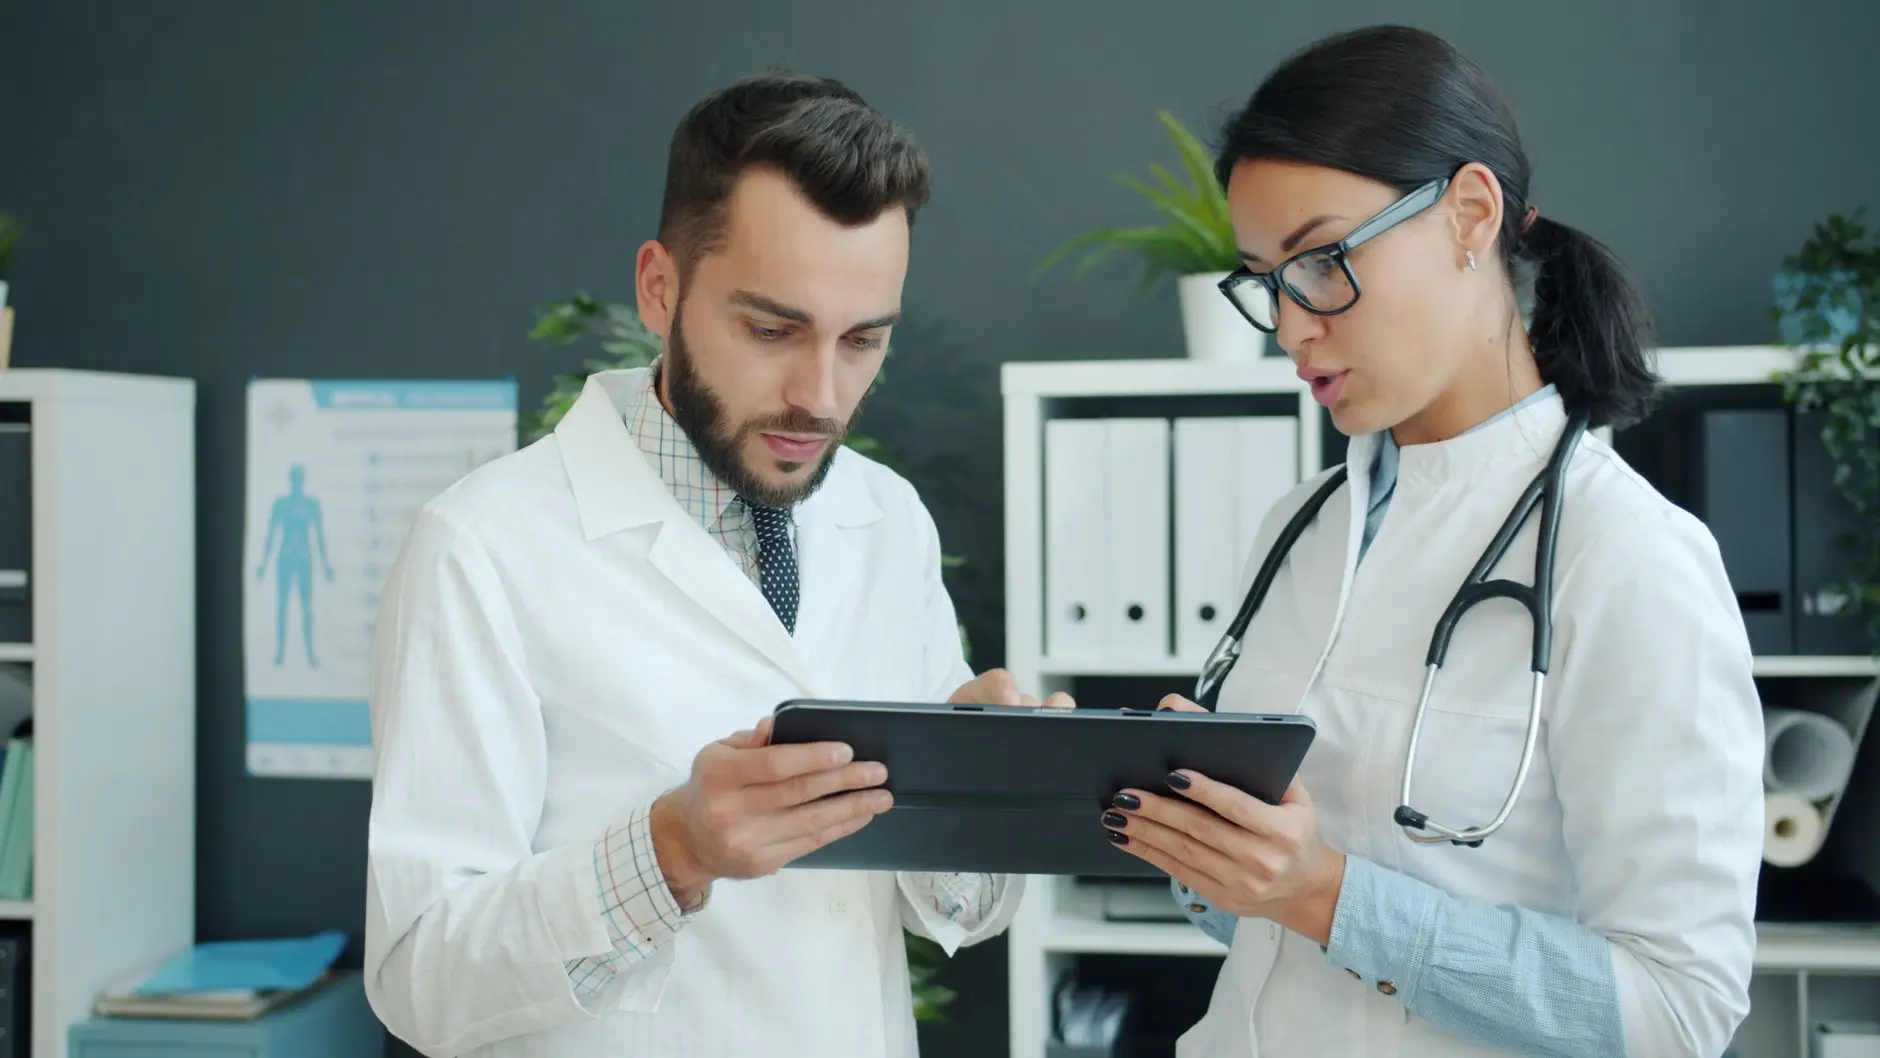
Medical institutions handle some of the most sensitive information imaginable, ranging from diagnostic imaging and genetic markers to daily medication logs and insurance histories. As digital transformation sweeps through hospitals, clinics, and diagnostic labs, the volume of personal data collected has skyrocketed. For medical professionals, understanding why healthcare providers Know NDPA standards is no longer optional. It is a fundamental operational requirement that dictates how patient files are collected, stored, and shared.
The Nigeria Data Protection Act establishes a comprehensive framework for safeguarding personal information. Unlike general commercial sectors, healthcare operations involve special category data, which demands a heightened tier of security and strict accountability. A single mismanaged database can expose thousands of patients to identity theft, financial fraud, and severe reputational damage. Compliance teams and practice managers must look closely at their current workflows to align with national mandates.
Understanding the Mandate for Healthcare Providers Know NDPA
The regulatory framework shifts the burden of proof directly onto organizations processing personal data. Under the law, clinics and hospitals act as data controllers or data processors. They are legally accountable for every piece of patient information that enters their systems, whether captured via paper intake forms or cloud-based electronic health records. Regulatory bodies such as the Nigeria Data Protection Commission expect medical facilities to implement robust technical and organizational measures from the ground up.
When healthcare providers Know NDPA requirements, they transition from reactive data management to proactive risk mitigation. This shift protects medical organizations from severe statutory penalties while fostering deeper trust with patients. In an era where data breaches make daily headlines, demonstrating a clear commitment to privacy serves as a powerful competitive advantage for modern medical practices.
Core Obligations for Medical Practices
Medical establishments must operationalize several key legal principles to remain compliant. These principles govern every interaction between a patient and a healthcare provider:
- Lawfulness and Transparency: Patients must understand precisely why their medical data is being collected and how it will be utilized.
- Purpose Limitation: Data gathered for routine check-ups cannot be repurposed for third-party marketing without explicit consent.
- Data Minimization: Providers should only collect information that is strictly necessary for diagnosis and treatment.
- Storage Limitation: Medical records must be retained only as long as medically or legally required, then securely destroyed.
Real-World Risks and Consequences
Consider a mid-sized regional diagnostic clinic that migrated its patient imaging database to an unencrypted cloud server to cut operational costs. Due to lax access controls, an unauthorized external actor accessed thousands of MRI scans and patient identification files. Under the regulatory framework, this oversight constitutes a severe breach of data security principles.
The consequences extend far beyond statutory fines. The clinic faced immediate public scrutiny, lost key institutional partnerships, and spent months managing individual data subject rights inquiries from affected patients demanding damage compensation. This scenario illustrates why every administrator must prioritize robust cybersecurity and data governance before an incident occurs.
| Compliance Area | Traditional Practice | NDPA Compliant Approach |
|---|---|---|
| Patient Consent | Implied verbal agreement | Granular, documented opt-in |
| Data Storage | Local unencrypted drives | End-to-end encrypted cloud/local storage |
| Staff Training | Occasional reminders | Mandatory, tracked annual certification |
| Breach Response | Reactive concealment | Immediate reporting to NDPC and victims |
Actionable Steps for Healthcare Compliance
Achieving full regulatory alignment requires a structured, systematic approach across all departments. Practice managers and chief medical officers can follow this actionable checklist to strengthen their privacy posture:
- Conduct a Data Mapping Audit: Identify every touchpoint where patient information enters, travels through, and leaves your facility.
- Update Privacy Notices: Rewrite patient intake forms and digital portals to clearly explain data rights in plain, accessible language.
- Enforce Role-Based Access: Restrict electronic medical record access so that staff members only view data necessary for their specific job functions.
- Establish Incident Response Plans: Create a step-by-step protocol for detecting, containing, and reporting data breaches within statutory deadlines.
- Partner with Credible Vendors: Ensure all software suppliers, billing partners, and cloud providers sign data processing agreements that meet national standards.
Data privacy in healthcare is not merely a legal checkbox. It is an extension of the medical oath to do no harm, protecting patients in both the physical and digital realms.
As the digital health ecosystem continues to mature, regulatory oversight will only intensify. Industry leaders emphasize that building a privacy-first culture protects both the institution and the individuals who rely on its services. By investing in proper staff training, secure technology infrastructure, and transparent communication, medical facilities can navigate the regulatory landscape with confidence.
Frequently Asked Questions
Do these regulations apply to small private clinics?
Yes. The legislation applies to any organization processing personal data in Nigeria, regardless of size. Small clinics handling sensitive health records must comply with core data protection principles.
What happens if a medical facility suffers a data breach?
Organizations must notify the regulatory authority promptly and, where high risks to individuals exist, inform the affected patients directly to mitigate potential harm.
How does this impact patient data access rights?
Patients retain the legal right to request copies of their medical records, correct inaccurate information, and, in certain circumstances, object to specific processing activities.
Conclusion
Navigating modern data regulations requires constant vigilance, clear policies, and a genuine commitment to patient confidentiality. When healthcare providers Know NDPA principles and integrate them into daily operations, they build a resilient defense against digital threats. Protecting patient data is an essential pillar of modern medical ethics and sustainable clinical success.










Leave a Reply