



How Universities Should Think About AI Governance Before Using AI Tools

Share
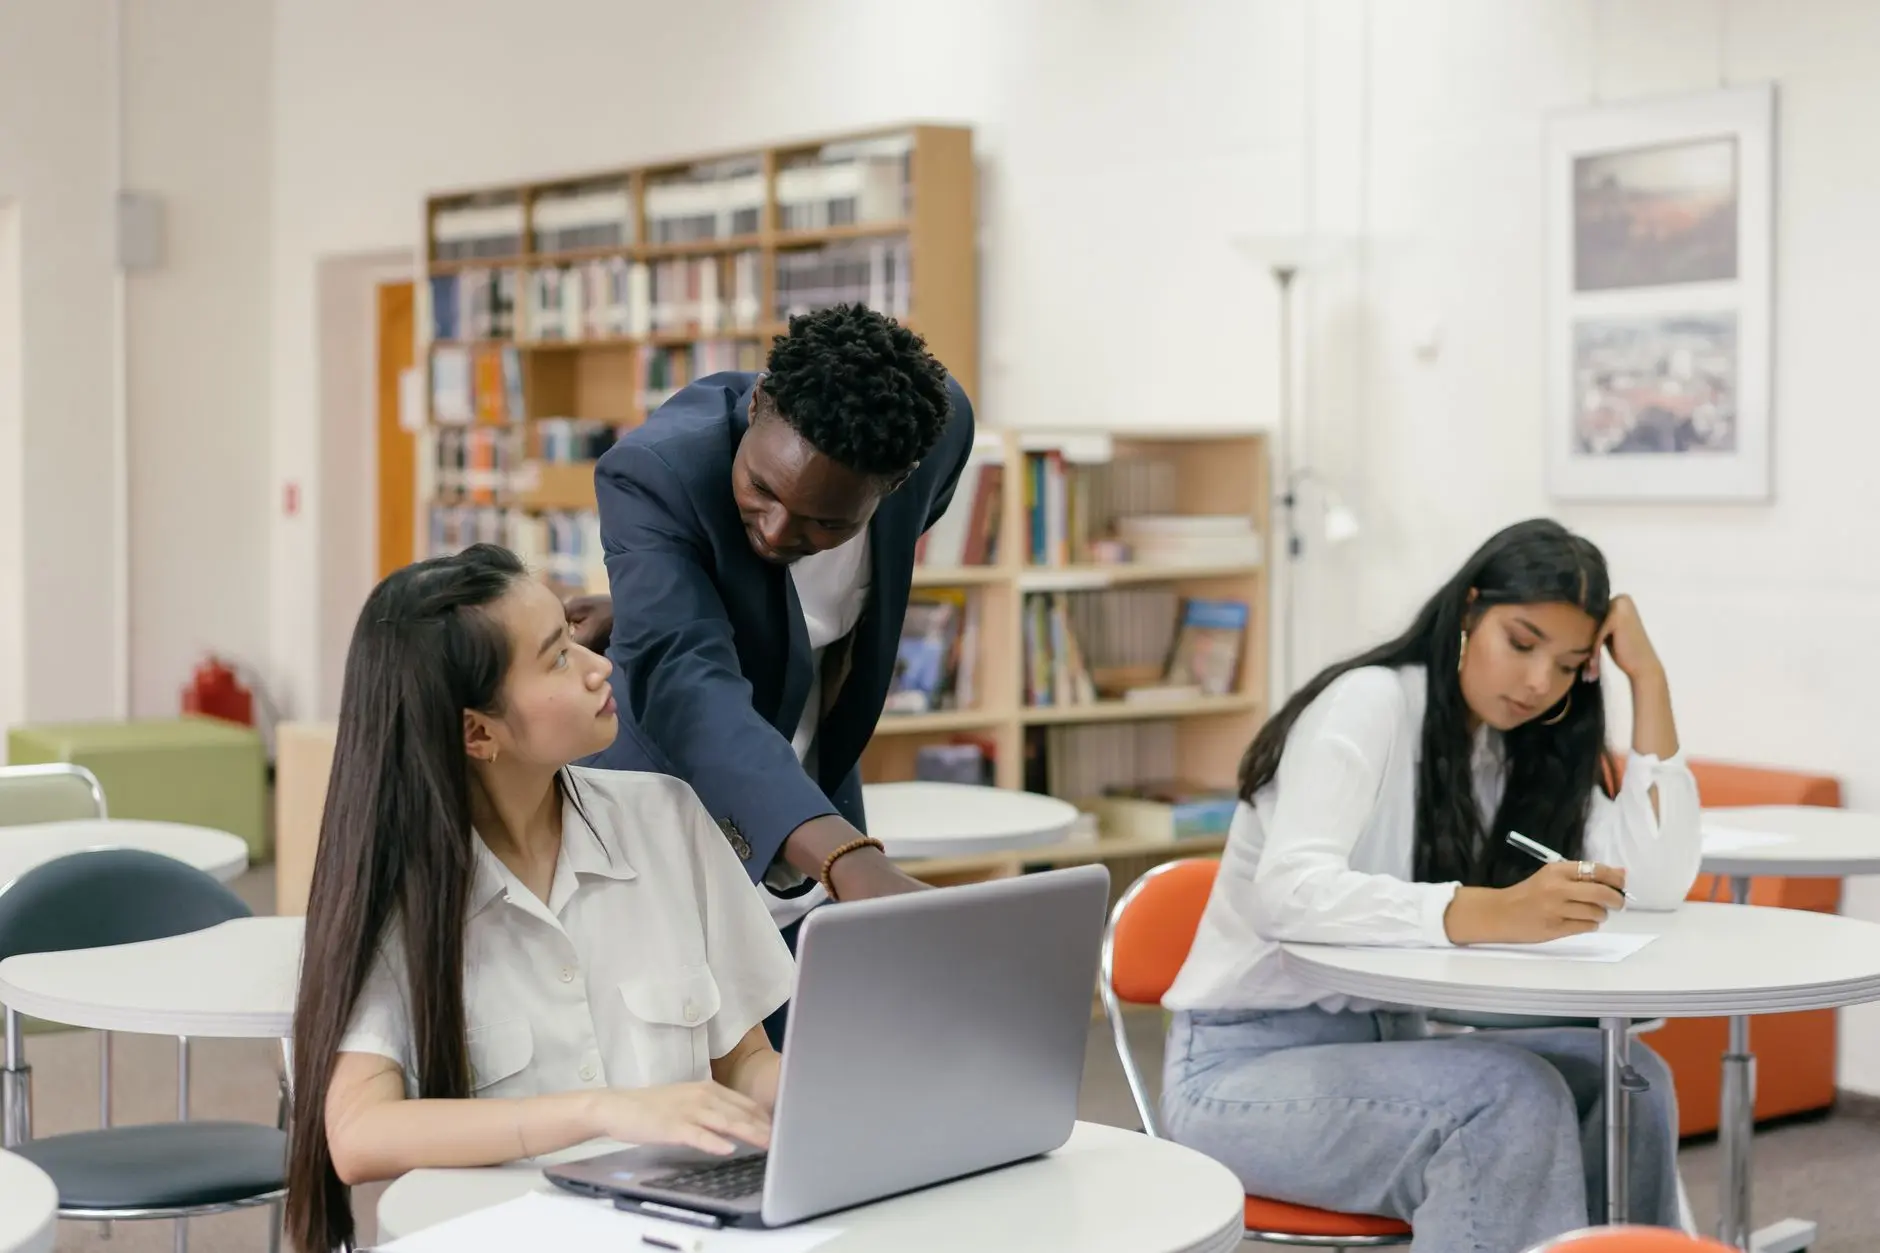
The Urgency of AI Governance in Higher Education
Higher education institutions are rushing to adopt generative artificial intelligence, machine learning algorithms, and automated grading systems. However, before deployment, universities think AI governance using AI should be the primary operational baseline rather than an afterthought. Academic environments handle sensitive student records, proprietary research, and confidential employee data, making them prime targets for regulatory scrutiny and data breaches.
As the European Union and global regulators tighten oversight on automated decision-making, educational leaders must establish clear internal policies. Without a formal governance structure, institutions risk severe legal penalties, reputational damage, and the erosion of trust among students and faculty members. Understanding how compliance frameworks apply to campus technology is critical for every administrator.
Understanding Regulatory Pressures and the EU AI Act
The regulatory landscape for artificial intelligence is shifting rapidly. Under frameworks like the EU AI Act, educational systems that evaluate students, determine admissions, or monitor exams are often classified as high-risk applications. This classification triggers strict obligations regarding transparency, human oversight, data quality, and security.
Dr. Elena Vance, a prominent technology law researcher, notes, "Universities are unique ecosystems that combine public sector accountability with commercial research partnerships. When deploying automated systems, they cannot simply rely on vendor promises. They must independently verify that their AI usage respects fundamental rights and strict data protection standards outlined in legislative texts such as the European Commission AI regulatory proposals."
Core Components of a University AI Framework
Building an effective institutional governance model requires a multidisciplinary approach involving legal counsel, IT security, academic senate members, and student representatives. Institutions must look beyond simple software procurement and evaluate long-term societal impacts.
- Data Minimization: Limiting the amount of personal student and faculty data fed into third-party machine learning models.
- Transparency Protocols: Clearly informing students when and how automated systems are used in grading, assessment, or counseling.
- Human-in-the-Loop Oversight: Ensuring that no significant academic decision relies entirely on algorithmic output without human review.
- Vendor Risk Assessments: Rigorously vetting EdTech providers for data security compliance and proprietary data usage rights.
Comparative Risk Matrix for Higher Education AI Tools
Different campus applications carry distinct risk profiles that dictate the level of governance required before rollout.
| AI Application Category | Potential Risk Level | Key Compliance Requirement |
|---|---|---|
| Automated Exam Proctoring | High Risk | Explicit consent, strict biometric data protection, human appeal paths. |
| Administrative Chatbots | Low to Medium Risk | Clear disclosure of bot identity, no persistent storage of sensitive queries. |
| Admissions Screening Algorithms | High Risk | Bias auditing, explainability, rigorous non-discrimination testing. |
| General Research Assistants | Medium Risk | IP protection, prevention of data leakage of proprietary findings. |
A Real-Life Scenario: The Automated Grading Dilemma
Consider a mid-sized university that implemented an experimental AI-driven essay grading tool to reduce faculty workload. Within weeks, students noticed inconsistent scoring patterns, and international students experienced higher error rates due to linguistic bias in the training data. Furthermore, the third-party software provider was using anonymized student essays to train future commercial models without explicit institutional authorization.
This scenario highlights why universities think AI governance using AI systems must precede any contract signing. The institution faced an immediate public relations crisis, potential violations of privacy regulations, and costly emergency remediation work that far outweighed the initial administrative time saved.
Actionable Steps for Campus Leaders
To prevent similar pitfalls, academic leaders and technology committees should implement a phased governance checklist before launching new AI initiatives:
- Form an institutional AI ethics and governance board representing faculty, legal, and student interests.
- Audit all existing generative AI tools currently used informally by departments and individual professors.
- Establish a mandatory procurement review process for any software claiming machine learning capabilities.
- Provide ongoing privacy and algorithmic literacy training for staff and students.
Frequently Asked Questions
Are universities legally liable for bias in third-party AI tools?
Yes. If an institution deploys an algorithm for admissions or grading, the university remains legally responsible for ensuring fairness, non-discrimination, and regulatory compliance, regardless of whether the software was built in-house or purchased from a vendor.
How does student data privacy intersect with generative AI?
Many commercial AI platforms ingest user inputs to retrain their models. If students or faculty enter personal data, academic research, or protected educational records into these tools, it may constitute an unauthorized data transfer and breach institutional privacy policies.
Conclusion
Artificial intelligence offers immense potential to transform higher education, teaching methodologies, and administrative efficiency. However, unlocking these benefits safely requires a proactive stance. When universities think AI governance using AI frameworks before implementation, they safeguard their student body, protect institutional integrity, and ensure sustainable, responsible digital innovation for the future.












Leave a Reply