



CISA Warns of Critical RCE Flaw in MikroTik RouterOS

Share
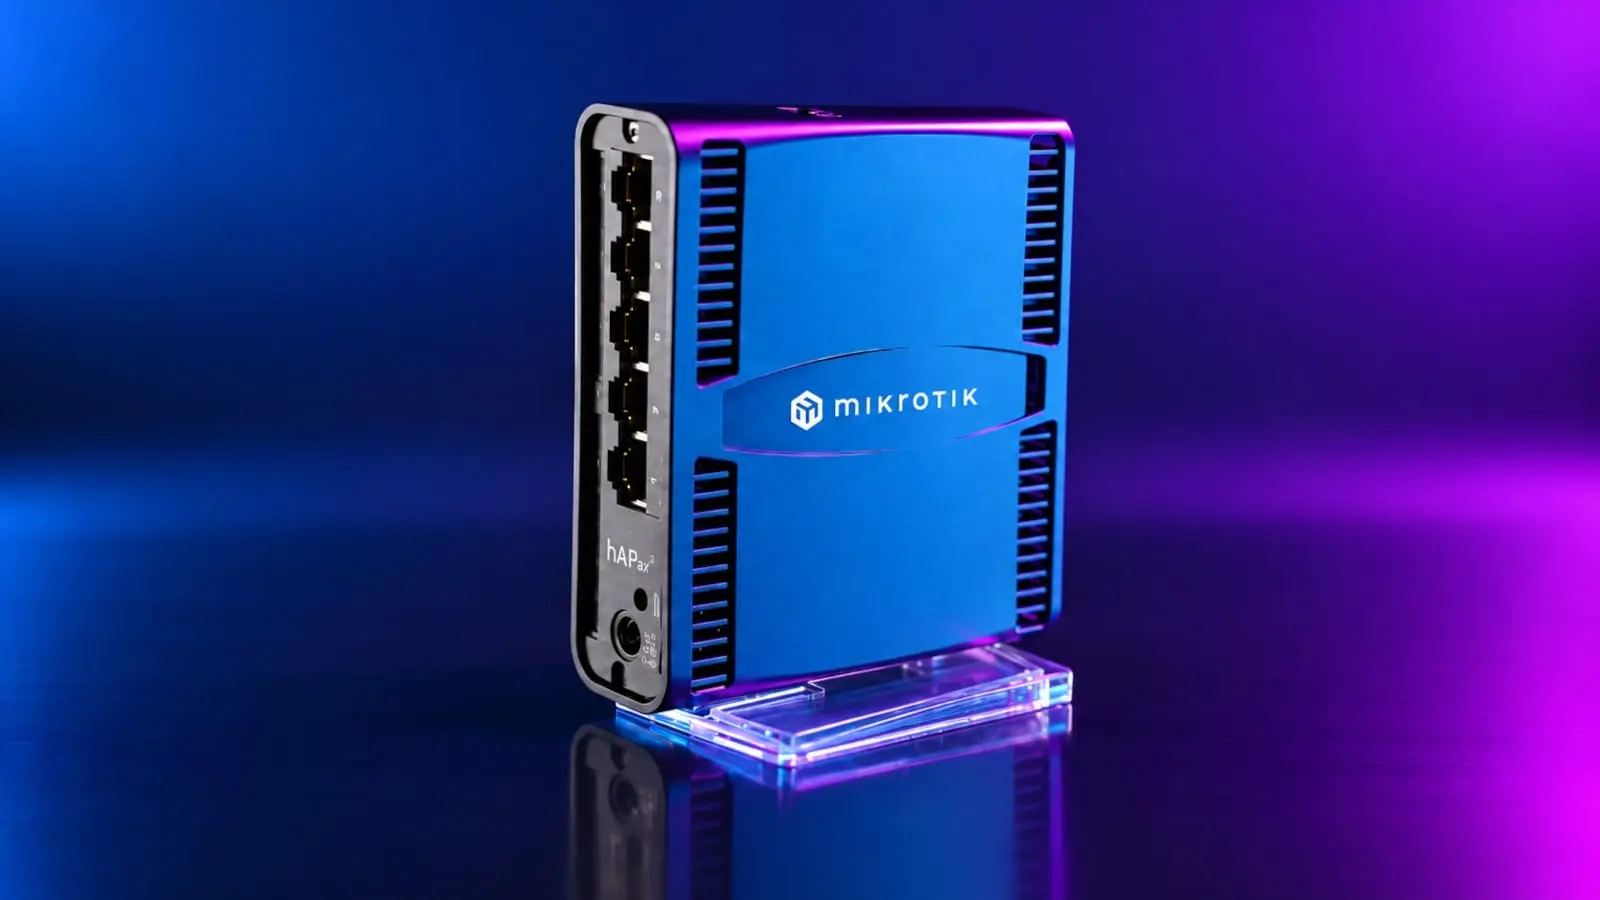
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a critical warning regarding a severe pre-authentication remote code execution (RCE) vulnerability in MikroTik RouterOS. Tracked as CVE-2026-84411, the flaw could allow an unauthenticated attacker to take complete control of affected devices or trigger a denial-of-service (DoS) condition.
The security vulnerability is an integer underflow present in RouterOS’s web-management HTTP request handling. According to CISA, a single crafted request can exploit this weakness before authentication, leading to code execution with root privileges or a denial of service.
Affected Versions and Mitigation
MikroTik RouterOS versions below 7.24 are identified as affected. However, MikroTik has released updates addressing the issue, recommending users upgrade to version 7.23 or later to mitigate the risk. The latest stable version of RouterOS is 7.24.4, while the most recent long-term release is 7.23.7, both made available in mid-September.
As of CISA’s advisory, there is no public knowledge of active exploitation of CVE-2026-84411. Despite this, CISA has released the alert to urge organisations to implement defensive measures swiftly, as MikroTik flaws are frequently targeted by threat actors and botnet malware.
CISA’s Recommendations for Router Owners
In addition to applying the latest security patches, CISA has provided several defensive recommendations for MikroTik router owners:
- Ensure control systems are not directly accessible from the internet.
- Place control networks and remote devices behind robust firewalls, isolated from broader business networks.
- Utilise updated Virtual Private Networks (VPNs) for all remote access, and secure all connected devices effectively.
The warning from CISA highlights the agency’s ongoing efforts to protect critical infrastructure from known and emerging threats. This vulnerability alert follows other recent warnings from the agency, including active exploitation of flaws in WSO2, Adobe, and SharePoint, as previously reported by Privacy Needle.
Organisations and individual users managing MikroTik RouterOS devices are strongly advised to update their systems to version 7.23 or later immediately to safeguard against potential attacks stemming from this critical vulnerability.












Leave a Reply