

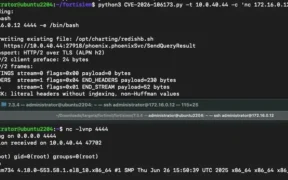
A public exploit has been released for a critical unauthenticated remote code execution flaw impacting Fortinet FortiSIEM.

A critical path traversal vulnerability in Fortinet FortiMail, tracked as CVE-2026-104286, is under active exploitation. The zero-day could allow attackers to write arbitrary files and potentially achieve remote code execution. CISA and Fortinet have issued
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning after a critical zero-day vulnerability in Fortinet FortiMail email security appliances was found under active exploitation. Tracked as CVE-2026-104286, the flaw allows unauthenticated

CISA has directed federal agencies to patch three critical vulnerabilities in Cisco, Citrix, and Fortinet products following reports of active exploitation.

Fortinet has addressed critical security defects in FortiMonitorOnSight and its Privileged Access Agent Chrome extension that could allow authentication bypass.












