

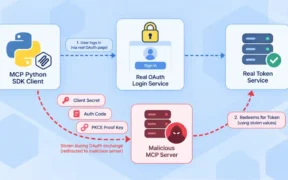
A vulnerability in the Model Context Protocol (MCP) Python SDK allows malicious servers to redirect authentication requests and steal sensitive OAuth credentials.
EfficientIP researchers flagged several AliExpress phishing domains before registration, uncovering a campaign that uses fake browser extensions to steal credentials.
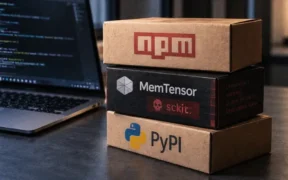
Threat actors have compromised MemTensor packages on npm and PyPI to deploy the sckit credential stealer, targeting sensitive cloud and developer secrets.
A new attack known as TrustSink allows attackers with privileged access to register rogue MFA providers that capture user passwords during legitimate Microsoft Entra logins.
Threat actors exploited CVE-2026-7273 in ZyXEL GS1900 switches to steal credentials and configuration data from devices across 48 countries.












