



Why Founder Data Responsibility Matters Before Startups Scale

Share
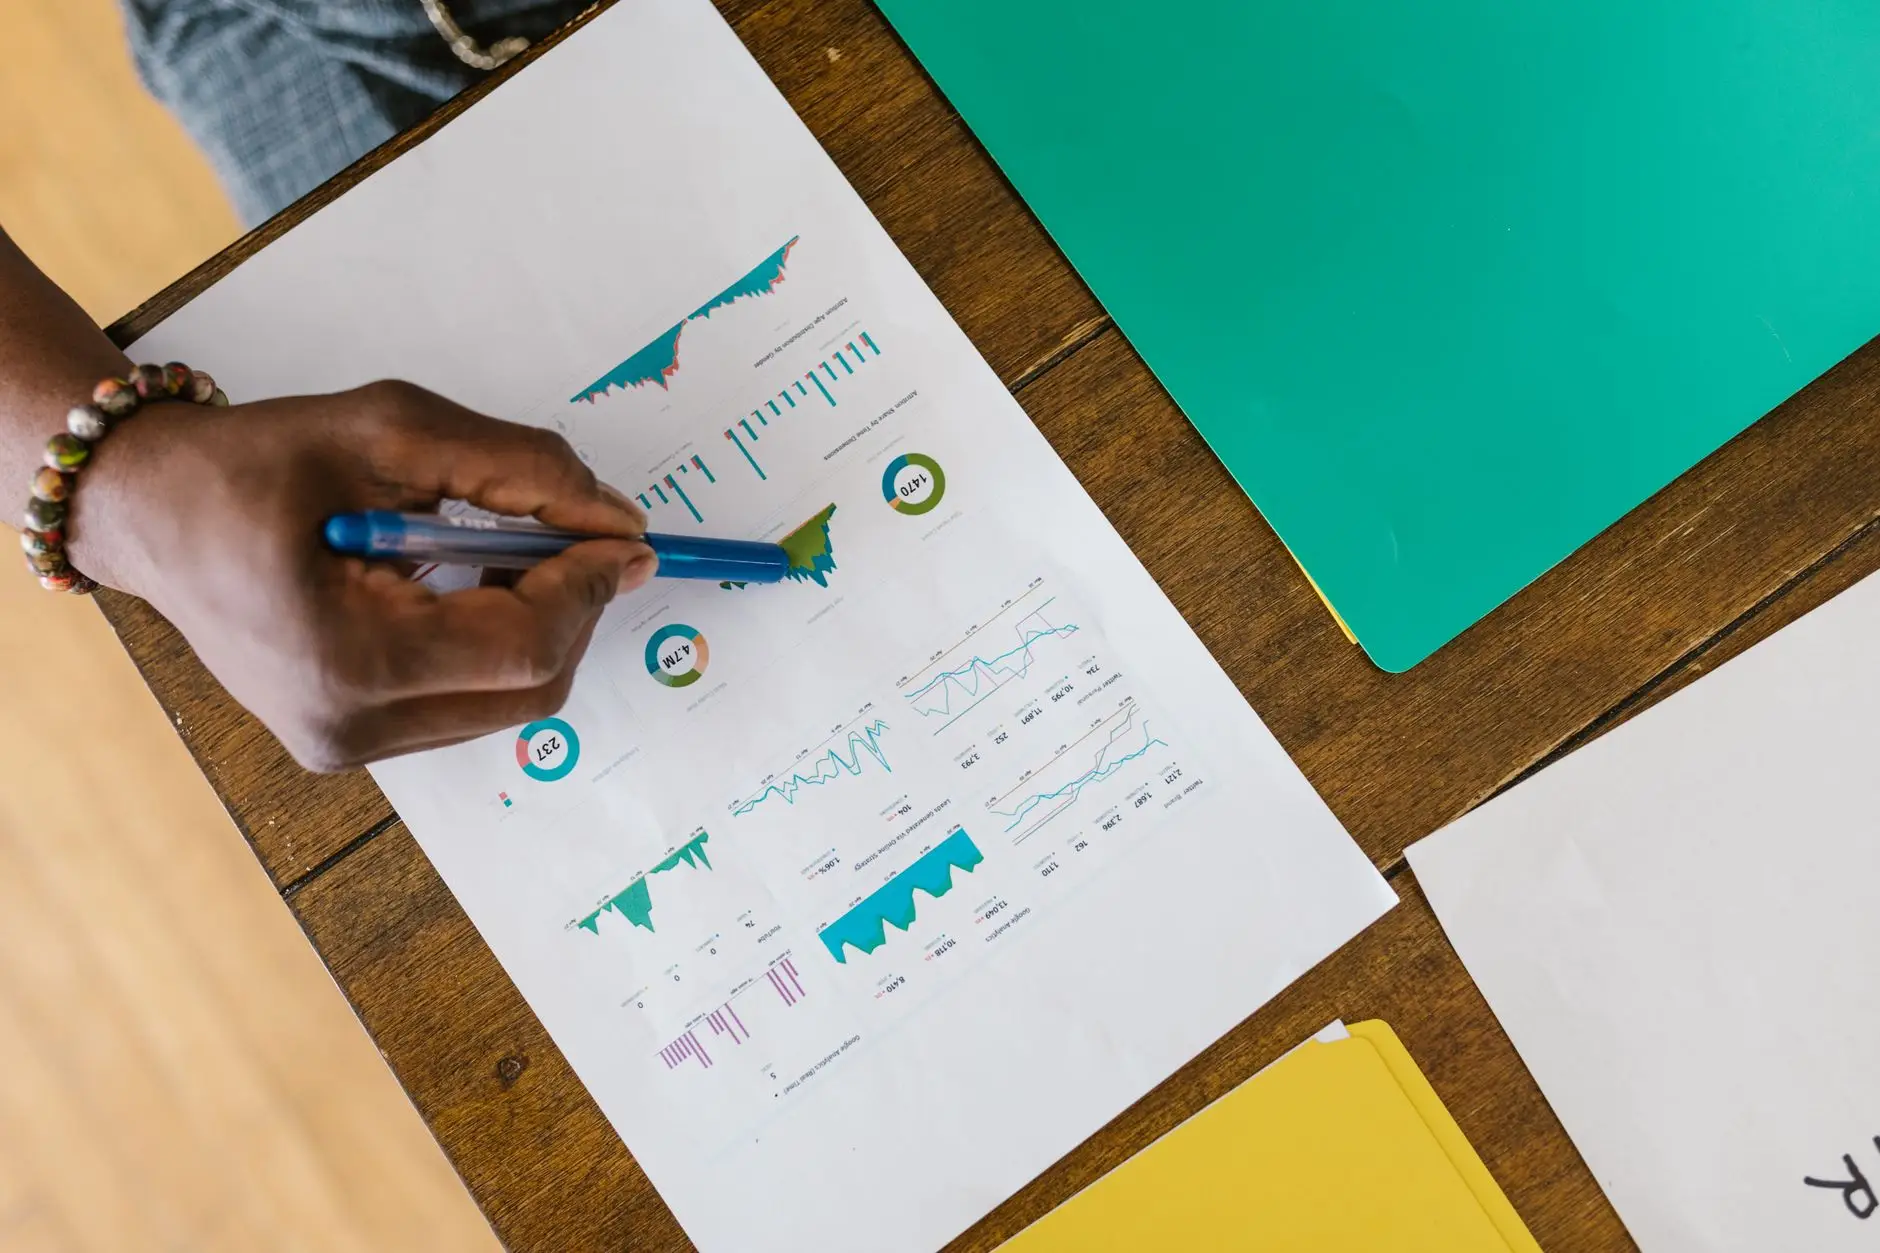
For many ambitious startup founders, the early days are a blur of product development, fundraising, and market validation. Data considerations often take a backseat, viewed as a ‘future problem’ to address once significant traction is gained. This oversight, however, is a critical miscalculation. The truth is, how a founder approaches data responsibility from day one profoundly impacts a startup’s ability to scale, attract investment, and ultimately, succeed.
Ignoring data protection principles, privacy laws, and cybersecurity best practices isn’t just a regulatory ticking time bomb; it’s an existential threat. When Founder Responsibility Matters Startups Scale, it means embedding a data-first mindset into the company’s DNA, not bolting it on as an afterthought. This article delves into why this early commitment is non-negotiable for any startup aiming for sustainable growth.
The Hidden Iceberg: Why Early Data Neglect Is Catastrophic
Imagine building a magnificent ship only to discover halfway across the ocean that its hull is riddled with unseen cracks. That’s precisely what happens when startups defer data responsibility. What might seem like minor data handling shortcuts in the beta phase can evolve into monumental liabilities as user bases expand, and data volumes explode. The cost of retrofitting privacy into a sprawling system is astronomically higher than building it in from the start.
Early-stage companies collect, process, and store various forms of data – from customer contact information and usage analytics to employee records and intellectual property. Each piece of data carries inherent risks. A lapse in data security, a misunderstanding of consent requirements, or a failure to implement robust data governance can lead to:
- Regulatory Fines: Major data protection laws like GDPR, CCPA, and emerging national frameworks impose steep penalties for non-compliance. Even small startups are not exempt.
- Reputational Damage: A data breach or privacy scandal can irrevocably shatter consumer trust, a startup’s most valuable asset.
- Lost Investment: Savvy investors increasingly scrutinize a startup’s data governance and cybersecurity posture as a key indicator of risk and long-term viability.
- Operational Disruption: Remediation efforts following an incident divert critical resources and attention away from core business objectives.
Legal & Financial Ramifications: The High Price of Non-Compliance
The regulatory landscape is unforgiving. Laws like the General Data Protection Regulation (GDPR) in Europe, the California Consumer Privacy Act (CCPA) in the United States, and numerous other global data protection frameworks require explicit adherence. For instance, GDPR fines can reach up to 4% of a company’s annual global turnover or €20 million, whichever is higher.
Consider a startup developing an innovative health app. If the founders overlook the stringent requirements for processing sensitive health data – such as obtaining explicit consent, implementing strong encryption, and defining clear data retention policies – they risk severe penalties. This isn’t just about financial loss; it can lead to forced cessation of operations or a complete loss of market viability. As Daniel Solove, a renowned privacy law expert, often notes, “Privacy is not about something to hide. It’s about something to protect.”
Building a Privacy-First Culture from Day One
The onus for establishing a strong data responsibility culture falls squarely on the founders. They must champion privacy and security, integrating it into every aspect of the business, from product design to hiring practices. This means more than just legal compliance; it’s about ethical data stewardship.
An article from the IAPP emphasizes that investing in privacy early is not just about avoiding fines, but about building trust and competitive advantage. A startup that can genuinely tell its users, partners, and investors that it prioritizes their data protection demonstrates maturity and foresight.
Operationalizing Data Responsibility: Practical Steps for Early-Stage Startups
Founders don’t need a dedicated privacy team from day one, but they do need a structured approach. Here’s a practical guide:
| Action Area | Pre-Scale (< 50 Employees) | Post-Scale (> 50 Employees) |
|---|---|---|
| Data Inventory & Mapping | Document what data you collect, why, and where it’s stored. | Automate data mapping, maintain records of processing activities. |
| Privacy Policy & Terms | Draft clear, concise, and legally compliant policies. | Regularly update policies, ensure clear consent mechanisms. |
| Security Basics | Implement strong passwords, MFA, basic access controls. | Adopt ISO 27001/SOC 2, regular penetration testing, incident response plan. |
| Employee Training | Mandatory basic privacy and security awareness. | Ongoing, role-specific training, phishing simulations. |
| Vendor Management | Vet critical third-party tools for data practices. | Comprehensive vendor due diligence, Data Processing Agreements (DPAs). |
| Data Subject Rights | Outline process for basic access/deletion requests. | Streamlined portal for all data subject rights, automated fulfillment where possible. |
Real-Life Scenario: The ‘Quick-Launch’ App’s Downfall
Consider ‘ConnectMe,’ a hypothetical social networking startup. In their rush to market, the founders, while brilliant engineers, deprioritized robust data practices. Their privacy policy was a generic template, user consent for data sharing was ambiguous, and their database had only basic security. They gained rapid traction. However, when a security researcher discovered a vulnerability that exposed user profile data, the damage was swift and severe.
Users fled, investors withdrew, and a class-action lawsuit quickly followed. The reputational blow was irreversible, and ConnectMe, despite its innovative idea, folded within months. Their failure wasn’t due to a lack of innovation but a profound neglect of data responsibility that amplified risks to an unmanageable level.
The Emerging Challenge of AI Governance
As AI becomes central to many startup offerings, the stakes for data responsibility soar. AI systems are data-hungry, and their fairness, transparency, and ethical implications are deeply intertwined with the data they consume. Founders building AI products must not only worry about data privacy but also about algorithmic bias, data quality, and the potential for automated decisions to harm individuals.
For more insights, exploring resources on EU AI & Data Protection Law can provide a foundational understanding of upcoming regulations that will impact AI-driven startups globally.
Conclusion: A Foundation for Trust and Growth
The journey from a nascent idea to a successful, scaled enterprise is fraught with challenges. However, one challenge that can be proactively mitigated is data risk. When Founder Responsibility Matters Startups Scale, it means recognizing that data protection is not merely a compliance burden but a strategic differentiator and an essential pillar of digital trust. By embedding privacy and security into their core operations from the very beginning, founders don’t just protect their users; they fortify their business, attract sustained investment, and lay a resilient foundation for long-term, ethical growth in an increasingly data-driven world.











Leave a Reply