



Why Sports Platforms Know Ticketing Platforms: Navigating Third-Party Privacy Risk

Share
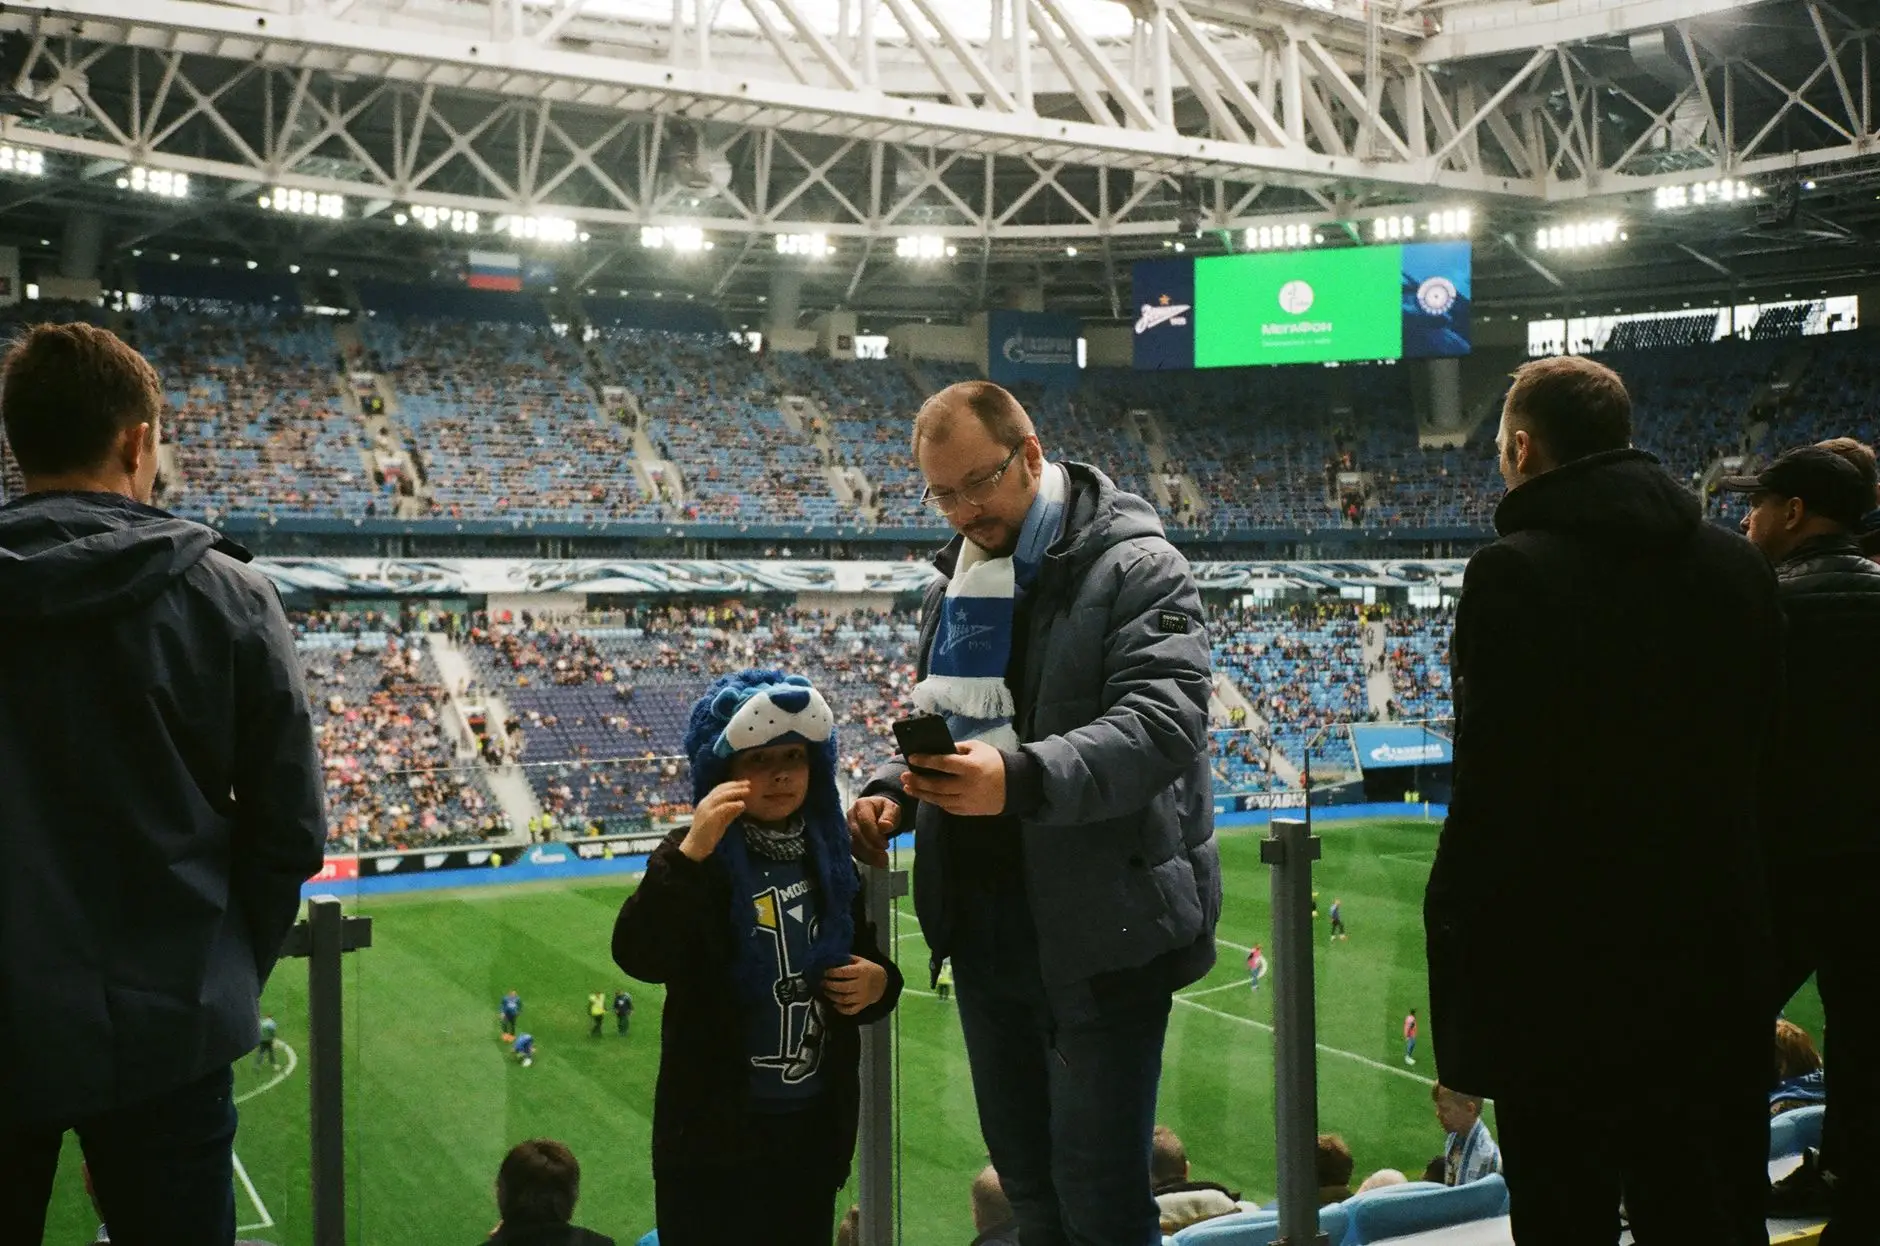
When a fan purchases a ticket to a championship game, they aren’t just securing a seat; they are initiating a complex, multi-layered data exchange. This transaction involves the sports organization, the ticketing platform, payment gateways, and often third-party marketing partners. For sports leagues and clubs, the convenience of digital ticketing creates a massive, invisible data pipeline that can either build fan loyalty or become a catastrophic liability.
The fundamental challenge is that the sports organization often owns the relationship with the fan, but the ticketing platform owns the most sensitive data points. This disconnect is exactly why Sports Platforms Know Ticketing Platforms are essential to their privacy strategy—not just as vendors, but as critical components of their digital risk profile.
The Invisible Data Pipeline: What is Being Shared?
The handshake between a sports entity and a ticketing provider is not limited to a name and an email address. To provide a seamless experience, these platforms exchange a high-density stream of information, including:
- Personally Identifiable Information (PII): Full names, home addresses, phone numbers, and birthdates.
- Financial Data: Payment methods, transaction histories, and billing details.
- Behavioral Data: Purchase frequency, seat preferences, and engagement with specific events.
- Technical Metadata: IP addresses, device IDs, and geolocation data used for mobile entry.
While this data facilitates personalized fan experiences, it also creates a lucrative target for cybercriminals. If a ticketing platform suffers a breach, the fallout doesn’t just hit the vendor; it hits the sports brand that the fans trust.
Why Sports Platforms Know Ticketing Platforms: The Hidden Risk Profile
Understanding why Sports Platforms Know Ticketing Platforms must be a priority for leadership comes down to three primary risks: third-party vulnerabilities, regulatory joint-controllership, and brand reputation.
1. Third-Party Vulnerabilities
Most sports organizations do not build their own ticketing software; they outsource it. This means the organization’s security posture is only as strong as the weakest link in their vendor chain. A vulnerability in the ticketing platform’s API can lead to unauthorized access to the entire fan database, bypassing the sports club’s own robust internal security.
2. The Compliance Trap: Joint Controllership
Under modern frameworks like the GDPR, the distinction between a “Data Controller” and a “Data Processor” is vital. In many ticketing arrangements, the sports club and the ticketing platform act as joint controllers. This means they both decide how and why data is processed. If the ticketing platform mishandles data, the sports club may still be held legally and financially liable for the breach.
“Data protection is not a checkbox for a single department; it is a continuous chain of trust that must extend to every partner in your digital ecosystem.”
To understand these legal nuances, organizations should review the compliance requirements that govern third-party data sharing.
3. Brand Reputation and Fan Trust
Fans view their relationship with a team as personal. If their credit card details are leaked through a third-party ticketing app, they won’t blame the software developer; they will blame the team. Rebuilding that trust is far more expensive than the cost of a rigorous security audit.
Scenario: The Mobile Entry Breach
Consider a mid-sized professional football league that utilizes a popular third-party mobile app for all stadium entries. To ensure speed, the app collects real-time geolocation data from fans as they approach the gates. A hacker exploits a vulnerability in the app’s cloud storage, gaining access to the location history and contact details of 50,000 fans.
Even though the league’s internal servers were never touched, the league is forced to issue a public apology, face a regulatory investigation, and provide credit monitoring to all affected fans. This illustrates how a vendor’s failure becomes a direct operational crisis for the sports platform.
Roles in the Ticketing Ecosystem
To manage risk, it is essential to define the roles within the data processing lifecycle. The following table outlines the typical division of responsibilities:
| Feature | Sports Platform (Controller) | Ticketing Platform (Processor/Joint Controller) |
|---|---|---|
| Primary Goal | Fan engagement and revenue. | Transaction processing and access control. |
| Data Ownership | Holds the ultimate relationship with the fan. | Manages the technical infrastructure. |
| Regulatory Duty | Ensures legal basis for processing. | Implements technical security measures. |
| Risk Impact | High (Brand and legal liability). | High (Operational and contractual liability). |
Effective data protection strategies require clear documentation of these roles in every contract.
Action Steps: A Due Diligence Checklist for Sports Leaders
To mitigate the risks associated with ticketing integrations, compliance and technology teams should implement the following steps:
- Conduct Vendor Audits: Do not rely on self-assessment questionnaires. Request independent SOC2 Type II reports or ISO 27001 certifications from your ticketing partners.
- Enforce Data Minimization: Only share the data that is strictly necessary for the transaction. If the ticketing platform doesn’t need a fan’s birthdate to issue a ticket, do not provide it.
- Review Data Processing Agreements (DPAs): Ensure your contracts explicitly define liability, breach notification timelines, and the right to audit.
- Implement Zero-Trust Architecture: Ensure that the connection between your internal systems and the ticketing platform is authenticated and encrypted at every stage.
- Map the Data Flow: Maintain an up-to-date inventory of exactly what data travels from your platform to the vendor and where it is stored.
For more information on how regulators view these relationships, the ICO guidance on controllers and processors provides a detailed framework for compliance.
Frequently Asked Questions
Is the sports club responsible if the ticketing vendor is hacked?
In many jurisdictions, yes. If you are deemed a joint controller or if you failed to conduct proper due diligence on the vendor, you may share legal responsibility for the breach.
How can we reduce the amount of data shared with vendors?
By practicing data minimization. Regularly review your API calls and data fields to ensure you are only sending the bare minimum required to complete the service.
Does mobile ticketing increase privacy risks?
Yes, because mobile ticketing often involves additional data points like device identifiers and real-time geolocation, which require stricter consent management.
Conclusion
The integration of digital commerce and fan engagement has revolutionized the sports industry, but it has also expanded the attack surface. Because Sports Platforms Know Ticketing Platforms are inextricably linked to their brand reputation, managing the privacy of that relationship is no longer optional. By treating ticketing providers as high-risk third parties rather than simple utility vendors, sports organizations can protect both their fans and their future.











Leave a Reply