



Beyond the Scoreboard: What Sports Platforms Know Athlete Data Privacy Demands

Share
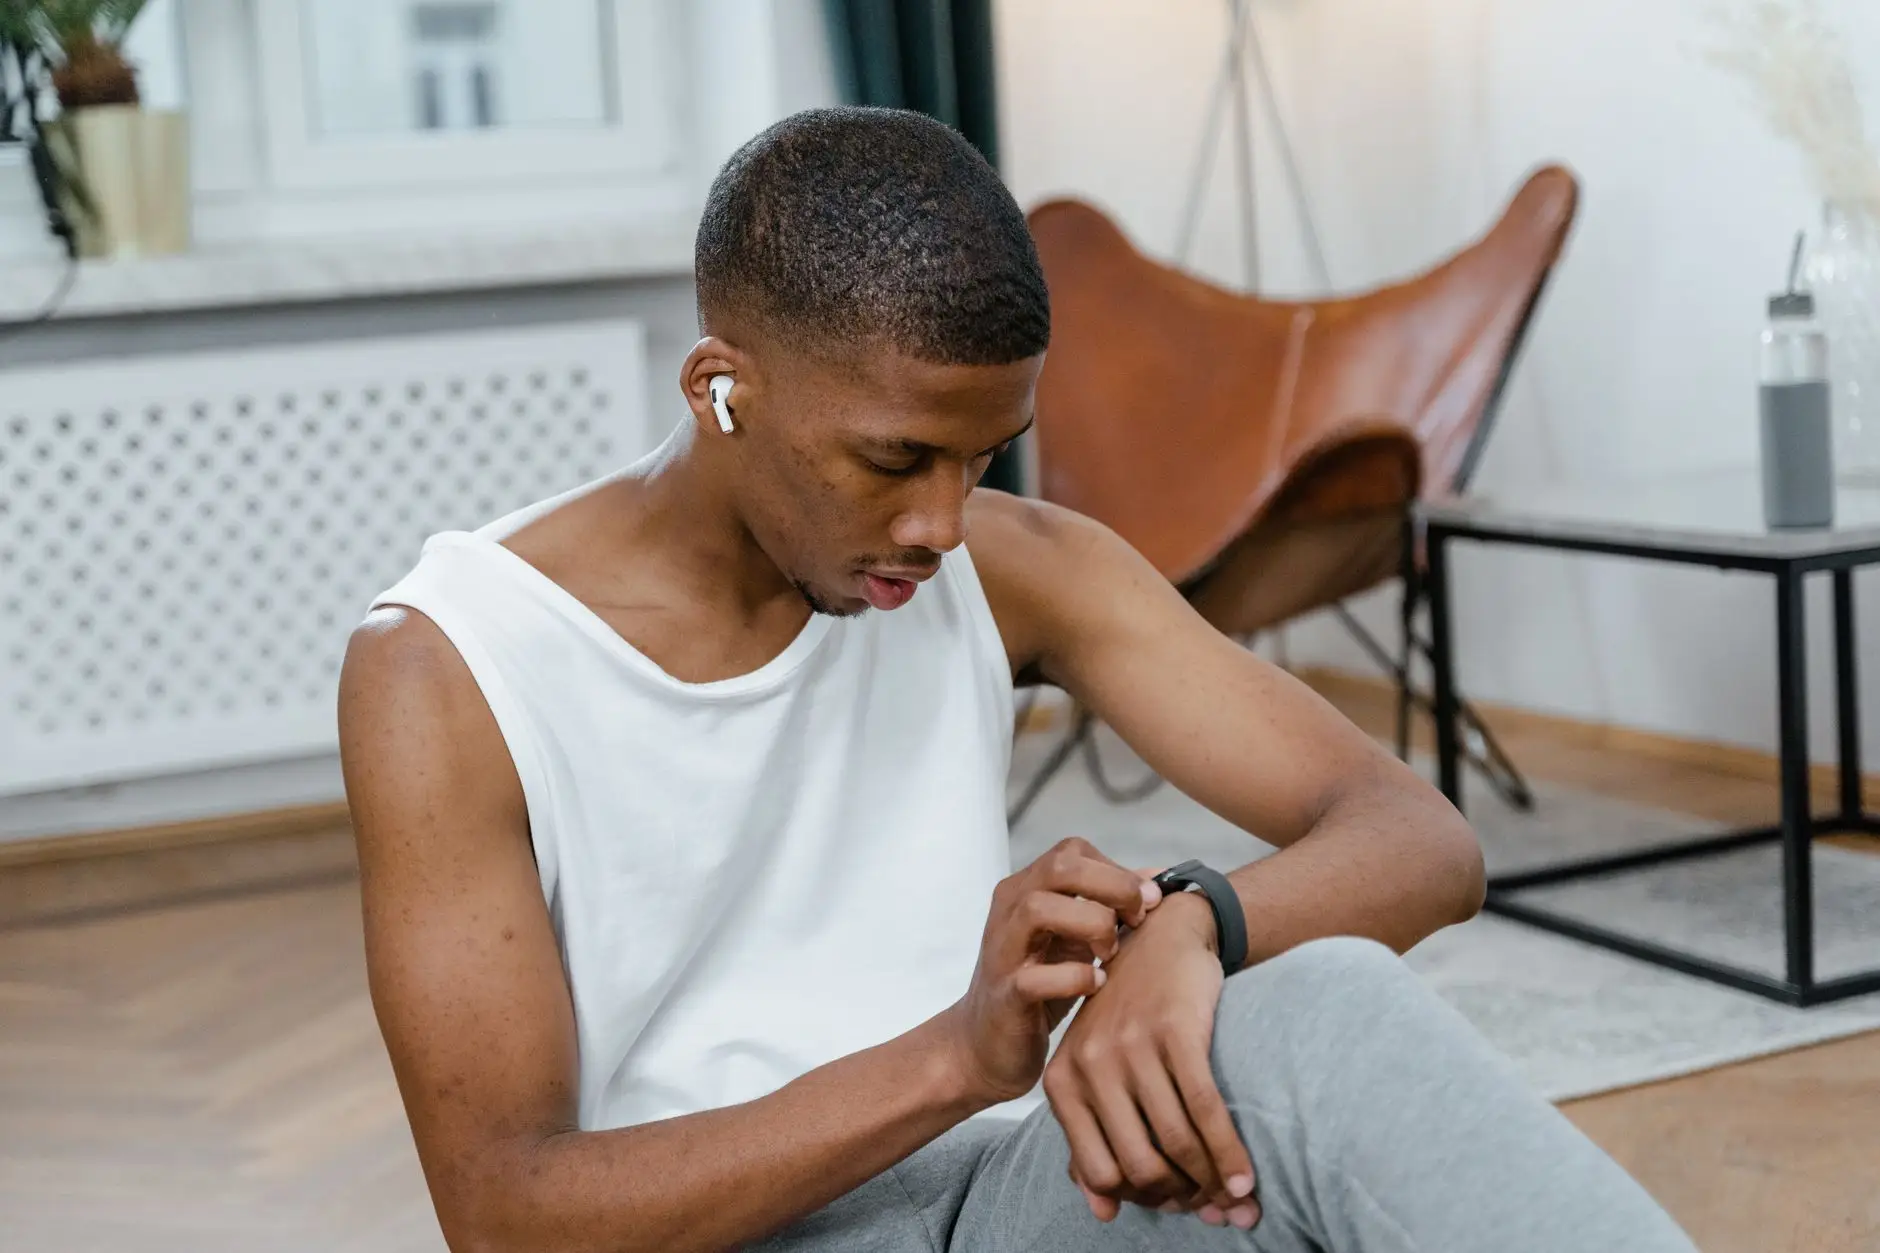
When a professional athlete syncs their wearable device after a training session, they are not just uploading heart rate variability or sleep duration. They are transmitting a biological fingerprint. This stream of highly sensitive information represents a new frontier of risk. For many developers and league operators, the sheer volume of performance metrics creates a sense of distraction from the underlying regulatory reality: as the industry evolves, many sports platforms know athlete privacy needs are shifting from simple security to complex, high-stakes governance.
The Data Landscape: More Than Just Statistics
The modern sports ecosystem relies on a continuous loop of data to drive performance, scouting, and fan engagement. However, this data is not monolithic. It falls into several sensitive categories that require distinct protection strategies. Understanding these categories is the first step in moving from a reactive to a proactive privacy posture.
- Biometric and Physiological Data: This includes heart rate, oxygen saturation, glucose levels, and hormonal profiles. Under many jurisdictions, this is classified as special category data.
- Locational Data: GPS tracking used for pitch positioning or recovery monitoring can reveal precise movements, training schedules, and even personal habits.
- Health and Medical Data: Injury histories, rehabilitation progress, and physiological responses to medication.
- Behavioral and Performance Data: Speed, fatigue indices, and reaction times which, while seemingly technical, can influence an athlete’s market value.
Because this information is so intimate, any failure in data protection protocols can lead to consequences far beyond a standard digital breach.
The Core Risks: What Sports Platforms Know Athlete Privacy Issues Are
The risks associated with athlete data are unique because they directly impact the subject’s livelihood. Unlike a leaked password, a leaked biometric profile cannot be changed. There are three primary risk vectors that platforms must address:
1. The Contractual Weaponization of Data
There is a growing tension between coaching staff and players regarding data ownership. If a team has access to real-time fatigue levels or declining physiological markers, they might use this information to suppress wages during contract negotiations or justify releasing a player. When performance analytics are used to make automated decisions about an athlete’s career, it triggers significant legal scrutiny under AI and automated decision-making laws.
2. The Secondary Market and Betting Risks
The explosion of sports betting has created a massive demand for “insider” data. If a platform suffers a leak of injury data or physiological status, that information becomes immediate, high-value intelligence for bad actors in the gambling industry. This creates a unique cybersecurity target for hackers looking to exploit the sports betting markets.
3. Identity and Physical Safety
Detailed locational data can be used to track athletes outside of official training hours. For high-profile individuals, this represents a significant physical security risk, potentially facilitating stalking or targeted harassment.
To visualize these risks, consider the following breakdown:
| Data Type | Primary Use Case | Primary Privacy Risk |
|---|---|---|
| Biometric | Recovery Monitoring | Health discrimination and identity theft |
| Locational | Tactical Analysis | Physical stalking and pattern tracking |
| Performance | Scouting/Training | Unfair contract negotiations/Market bias |
| Medical | Injury Management | Insurance exclusion and loss of career |
Real-World Scenario: The Negotiation Trap
Imagine a mid-tier professional basketball player, “Player X,” whose team uses a centralized performance platform. During a contract dispute, the team’s management acquires access to a report showing that Player X’s sleep quality and recovery metrics have declined by 15% over the last three months. While the player feels they are simply managing a minor, nagging injury, the team uses this physiological data to argue that the player’s “biological ceiling” has lowered, successfully negotiating a significantly lower contract. This scenario highlights why compliance teams must implement strict access controls: data intended for coaching must not be automatically available to the business/negotiation side of the organization.
“Data is the new currency in sports, but for the athlete, it is their biological identity. Treating it as mere statistics is a regulatory and ethical failure.”
— Industry standard for digital trust in sports tech.
Regulatory Realities: Navigating Special Category Data
For platforms operating globally, the legal landscape is daunting. Under the GDPR, biometric data used for the purpose of uniquely identifying a natural person is treated as a “special category” of data. This means that standard legal bases for processing, such as “legitimate interest,” are often insufficient. Platforms must frequently rely on explicit, informed, and granular consent.
Specifically, Article 9 of the GDPR prohibits the processing of such data unless specific derogations apply. For sports platforms, this means that a blanket “I agree to the Terms and Conditions” is likely legally inadequate. Consent must be specific to the type of data being collected and the specific purpose for which it is being used.
Strategic Implementation: A Framework for Sports Platforms
To build a sustainable and trustworthy platform, technology teams and founders should adopt a “Privacy by Design” approach. This is not just about encryption; it is about the architecture of how data flows through the organization.
- Data Minimization: Do not collect heart rate data if you only need to know if an athlete has completed a workout. If the data isn’t necessary for the stated purpose, it should not be captured.
- Purpose Limitation: Ensure that data collected for “performance optimization” is technically walled off from data used for “commercial analytics” or “contractual management.”
- Granular Consent Management: Implement user interfaces that allow athletes to opt-in to specific data streams (e.g., “Yes to sleep tracking, No to GPS tracking”).
- Robust Access Governance: Use Zero Trust principles. A scout should not have the same access levels as a team doctor.
Frequently Asked Questions
Who owns the athlete’s biometric data?
Ownership is a complex legal question that varies by jurisdiction, but most modern privacy frameworks view the individual as the primary controller of their personal biological data. Platforms are merely processors.
Can an athlete refuse to wear a tracker?
This is a matter of employment law and collective bargaining agreements. However, from a privacy perspective, platforms should strive to make data collection voluntary and provide clear consequences for non-participation.
Conclusion
The intersection of elite performance and digital surveillance is fraught with tension. As technology becomes more invasive, the responsibility of the developer increases. Ultimately, the most successful sports platforms know athlete trust is their most valuable asset. By prioritizing rigorous data protection, respecting the nuances of biometric sensitivity, and building transparent consent models, platforms can drive athletic excellence without compromising the fundamental rights of the individuals they serve.











Leave a Reply