



Why Privacy Culture Should Matter More to Schools

Share
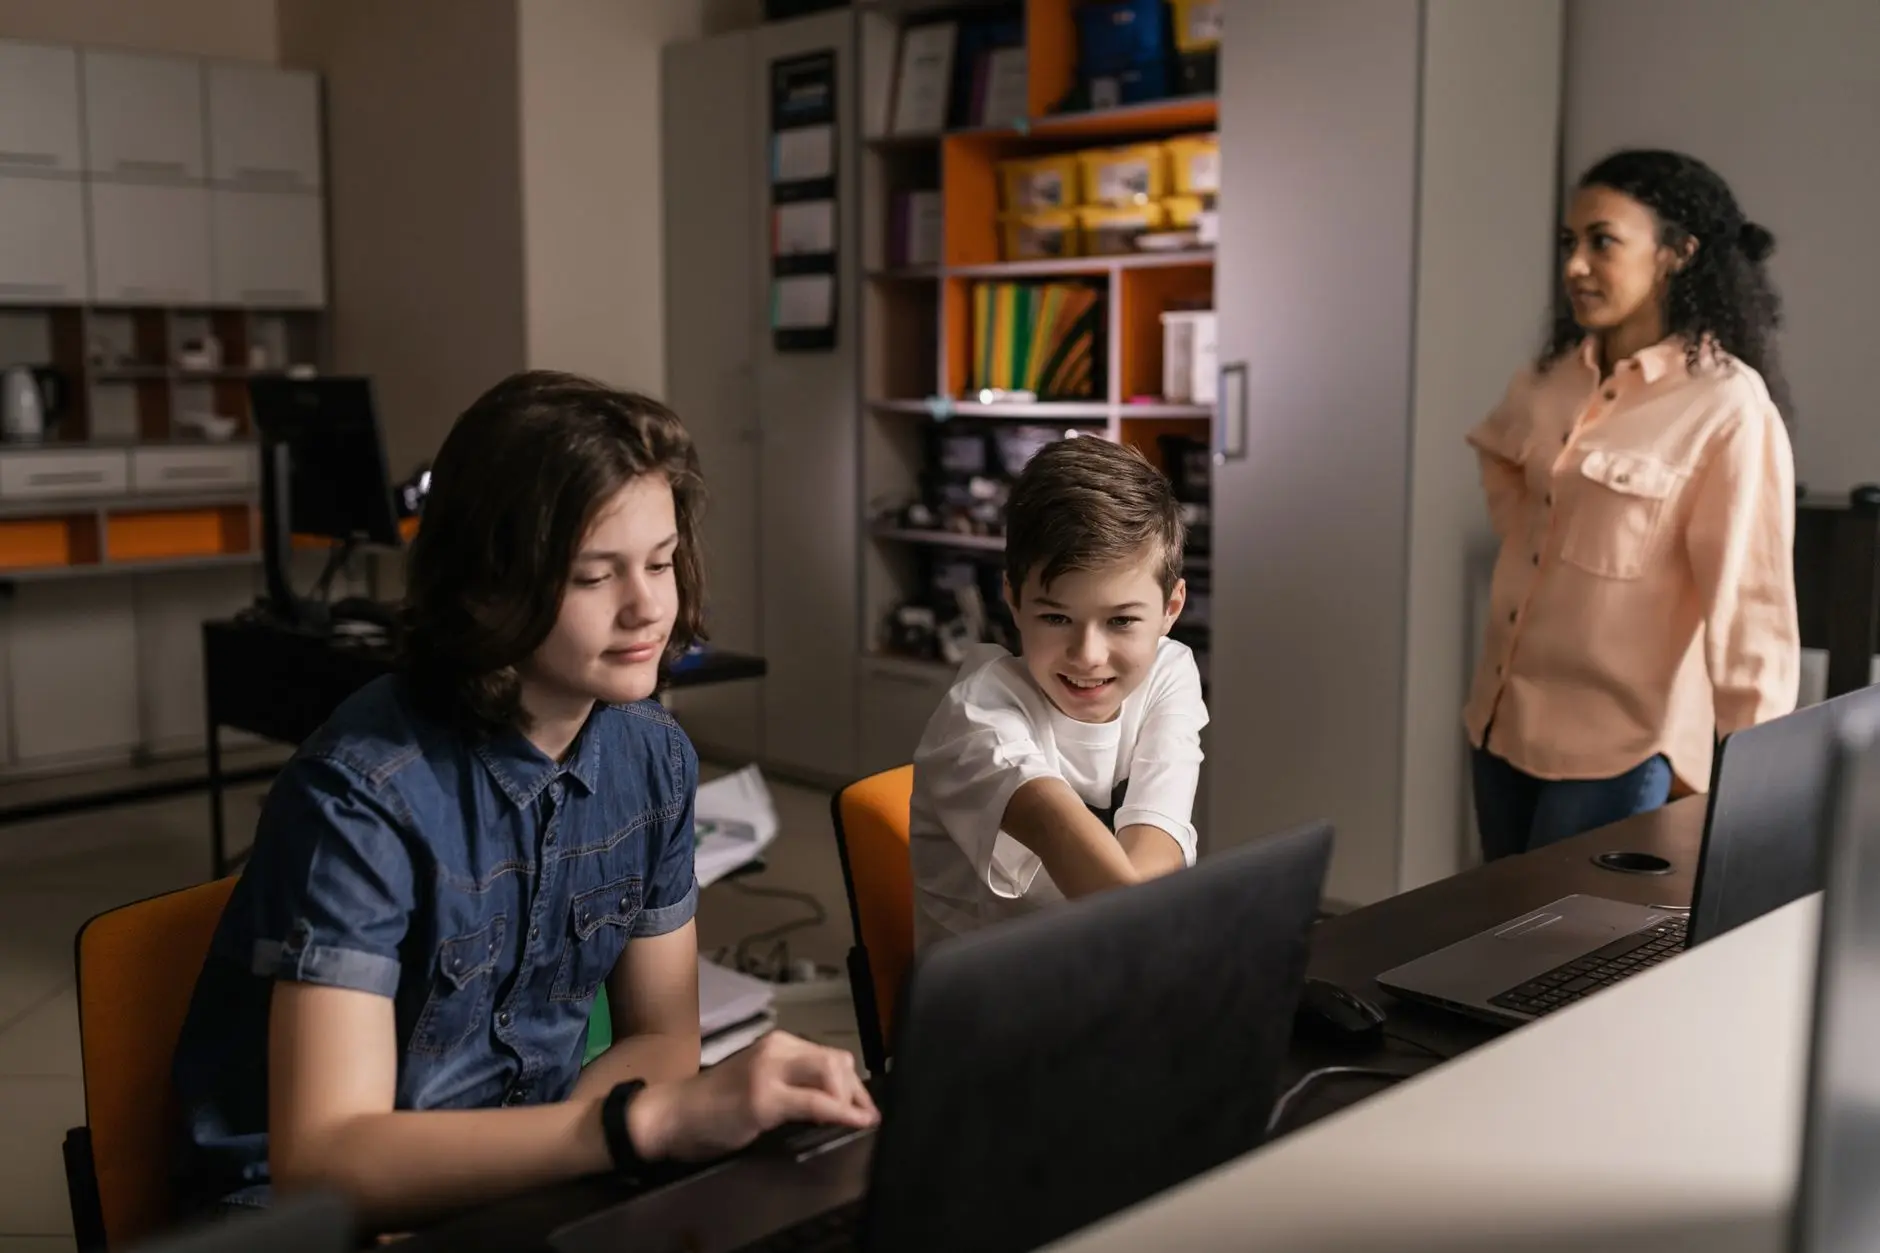
Educational institutions have undergone a massive digital transformation over the past decade. Classrooms once defined by chalkboards and paper folders now rely entirely on cloud-based learning management systems, tablet applications, and automated attendance tracking tools. While these technologies expand educational access, they also create a relentless stream of digital footprints. Children and teenagers now generate sensitive biometric, behavioral, and academic records long before they ever enter the workforce. Despite this influx of digital collection, institutional accountability often lags behind, proving why a robust privacy culture should matter more to schools at every level.
Protecting student information is no longer just an IT task or a regulatory checkbox for compliance teams. When educational boards treat data privacy as a secondary administrative burden, they expose minors to long-term risks such as identity theft, predatory marketing, and profiling. Fostering a genuine privacy-first mindset requires shifting institutional values so that every teacher, administrator, and vendor views data stewardship as a core component of student welfare.
The Growing Digital Footprint of K-12 and Higher Education
Modern edtech ecosystems track far more than traditional report cards. Software platforms monitor keystrokes, webcam feeds during remote exams, precise location data, and even emotional sentiment through adaptive learning programs. According to guidance from regulatory bodies like the Federal Trade Commission, the collection of children’s data demands rigorous oversight and transparent consent mechanisms. Yet, many schools adopt new applications hastily without conducting thorough vendor risk assessments.
When a school district signs up for a free cloud service in exchange for student engagement analytics, it may inadvertently compromise confidentiality. If the platform lacks proper encryption or data-sharing safeguards, vulnerable records can end up exposed in a public leak. Building a strong data protection framework means vetting these third-party platforms before they ever touch a classroom device.
Real-World Consequences of Lax School Security
Consider the cautionary scenario of a suburban school district that suffered a severe ransomware attack during midterm examinations. Hackers exfiltrated gigabytes of data containing confidential special education evaluations, psychological counseling notes, and home addresses. Because the district lacked a cohesive security mindset, teachers had shared administrative passwords and ignored basic phishing warnings.
The fallout extended far beyond financial extortion. Families faced immediate distress, students experienced disrupted learning schedules, and the district faced intense scrutiny from state regulators and litigators. This incident illustrates why technical firewalls alone are insufficient. Without a lived institutional culture that values digital boundaries, human error will continually undermine technical defenses.
Comparing Compliance Versus Actual Privacy Culture
Many educational leaders confuse legal compliance with operational safety. While complying with regulations such as FERPA or COPPA is mandatory, legal checklists rarely address day-to-day behavioral habits. The table below outlines the core differences between a tick-box compliance approach and a sustainable privacy culture.
| Feature | Compliance-Driven Approach | Privacy Culture Approach |
|---|---|---|
| Primary Motivation | Avoiding fines and lawsuits | Protecting student trust and dignity |
| Staff Engagement | Annual mandatory training videos | Continuous dialogue and practical workshops |
| Vendor Vetting | Signing standard contract clauses | Rigorous ongoing audits and data minimization |
| Incident Response | Reactive panic and public relations control | Proactive transparency and student-first support |
Actionable Steps for Educational Institutions
Transforming how an educational institution handles information requires deliberate leadership and consistent education. School boards, principals, and IT directors can implement several practical measures immediately:
- Adopt Data Minimization: Collect only the student information strictly necessary for educational purposes and delete it when no longer needed.
- Empower Staff Training: Move beyond boring compliance seminars by running realistic phishing simulations and interactive privacy workshops for teachers.
- Enforce Strict Vendor Accountability: Require all educational software providers to sign binding data processing agreements detailing how they store and protect student records.
- Involve Parents and Students: Provide clear, jargon-free explanations of what digital tools are used in classrooms and how families can exercise their regulatory rights.
Frequently Asked Questions
Why is student data privacy more critical than corporate data privacy?
Minors lack the legal capacity to consent and cannot easily change compromised biometric or historical educational records. Protecting their data establishes a safe foundation for their future digital identities.
How can teachers promote privacy without being technical experts?
Teachers can model good digital hygiene by using strong passwords, avoiding unapproved third-party apps, and teaching students basic concepts about online safety and consent.
Conclusion
Ultimately, safeguarding the digital lives of students is an ethical imperative. When educational leaders recognize that a strong privacy culture should matter more to schools, they do more than prevent data breaches. They teach the next generation how to navigate a digital world with awareness, respect, and confidence in their fundamental right to privacy.











Leave a Reply