



Why Privacy Culture Should Matter More to Healthcare Providers

Share
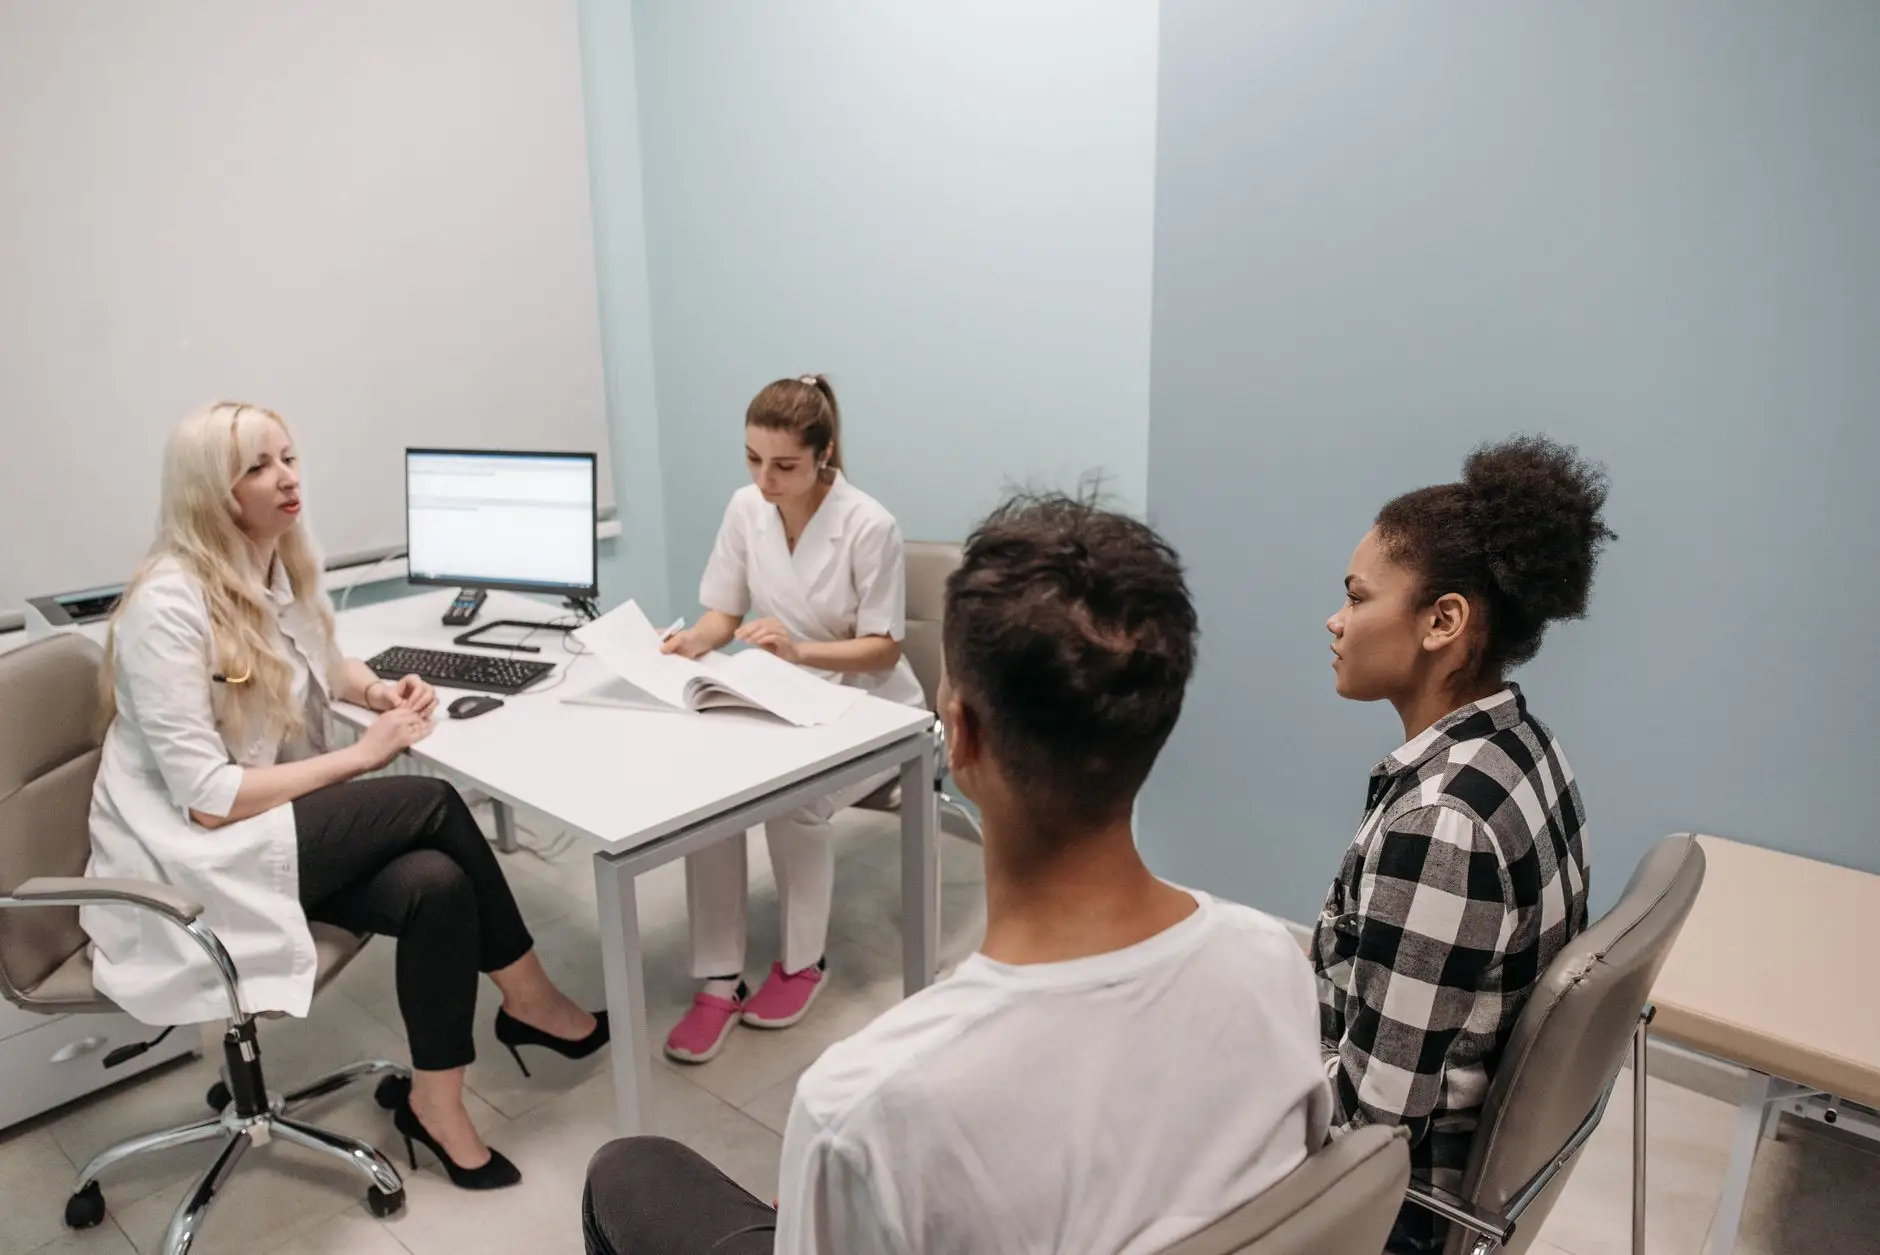
Beyond the Checklist: The Human Side of Health Data
Regulatory frameworks like HIPAA, GDPR, and local medical confidentiality laws demand rigorous safeguards. Yet, data breaches and unauthorized record lookups continue to plague hospitals, clinics, and digital health startups. Why do breaches happen even when organizations pass annual audits? The answer lies in organizational psychology. When medical institutions treat data protection merely as a legal obligation rather than an internal value system, vulnerabilities multiply. This reality explains why Culture Matter More healthcare providers need to recognize that technology and policies alone cannot stop human error or malicious intent.
Healthcare environments are fast-paced, high-stress workplaces where clinicians often prioritize rapid patient care over administrative protocols. If an organization lacks a healthy internal environment regarding information stewardship, staff will bypass security controls to save time. Cultivating a robust safeguarding mindset shifts employee behavior from reluctant compliance to active protection.
The Real Cost of a Broken Privacy Ecosystem
When patient records are exposed, the fallout extends far beyond regulatory fines or public relations nightmares. Medical data is among the most sensitive information in existence. It encompasses mental health histories, genetic profiles, chronic illness diagnoses, and financial details. A compromise of this data erodes the fundamental doctor-patient relationship.
Consider a mid-sized regional hospital where an administrative employee casually browses the medical file of a high-profile local politician out of curiosity. No ransomware was deployed, and no external hacker breached the perimeter. Yet, the internal policy violation severely damages institutional reputation and breaches legal standards. Incidents like this highlight why data protection protocols fail without widespread organizational buy-in.
According to the U.S. Department of Health and Human Services (HHS), unauthorized internal access remains a persistent vector for healthcare privacy incidents, proving that technical firewalls cannot police human curiosity.
Compliance vs. Culture: Spotting the Difference
Many clinics assume that installing end-to-end encryption and holding a once-a-year training seminar checks every necessary box. In reality, compliance is just the baseline. A true internal ethos transforms how every staff member handles information daily.
| Feature | Compliance-Driven Approach | Culture-Driven Approach |
|---|---|---|
| Primary Driver | Avoiding regulatory penalties | Protecting patient dignity and trust |
| Training Frequency | Annual checkbox webinar | Continuous, contextual, and interactive |
| Incident Reporting | Feared, hidden, or avoided | Encouraged, investigated, and learned from |
| Staff Attitude | Burdensome administrative red tape | Shared professional responsibility |
As privacy governance expert Dr. Alan Westin once noted, “The truest test of an ethical information policy is how staff behave when no auditor is watching.” This principle is especially vital in modern digital health ecosystems where telemedicine platforms and third-party vendors handle millions of patient records.
Actionable Steps for Healthcare Leaders
Building a resilient internal environment requires deliberate leadership and consistent reinforcement. Business leaders, compliance officers, and medical directors can take practical steps to transform their institutional mindset:
- Redefine Training: Move away from dense legal lectures. Use realistic simulations, short case studies, and interactive discussions that reflect daily clinical workflows.
- Empower Whistleblowers and Reporters: Establish anonymous reporting channels where staff can flag risky behaviors or unsecured devices without fear of professional retaliation.
- Lead from the Top: Hospital executives and clinical leads must visibly follow the same protocols they enforce, setting a standard for junior staff and visiting physicians.
- Integrate Privacy into compliance Audits: Evaluate not just software vulnerabilities, but also behavioral patterns, workstation habits, and physical document disposal practices.
Frequently Asked Questions
Why do healthcare providers struggle with information safeguarding?
Healthcare workers operate under extreme time constraints where saving lives or expediting patient flow naturally takes precedence over administrative security tasks, leading to shortcuts.
How does an ethical framework reduce data breaches?
When staff understand the personal and professional impact of data exposure, they are far less likely to fall for phishing emails, share passwords, or access records without authorization.
Is regulatory adherence enough to secure patient data?
No. Regulations provide minimum legal standards, but they cannot dictate human attitude, ethical judgment, or vigilance during high-stress medical emergencies.
Conclusion
Protecting medical records is ultimately about protecting people. While software patches, encryption tools, and legal frameworks are essential components of modern healthcare infrastructure, they are incomplete without a dedicated workforce standing behind them. When healthcare executives realize that Culture Matter More healthcare providers can foster an environment where trust, security, and patient dignity thrive side by side, ensuring long-term resilience against evolving digital threats.












Leave a Reply