

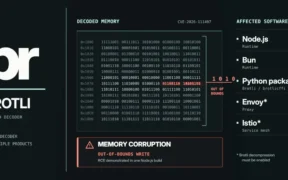
A memory-corruption flaw in Google’s Brotli decoder has been identified, impacting Node.js, Bun, and Python packages. The vulnerability could lead to remote code execution through maliciously crafted compressed data.
Security researchers from Eye Security have remotely disabled a background updater on 2 million computers to prevent a vulnerable piracy app from being exploited by botnet operators.

CISA has added critical vulnerabilities in Collabora Online Built-in CODE Server and Arista VeloCloud Orchestrator to its Known Exploited Vulnerabilities catalogue following evidence of active exploitation.
The Nigerian Communications Commission (NCC) has unveiled a new framework to facilitate zero-rated access to educational platforms and content across Nigeria.
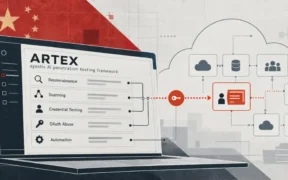
Microsoft has attributed a supply chain attack on ConnectWise Cloud Backup to the China-linked actor Storm-0940, who utilised the ARTEX AI agentic framework to accelerate the intrusion.












