



NetamLoader Malware Targets Asian Government Windows 10 Systems

Share
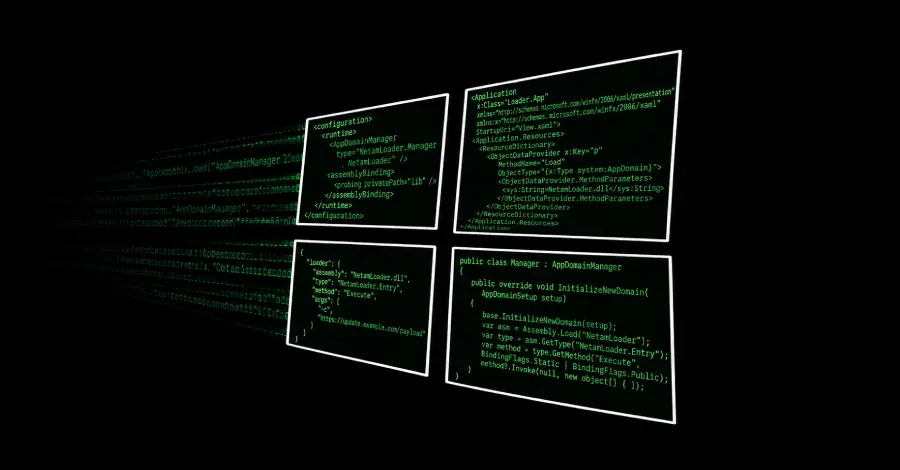
Kaspersky researchers have identified a sophisticated malware infection chain, codenamed NetamLoader, targeting government organisations in Asia. The attack specifically focuses on a custom Windows 10 build used exclusively by government entities within the region.
The high level of targeting suggests the campaign is designed to penetrate specialised administrative environments rather than broad consumer networks.
Advanced .NET Injection Techniques
The malware employs a previously undocumented .NET assembly-loading framework to carry out its operations. By utilising .NET injection, the attackers can load malicious code directly into memory, which helps evade detection by many traditional endpoint security solutions.
This injection method allows the NetamLoader framework to execute complex commands within the context of legitimate system processes. This technique makes forensic investigation and the identification of malicious activity significantly more difficult for security teams.
While the technical sophistication of the injection framework is clear, the specific identity of the threat actor behind the campaign has not yet been confirmed.










Leave a Reply