



Attackers Impersonate IT Support on Microsoft Teams to Compromise Active Directory

Share
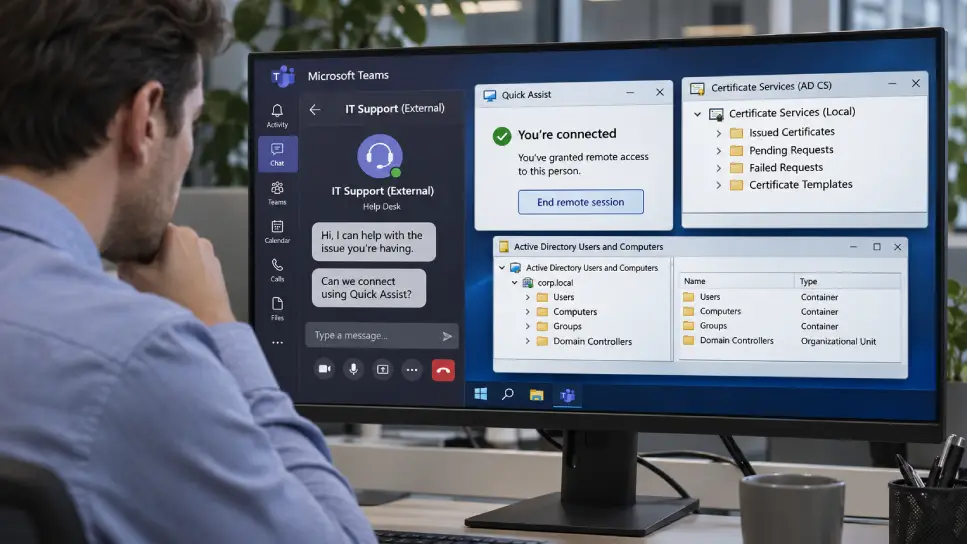
Attackers are impersonating IT support staff on Microsoft Teams to gain remote access to employee workstations, subsequently exploiting insecure Active Directory Certificate Services (AD CS) to steal sensitive company data.
Microsoft has investigated two separate intrusions involving this specific attack chain. In one of these instances, the intrusion resulted in the theft of company data.
The threat actors use social engineering to convince employees via Microsoft Teams to grant them remote control of their computers. Once initial access is established on a workstation, the attackers target misconfigured or insecure AD CS settings within the corporate network.
By exploiting these certificate services, the attackers are able to obtain login certificates for highly privileged accounts. In the investigated cases, this process allowed the attackers to secure a certificate for a domain controller, providing them with extensive control over the affected organisation’s identity infrastructure.
This method highlights a growing trend of using internal collaboration tools as a primary vector for social engineering. By leveraging the inherent trust associated with internal messaging platforms, attackers can more effectively bypass traditional email-based phishing defences.
To mitigate these risks, organisations should perform regular audits of their Active Directory Certificate Services configurations. Security teams should specifically review certificate templates to ensure they do not allow for unauthorised privilege escalation and monitor for any unusual or unexpected certificate issuance.













Leave a Reply