



Hackers Compromise Nearly 1,000 Online Stores in Evasive Magento Campaign

Share
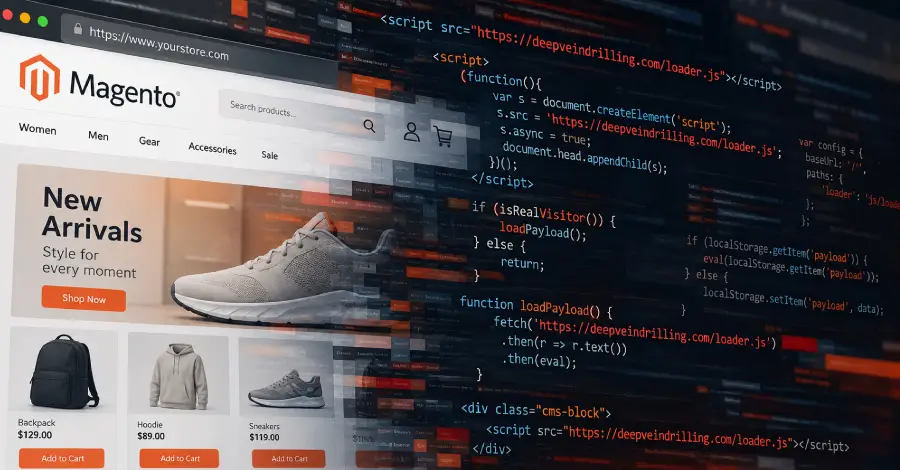
Threat actors have compromised 953 online stores in an ongoing cyber attack active since July 2025, with the vast majority of target websites running on the Magento e-commerce platform.
According to findings from e-commerce security specialist Sansec, the campaign stealthily inserts small code snippets into online storefronts. When customers visit an infected store, the code dynamically loads malicious JavaScript payloads through Content Management System (CMS) blocks.
Scanner-Evading Injection Techniques
The attackers designed the malicious code specifically to evade automated security scanners and integrity monitors. By abusing Magento CMS blocks, the scripts load secondary payloads only under specific user interactions, concealing the compromise from routine website checks.
Sansec indicated that the primary objective of the obfuscated JavaScript loaders is to execute unauthorized scripts during checkout operations, exposing payment credentials and customer data to the threat actors.
Mitigation and Platform Security
Magento, an open-source e-commerce platform maintained by Adobe, remains a prime target for digital web skimming and Magecart-style operations owing to its broad market presence.
E-commerce merchants operating Adobe Commerce or Magento Open Source are advised to inspect database CMS blocks, monitor file integrity, and audit third-party integrations for unauthorized alterations.










Leave a Reply