



Dutch Police Arrest Man Linked to ShinyHunters Group

Share
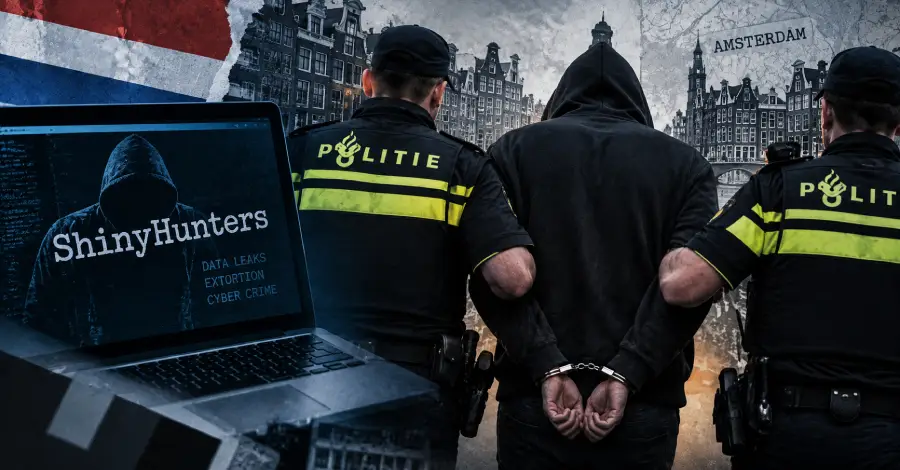
Dutch authorities have confirmed the arrest of a 24-year-old man in Amsterdam in connection with an investigation into the hacker group ShinyHunters.
The Politie Landelijke Opsporing en Interventies (National Investigation and Intervention Police) announced in a statement on Monday that the individual is expected to appear before the Rotterdam District Court on 29 September 2026.
While law enforcement officials did not officially name the suspect, security researchers and journalists have identified the individual as Pepijn van der Stap, known online as “Umbreon.” Van der Stap has a prior history with law enforcement, having been apprehended in 2023 in relation to a series of data thefts and extortion attempts.
Van der Stap is currently the offensive security lead at the Dutch company Neo Security. He has previously worked at the cybersecurity firm Hadrian and volunteered with the Dutch Institute for Vulnerability Disclosure (DIVD).
ShinyHunters and FBI Breach Claims
The arrest occurs as the ShinyHunters group faces intense scrutiny following claims of a massive breach targeting the U.S. Federal Bureau of Investigation (FBI). The group recently claimed responsibility for siphoning terabytes of sensitive data from the FBI’s job application portal, apply.fbijobs.gov.
A representative for ShinyHunters stated that the operation was not a financially motivated extortion attempt, but rather a “marketing campaign” intended to combat disinformation and increase the group’s visibility. The group maintained that the attack was not an attempt to solicit ransom.
Technical Exploitation Details
ShinyHunters claimed to have exploited a zero-day vulnerability in Oracle PeopleSoft to gain unauthorised access to the FBI’s systems. However, technical assessments of the incident suggest a different method may have been used to bypass security controls.
Security analysts believe the group may have utilised a URL-encoding technique to circumvent web application firewall (WAF) rules designed to mitigate CVE-2026-35273.












Leave a Reply