



Proofpoint Researcher Warns AI Overreliance Leads to Flawed Cyberattacks

Share
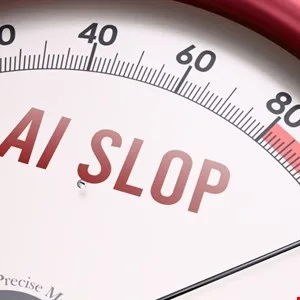
Selena Larson, a principal threat researcher at Proofpoint, has observed that cybercriminals’ increasing reliance on artificial intelligence (AI) is often resulting in less effective and more error-prone attacks.
Speaking at the IRISSCON 2026 conference in Dublin, Larson noted that while AI has improved the speed and scalability of malicious campaigns, it has not significantly increased the sophistication of threat actors. She described the resulting errors in AI-generated content as “AI slop.”
Flaws in Malware and Phishing Campaigns
Proofpoint researchers have identified instances where AI-generated malware contains non-functional code or comments that contradict the actual behaviour of the software. This lack of precision makes the malware easier for security tools to identify.
The researcher also highlighted a decline in the quality of phishing lures. For example, the threat actor group TA4903, which historically utilised sophisticated lures to impersonate US government entities for business email compromise (BEC) campaigns, has seen a drop in effectiveness after adopting AI tools. Larson reported that AI-generated emails from the group often feature mismatched subjects and attachments, or even blank message bodies.
Additionally, the group has begun using AI coding tools to create phishing websites. These “vibe coded” sites often share a simplistic, uniform appearance in terms of colour and formatting, which aids in detection by targets and security systems.
Vulnerability Exploitation and Noisy Attacks
Even in the realm of vulnerability exploitation, AI-driven methods have shown significant weaknesses compared to human-led activity. Larson cited the ‘BlueMoon’ exploit chain, first observed in August 2026, which involved three browser vulnerabilities.
In this instance, threat actors used large language models (LLMs) to write exploits based on patch release notes. However, the resulting AI-generated exploits were highly flawed, frequently failing to behave as intended and generating significant “noise” that made the attempts easily identifiable to defenders.
Larson concluded that AI should be viewed as a productivity tool rather than a sophistication enhancer. While AI allows attackers to exploit known vulnerabilities more rapidly, she noted that fundamental cyber defence priorities remain unchanged.









Leave a Reply