



Iran-Aligned Actor Targets Israeli Individual and Kurdish Government Cloud

Share
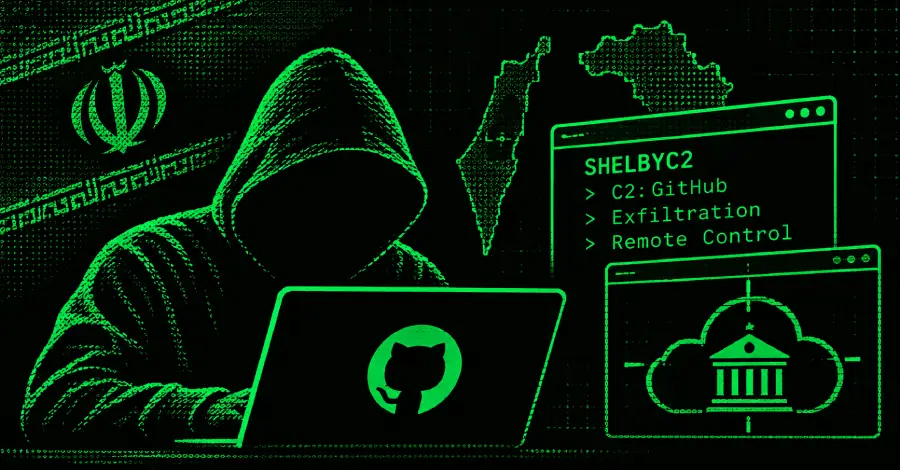
A cyber espionage campaign attributed to an Iran-aligned threat actor has targeted sensitive individuals and government infrastructure in the Middle East. Researchers at Dream Research Labs have disclosed that the actor, known as DarkBlinders, successfully compromised a high-profile individual in Israel and a government cloud environment in the Kurdistan Region of Iraq.
Targeted Intelligence Gathering
The campaign was active between August and October 2026. The scope of the operation, which included the compromise of a government cloud, suggests a strategic focus on intelligence gathering through state-level digital environments.
While the specific technical methods used to breach the cloud environment and the high-profile Israeli target have not been fully detailed in the initial research, the attribution to DarkBlinders indicates a sophisticated, state-aligned operation. The targeting of both Israeli and Kurdish entities underscores the geopolitical motivations often associated with such espionage activity.
The breach of government cloud services highlights ongoing vulnerabilities in regional administrative infrastructure. Further technical details regarding the specific vulnerabilities exploited by DarkBlinders are expected as investigations continue.












Leave a Reply