



What Online Stores Need to Explain Before Collecting Customer Addresses

Share
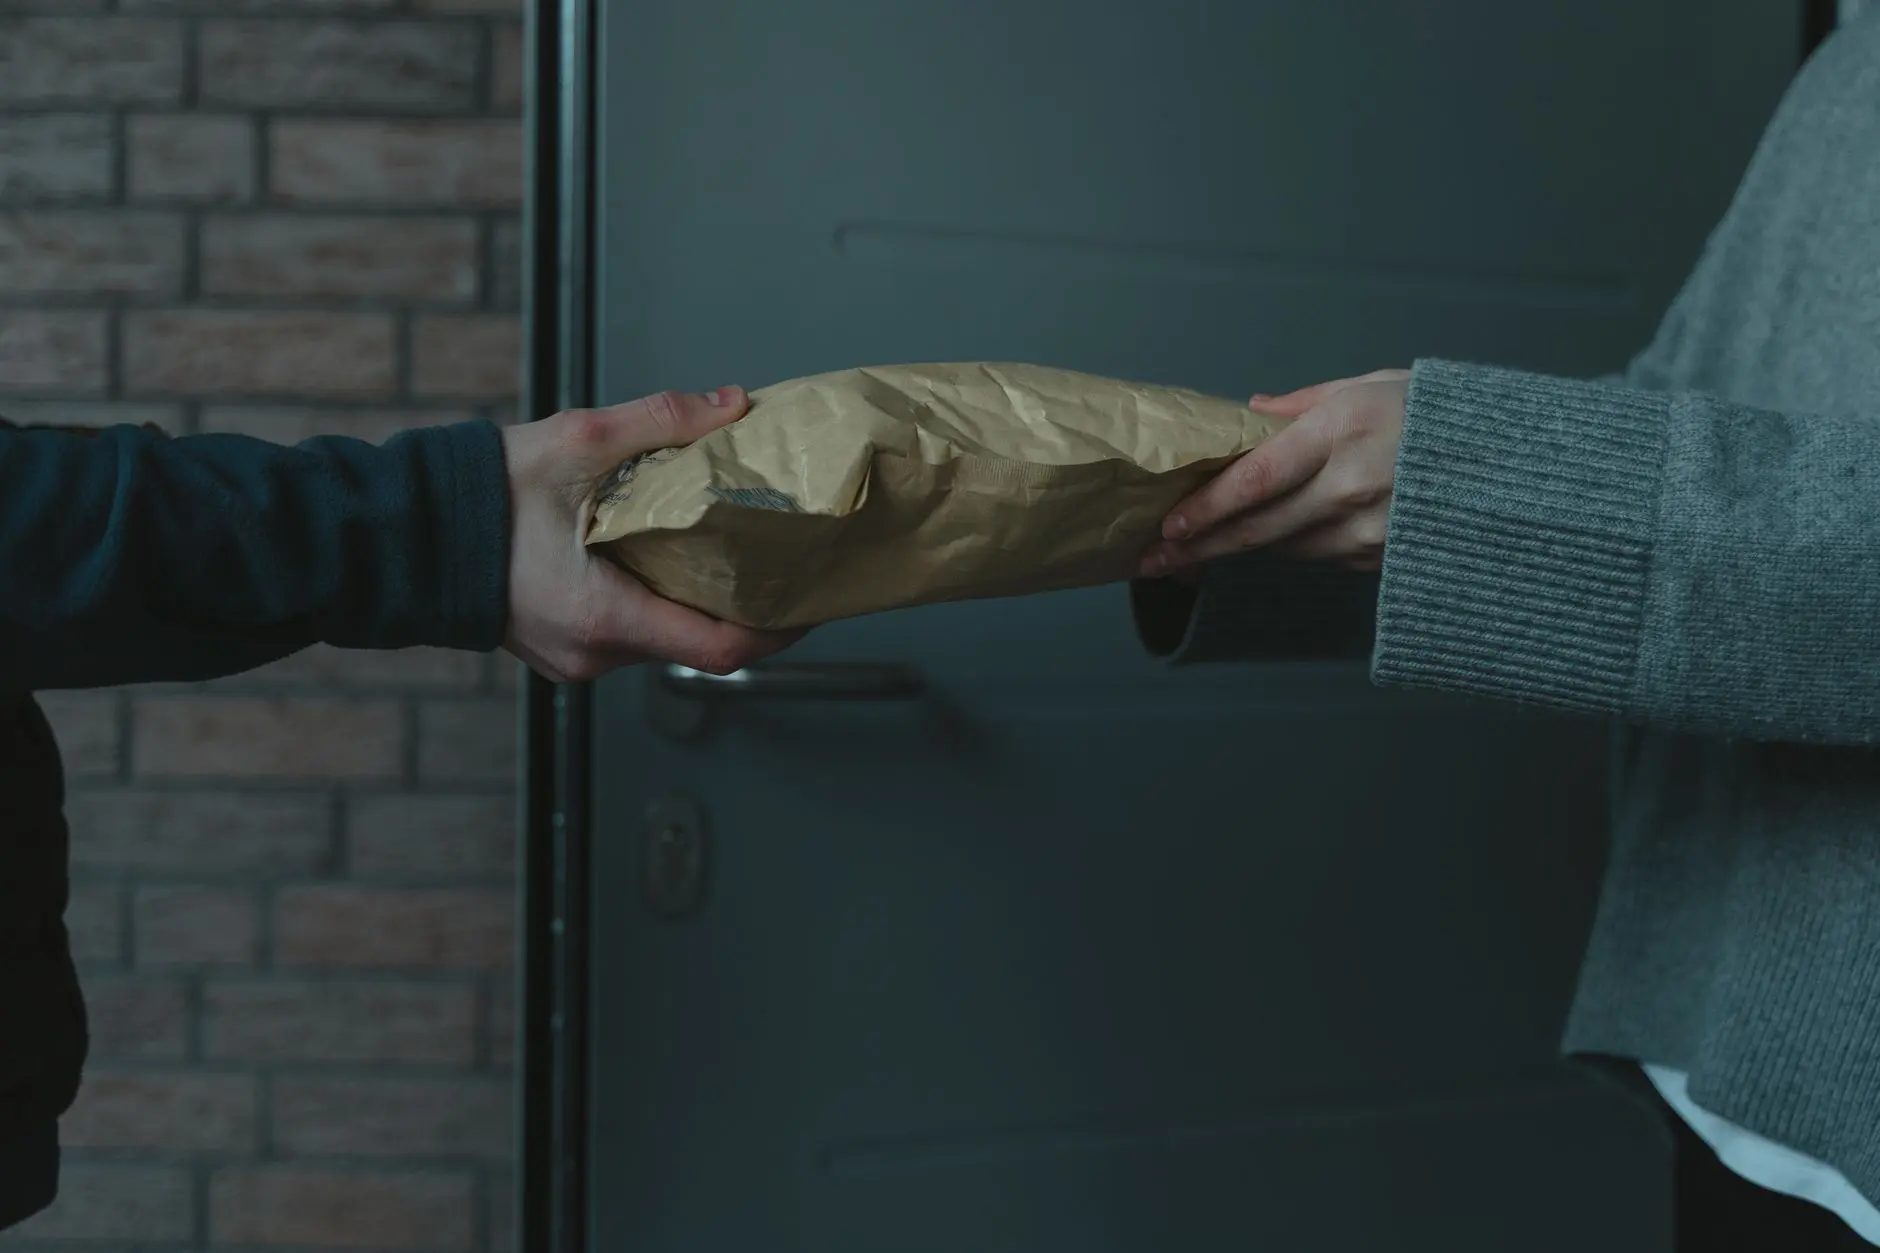
When a shopper on a Lagos-based Instagram boutique or a global Shopify store types their home address into a checkout field, they aren’t just providing a delivery location; they are handing over sensitive Personal Identifiable Information (PII). To avoid regulatory scrutiny, online stores need explain collecting this data with absolute clarity at the point of capture.
For many small to medium-sized e-commerce entrepreneurs, a physical address feels like a purely logistical detail. However, under modern data protection frameworks like the Nigeria Data Protection Act (NDPA) and the EU’s General Data Protection Regulation (GDPR), an address is a core piece of personal data that links a digital identity to a physical location. Collecting it without proper disclosure is not just a bad user experience; it is a compliance failure.
The Transparency Principle: Beyond the Privacy Policy
A common mistake made by digital founders is assuming that a long, dense Privacy Policy tucked away in the website footer is sufficient. Regulators are increasingly moving away from “hidden” disclosures toward “just-in-time” notices. This means that the moment a user is asked for their address, they should be informed about how that specific piece of data will be handled.
The principle of transparency requires that information be concise, transparent, intelligible, and easily accessible. If a customer provides their address to receive a package, they must be able to understand exactly who else will see that address, how long it will be stored, and whether it will be used for anything other than shipping.
Why Online Stores Need to Explain Collecting Addresses Effectively
There are three primary reasons why clarity is non-negotiable for e-commerce businesses:
- Purpose Limitation: You cannot collect an address for delivery and then secretly use it to build a physical mailing list for marketing without separate, explicit consent.
- Third-Party Risk: Most online stores use third-party logistics (3PL) providers, courier services, or delivery apps. The customer has a right to know that their data is being shared with these entities.
- Legal Basis: In many jurisdictions, the legal basis for processing an address is “contractual necessity” (you need the address to fulfill the order). However, if you use that address for profiling or location-based advertising, you may need a different legal basis, such as consent.
Four Essential Disclosures for E-commerce Checkouts
To build digital trust and ensure compliance, businesses should integrate the following explanations into their checkout flows or close to the address input field.
1. The Specific Purpose of Collection
Do not just say “we collect data to improve services.” Be specific. State that the address is collected for the purpose of order fulfillment, shipping, and communicating delivery updates.
2. Third-Party Sharing Disclosures
This is where most breaches of trust occur. If you use a local delivery partner in Nigeria or a global giant like DHL, your privacy notice should clarify that address data is shared with these service providers to complete the transaction. This falls under the umbrella of data protection obligations regarding data processors.
3. Data Retention Periods
How long do you keep the address? While you need it to ship the item, you should not keep it indefinitely. Explain that the data is retained for a specific period (e.g., seven years for tax and audit purposes) and then deleted or anonymized.
4. Data Subject Rights
Users must be reminded that they have the right to access, correct, or request the deletion of the information they have provided. Providing a direct way to exercise these rights increases your brand’s perceived trustworthiness.
Comparison: Vague vs. Transparent Disclosures
The following table illustrates the difference between non-compliant, vague language and the clear, transparent language required by modern regulators.
| Vague/Non-Compliant Language | Transparent/Compliant Language |
|---|---|
| “We collect your information to provide our services.” | “We collect your physical address to facilitate the delivery of your purchased items.” |
| “We may share data with our partners.” | “Your address will be shared with our courier partners (e.g., GIGL or DHL) solely for delivery purposes.” |
| “Your data is stored securely.” | “Your address is stored on encrypted servers for 5 years to comply with financial record-keeping laws.” |
Mini Case Study: The Lagos Skincare Brand Scenario
Consider a hypothetical skincare brand based in Lekki, Lagos, which operates via a mobile app. The brand collects customer addresses for deliveries. However, to save on costs, they shared their customer database—including names and addresses—with a third-party marketing agency to help them find new customers through physical flyer distribution. They did not inform customers that their addresses would be used for marketing via physical mail.
Under the NDPA, this is a violation of the purpose limitation principle. The customers provided their data for fulfillment, not marketing. Had a customer complained to the Nigeria Data Protection Commission (NDPC), the brand could have faced significant fines and a devastating loss of reputation. The lesson is clear: what you collect must match what you explain.
“Transparency is not a checkbox; it is the foundation of the digital relationship between a brand and its customer. When customers feel in control of their data, they are more likely to remain loyal.” — Privacy Compliance Expert
Action Checklist for Business Leaders
If you are a founder or a technology lead, use this checklist to audit your current checkout process:
- Audit your data flow: Map out exactly where a customer’s address goes once they click “Submit.” (Is it going to your server? To a CRM? To a courier?)
- Review your checkout UI: Is there a clear, short notice near the address field?
- Update your Privacy Policy: Ensure your written policy matches your actual technical practices.
- Train your team: Ensure your customer support and logistics teams understand that customer addresses are protected data, not just “delivery info.”
Frequently Asked Questions
Do I need separate consent for an address if it’s for delivery?
Usually, no. Processing an address to deliver a product you have already sold is considered “contractual necessity.” You don’t need a separate checkbox for delivery, but you do need to inform the user that you are collecting it for that purpose.
Is an IP address considered a physical address?
No, but they are related. An IP address is a digital identifier, while a physical address is a geographic one. However, both are considered personal data under most modern laws.
Conclusion
As e-commerce continues to dominate the global economy, the scrutiny on how consumer data is handled will only intensify. For businesses, the goal should not be to do the bare minimum to avoid a fine, but to build a culture of transparency. By ensuring that online stores need explain collecting customer addresses clearly and honestly, companies can turn compliance from a legal burden into a competitive advantage of digital trust.












Leave a Reply