



What e commerce Know NDPA and Data Privacy

Share
Understanding the NDPA Landscape for Modern Retail
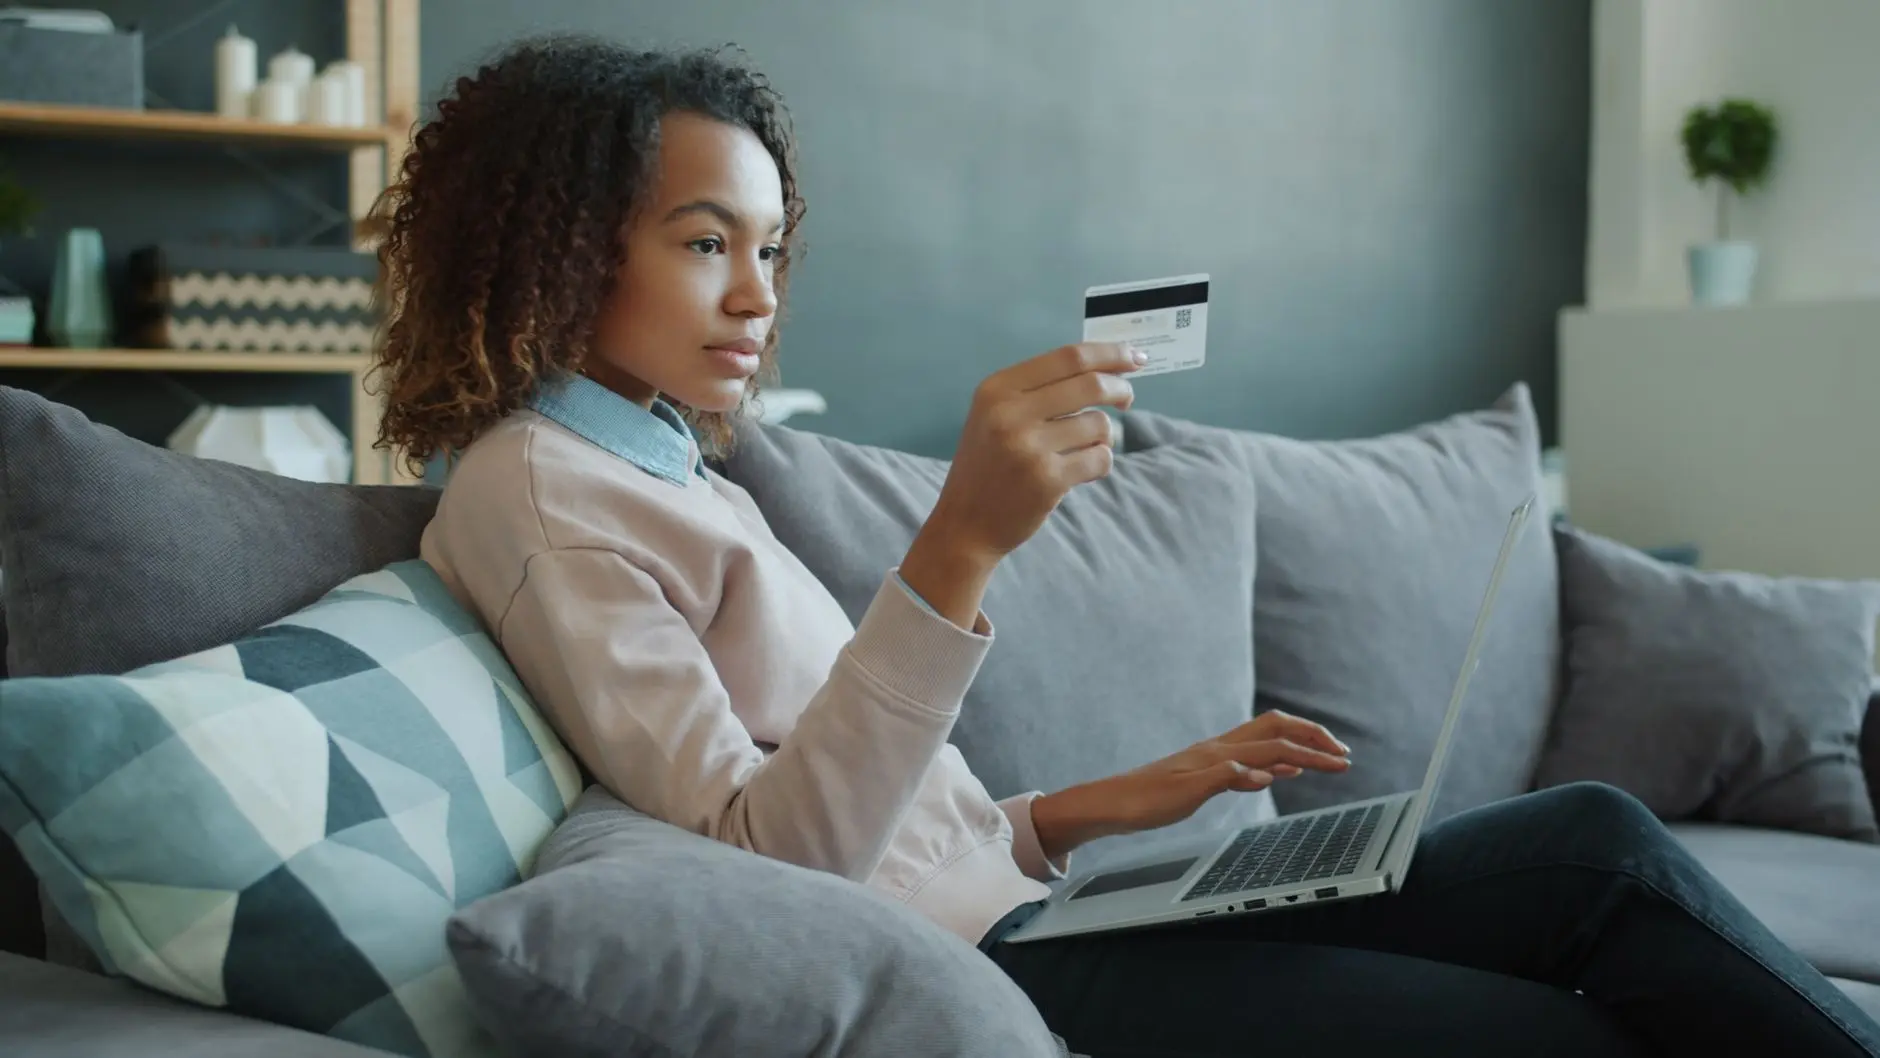
Online retail platforms handle immense volumes of sensitive consumer information every single minute. From names and delivery addresses to payment card details and browsing history, digital storefronts operate on a foundation of personal data. For online retailers expanding or operating within dynamic African markets, understanding regulatory frameworks like the Nigeria Data Protection Act (NDPA) is no longer optional. Business leaders must e commerce Know NDPA mandates thoroughly to avoid severe regulatory penalties and maintain consumer confidence.
Enforced by the Nigeria Data Protection Commission (NDPC), the NDPA establishes a robust legal framework for safeguarding personal data. Unlike localized privacy laws of the past, this legislation applies extraterritorially if an organization processes the data of individuals residing in Nigeria, regardless of where the business entity is physically domiciled. For an online store based in London, Nairobi, or Lagos, shipping products to regional buyers brings immediate compliance obligations.
Core Compliance Obligations for Online Retailers
Operating an online store requires strict adherence to data processing principles. Under the NDPA, customer data must be collected for explicit, lawful purposes and processed transparently. Retailers cannot quietly harvest customer emails for aggressive third-party marketing without obtaining explicit consent.
To build a resilient privacy posture, organizations must implement robust technical and organizational measures. This includes encrypting transit data, securing payment gateways, and conducting regular vulnerability assessments. Compliance teams must also establish clear protocols for managing data subject rights, such as allowing customers to access, correct, or delete their stored personal records.
Key Data Protection Responsibilities
- Lawful Basis: Ensure every piece of collected data has a valid legal basis, such as contract fulfillment or explicit consent.
- Transparency: Maintain an easily accessible, plain-language privacy policy detailing how consumer data is utilized.
- Security Measures: Deploy end-to-end encryption and multi-factor authentication across all administrative systems.
- Breach Notification: Prepare incident response plans to notify regulators and affected individuals swiftly during security incidents.
Real-World Risk: The Cost of Ignoring Data Privacy
Consider a growing online fashion retailer that stores customer profiles, purchase history, and credit card tokens insecurely on a cloud server. If an unauthorized actor exploits a misconfigured API, thousands of customer records could leak onto underground forums. Under the NDPA, regulatory fines can scale drastically based on the severity of the violation and annual turnover.
Beyond financial penalties, the reputational damage is often fatal for digital brands. Modern consumers actively avoid platforms that experience preventable data breaches. As noted by privacy experts, digital trust is the currency of the modern web. When a business fails to protect consumer data, customers leave for more secure competitors.
NDPA Versus Traditional E-Commerce Practices
Many traditional retail practices conflict directly with modern data protection standards. Review how modern requirements contrast with legacy habits:
| Traditional E-Commerce Practice | NDPA Compliant Standard |
|---|---|
| Pre-checked marketing subscription boxes | Unchecked, active, and granular opt-in consent |
| Indefinite customer data retention | Defined retention periods with automatic data purging |
| Sharing customer lists with affiliate partners | Strict third-party vetting and explicit user notification |
| Unencrypted customer support chat logs | Secure, encrypted communications and role-based access |
Actionable Steps for Compliance Teams
Founders and compliance officers should not wait for an audit to evaluate their data workflows. Start by mapping out every data touchpoint on your website. Where do you collect emails? How are guest checkouts handled? Do third-party analytics scripts track user sessions without consent?
Next, audit your vendor relationships. Payment processors, hosting providers, and customer relationship management (CRM) software vendors are often classified as data processors under the law. Ensure you have signed Data Processing Agreements (DPAs) in place with every external partner.
For broader compliance frameworks and regulatory guidance, review our detailed guides on data compliance strategies to align your business operations with international standards.
Frequently Asked Questions
Does the NDPA apply to small online shops?
Yes. While compliance tiers and audit requirements may vary based on the volume of data processed and organization size, the fundamental principles of lawful processing and consumer rights apply to businesses of all sizes.
What happens if an e-commerce store suffers a data breach?
Organizations must notify the NDPC within statutory timeframes, assess the risk to data subjects, and potentially notify affected customers if their rights and freedoms are placed at high risk.
Can customers request the complete deletion of their account history?
Under data subject rights provisions, individuals can request data erasure, provided there is no overriding legal obligation or active contract requiring the business to retain the information.
Conclusion
Navigating the intersection of retail technology and legal obligations requires continuous vigilance. To thrive in the digital economy, store owners must ensure they e commerce Know NDPA rules inside and out. By embedding privacy-by-design principles into your web architecture, training customer service teams, and respecting user consent, you protect your bottom line while fostering lasting consumer loyalty.












Leave a Reply