Bitget Loses $351.6M to Suspected North Korean Backend Attack

Share
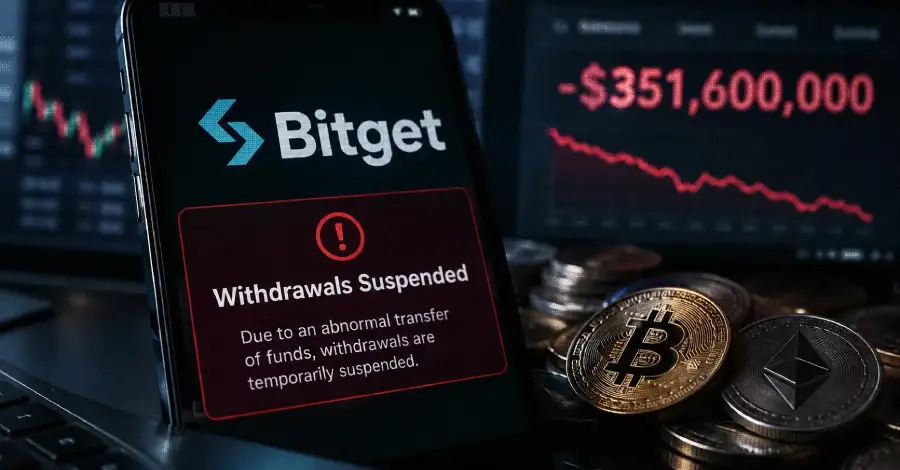
Bitget, a prominent cryptocurrency exchange, has reported the theft of $351.6 million following a breach of its backend wallet infrastructure. The company suspects the incident was carried out by North Korean threat actors.
The unauthorised transfers were identified by Bitget’s security systems at 18:31 UTC on 24 September 2026. The intrusion targeted a limited number of the exchange’s hot and warm wallets.
Backend system compromise used to spoof transactions
Bitget CEO Gracy Chen stated that the attackers compromised a critical backend system within the platform’s wallet infrastructure. By doing so, the threat actors were able to spoof transaction data, which in turn triggered the exchange’s internal authorisation process to move funds out of the platform.
Chen noted that the attack method and associated IP behaviour patterns are highly consistent with the known tactics of North Korean hacker organisations. The stolen assets include ETH, XRP, BNB, AVAX, USDT, and USDC, spanning multiple blockchain networks including Ethereum, Arbitrum, Avalanche, Optimism, BSC, Base, and the XRP Ledger.
Withdrawals suspended during security review
While Bitget confirmed that customer account balances remain accurate and that deposits and trading continue to operate normally, the exchange has temporarily suspended all withdrawals. This suspension is intended as a precautionary measure while a comprehensive security review is conducted.
The exchange emphasised that its cold wallets and the vast majority of platform assets remain secure and unaffected. Additionally, Bitget noted that its self-custodial Bitget Wallet operates on a separate, independent infrastructure and was not impacted by the breach.
Bitget has enlisted cybersecurity firms Mandiant and SlowMist to lead a third-party investigation into the incident. The company has also coordinated with the foundations of the affected blockchain networks, some of which have already confirmed the freezing of the attackers’ wallet addresses.
This incident follows recent reports of North Korea-linked activity, including attacks attributed to the TraderTraitor group. That group was recently linked to a large-scale theft from Bybit and a significant attack targeting an Indian information technology services firm.