



What insurance companies Should Know About NDPA and Data Privacy

Share
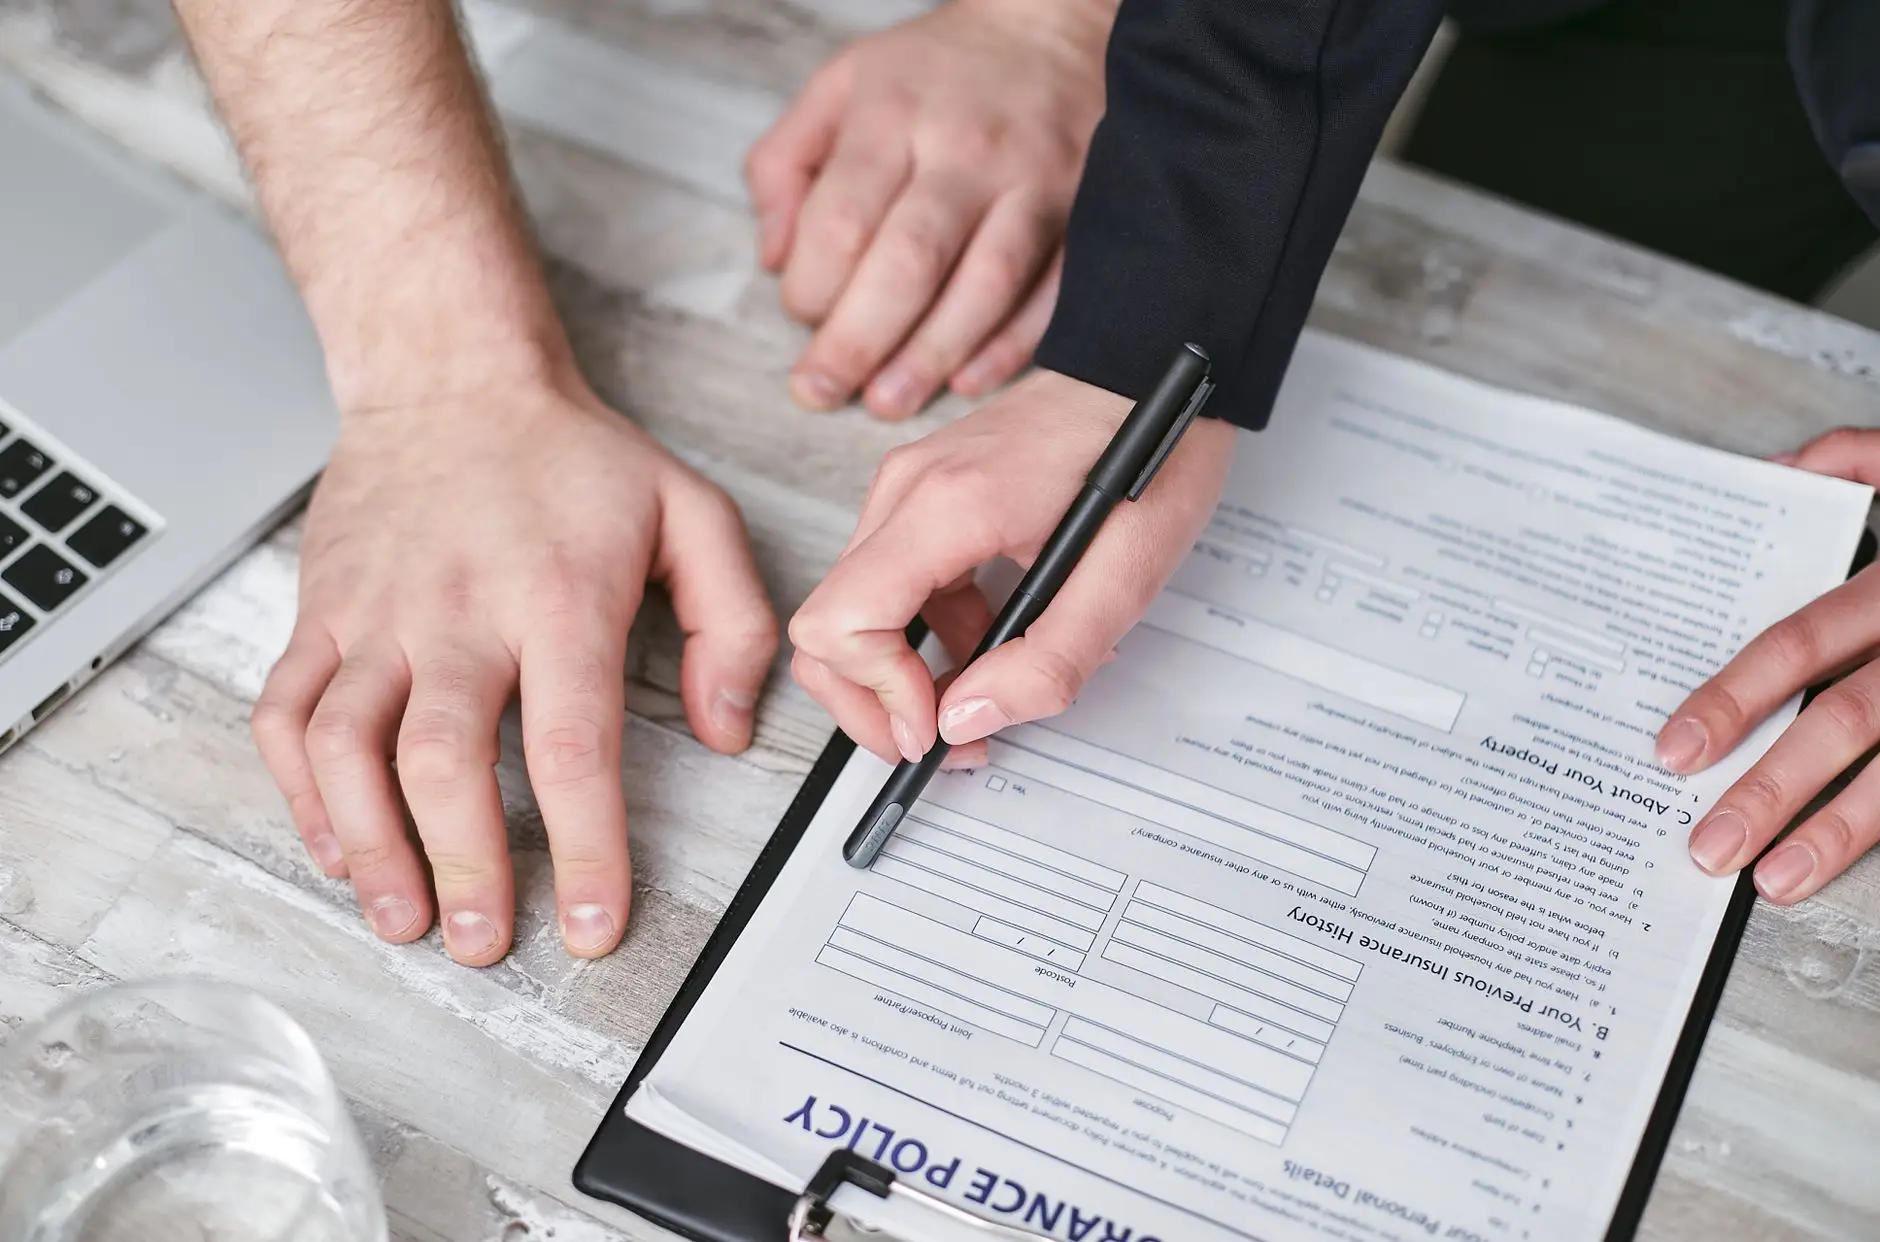
Insurance companies operate by collecting, analyzing, and storing massive volumes of sensitive personal and financial data. From medical records in health insurance underwriting to detailed asset valuations in property insurance, carriers handle some of the most private consumer information in existence. For insurers expanding or operating within jurisdictions governed by modern data privacy frameworks, understanding local legislation is no longer optional. When looking at emerging regulatory standards, it is vital that insurance Know NDPA mandates inside and out to avoid severe financial penalties and reputational damage.
The Nigeria Data Protection Act (NDPA) establishes a rigorous legal framework for how organizations handle personal identifiable information. Regulated by the Nigeria Data Protection Commission (NDPC), the law applies to any entity processing personal data of data subjects residing in Nigeria. Because insurance workflows inherently involve profiling, automated decision-making, and extensive background checks, insurance institutions face unique regulatory exposures under this legislation.
The Intersection of Insurance Underwriting and NDPA Mandates
Insurance underwriting relies heavily on data aggregation. Risk assessment algorithms evaluate lifestyle choices, medical histories, claims records, and financial standing. Under the NDPA, this data processing must adhere to strict principles of lawfulness, fairness, and transparency. Insurers can no longer collect sweeping categories of personal data without explicit, informed consent or a valid lawful basis recognized by the Nigeria Data Protection Commission.
Furthermore, policyholders retain enforceable data protection rights, including the right to access their data, object to automated profiling, and request the correction of inaccurate risk profiles. If an insurance algorithm incorrectly denies coverage based on flawed or poorly processed data, the carrier may face both regulatory scrutiny and civil litigation.
Key Compliance Obligations for Insurers
Insurance companies must implement comprehensive technical and organizational measures to secure consumer data throughout its lifecycle. This requires a shift from reactive security to proactive compliance frameworks. Here are the core areas insurance executives must prioritize:
- Data Minimization: Collecting only the data strictly necessary for underwriting or claims processing.
- Privacy Impact Assessments (PIAs): Conducting mandatory assessments before deploying new insurance tech platforms or automated pricing models.
- Vendor Risk Management: Ensuring third-party claims adjusters, medical examiners, and cloud storage providers maintain equal data security standards.
- Breach Notification Protocols: Establishing rapid incident response plans to notify the NDPC and affected data subjects within statutory timelines if a data breach occurs.
Risk Comparison: Traditional Insurance Operations vs. NDPA Standards
| Operational Area | Traditional Approach | NDPA Compliant Approach |
|---|---|---|
| Data Collection | Gathering broad data “just in case” | Targeted collection tied to specific policy needs |
| Consent Management | Buried inside dense terms of service | Granular, explicit, and easily revocable consent |
| Data Retention | Indefinite storage of old claims files | Defined retention schedules with secure deletion |
| Algorithmic Decisions | Opaque “black box” risk scoring | Transparent logic with human review options |
Real-Life Scenario: The Cost of Non-Compliance
Consider a mid-sized health insurance provider that experienced a cloud misconfiguration, exposing the medical histories and national identification numbers of fifty thousand policyholders. Under the NDPA, the regulatory fallout extends far beyond public relations damage. The NDPC has the authority to investigate the incident, audit internal security controls, and levy substantial administrative fines for failing to implement adequate security safeguards.
Beyond regulatory fines, policyholders affected by the exposure can file private lawsuits for distress and damages. This scenario highlights why every board member and risk officer must ensure their organization understands how insurance Know NDPA requirements shape modern accountability.
Actionable Steps for Insurance Compliance Teams
To align with the NDPA, compliance departments within insurance firms should execute a structured readiness plan:
- Audit Data Flows: Map every entry point where customer data enters the enterprise, tracking how it moves between brokers, underwriters, and reinsurers.
- Update Privacy Notices: Rewrite customer-facing policy documents in plain, accessible language explaining how their data is used in risk calculations.
- Train Frontline Staff: Educate customer service agents and sales representatives on handling data subject access requests securely.
- Appoint a Data Protection Officer: Designate a qualified DPO to oversee ongoing compliance and act as the primary liaison with regulatory authorities.
Frequently Asked Questions
Does the NDPA apply to foreign insurance companies operating remotely?
Yes. If a foreign insurer targets individuals residing in Nigeria or monitors their behavior within the country, the NDPA applies extraterritorially.
What are the penalties for non-compliance under the NDPA?
Penalties can include severe financial fines, corrective orders, public reprimands, and potential liability for civil damages paid to affected data subjects.
How often should insurance companies review their data processing practices?
Insurers should conduct annual data protection audits and immediate reviews whenever introducing new digital products or underwriting algorithms.
Conclusion
Data privacy is no longer a peripheral legal matter for financial institutions; it sits at the core of consumer trust and operational legitimacy. As regulatory oversight intensifies across global markets, ensuring insurance Know NDPA obligations safeguards both the enterprise and its policyholders. By embracing transparent data practices, robust security controls, and proactive compliance frameworks, insurance companies can turn regulatory mandates into a powerful competitive advantage.










Leave a Reply