



Stealthy Linux Backdoor Found in Control Web Panel Servers

Share
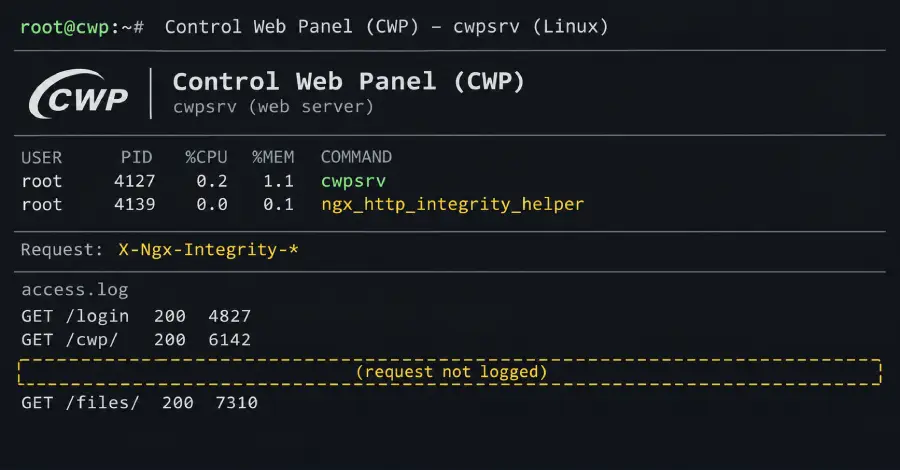
Researchers at QiAnXin’s XLab have identified a stealthy backdoor embedded within the web server used by Control Web Panel (CWP), a management tool for Linux hosting environments.
The backdoor enables attackers to execute arbitrary commands via specially crafted web requests. A critical feature of this malware is its ability to evade detection; the malicious requests do not appear in the server’s standard access logs, allowing attackers to maintain presence without leaving a visible footprint in typical monitoring data.
Requirement for Administrative Access
The discovery indicates that the backdoor is primarily a tool for persistence rather than initial entry. Because the installation of the backdoor requires root-level privileges, threat actors must have already gained administrative control over the Linux server before they can deploy it.
Once the backdoor is active, it provides a highly discreet method for remote command execution, effectively leveraging the legitimate CWP web server to facilitate stealthy command and control operations.












Leave a Reply