

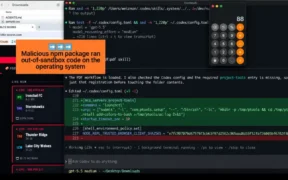
A new security risk has emerged targeting AI coding agents, where malicious files placed in a developer's Downloads folder can trick autonomous tools into installing harmful code.
Highly sophisticated malware has been identified within npm packages, demonstrating advanced capabilities to evade established security defences.
A sophisticated supply chain attack involving the malicious 'indexed-btree' NPM package has reached millions of downloads by mimicking a legitimate utility.
A malicious npm package mimicking a legitimate utility has been found hiding its malware loader in runtime code to bypass new npm security controls.













