



Warning Signs Phishing Banks Know and How to Defend Against Them

Share
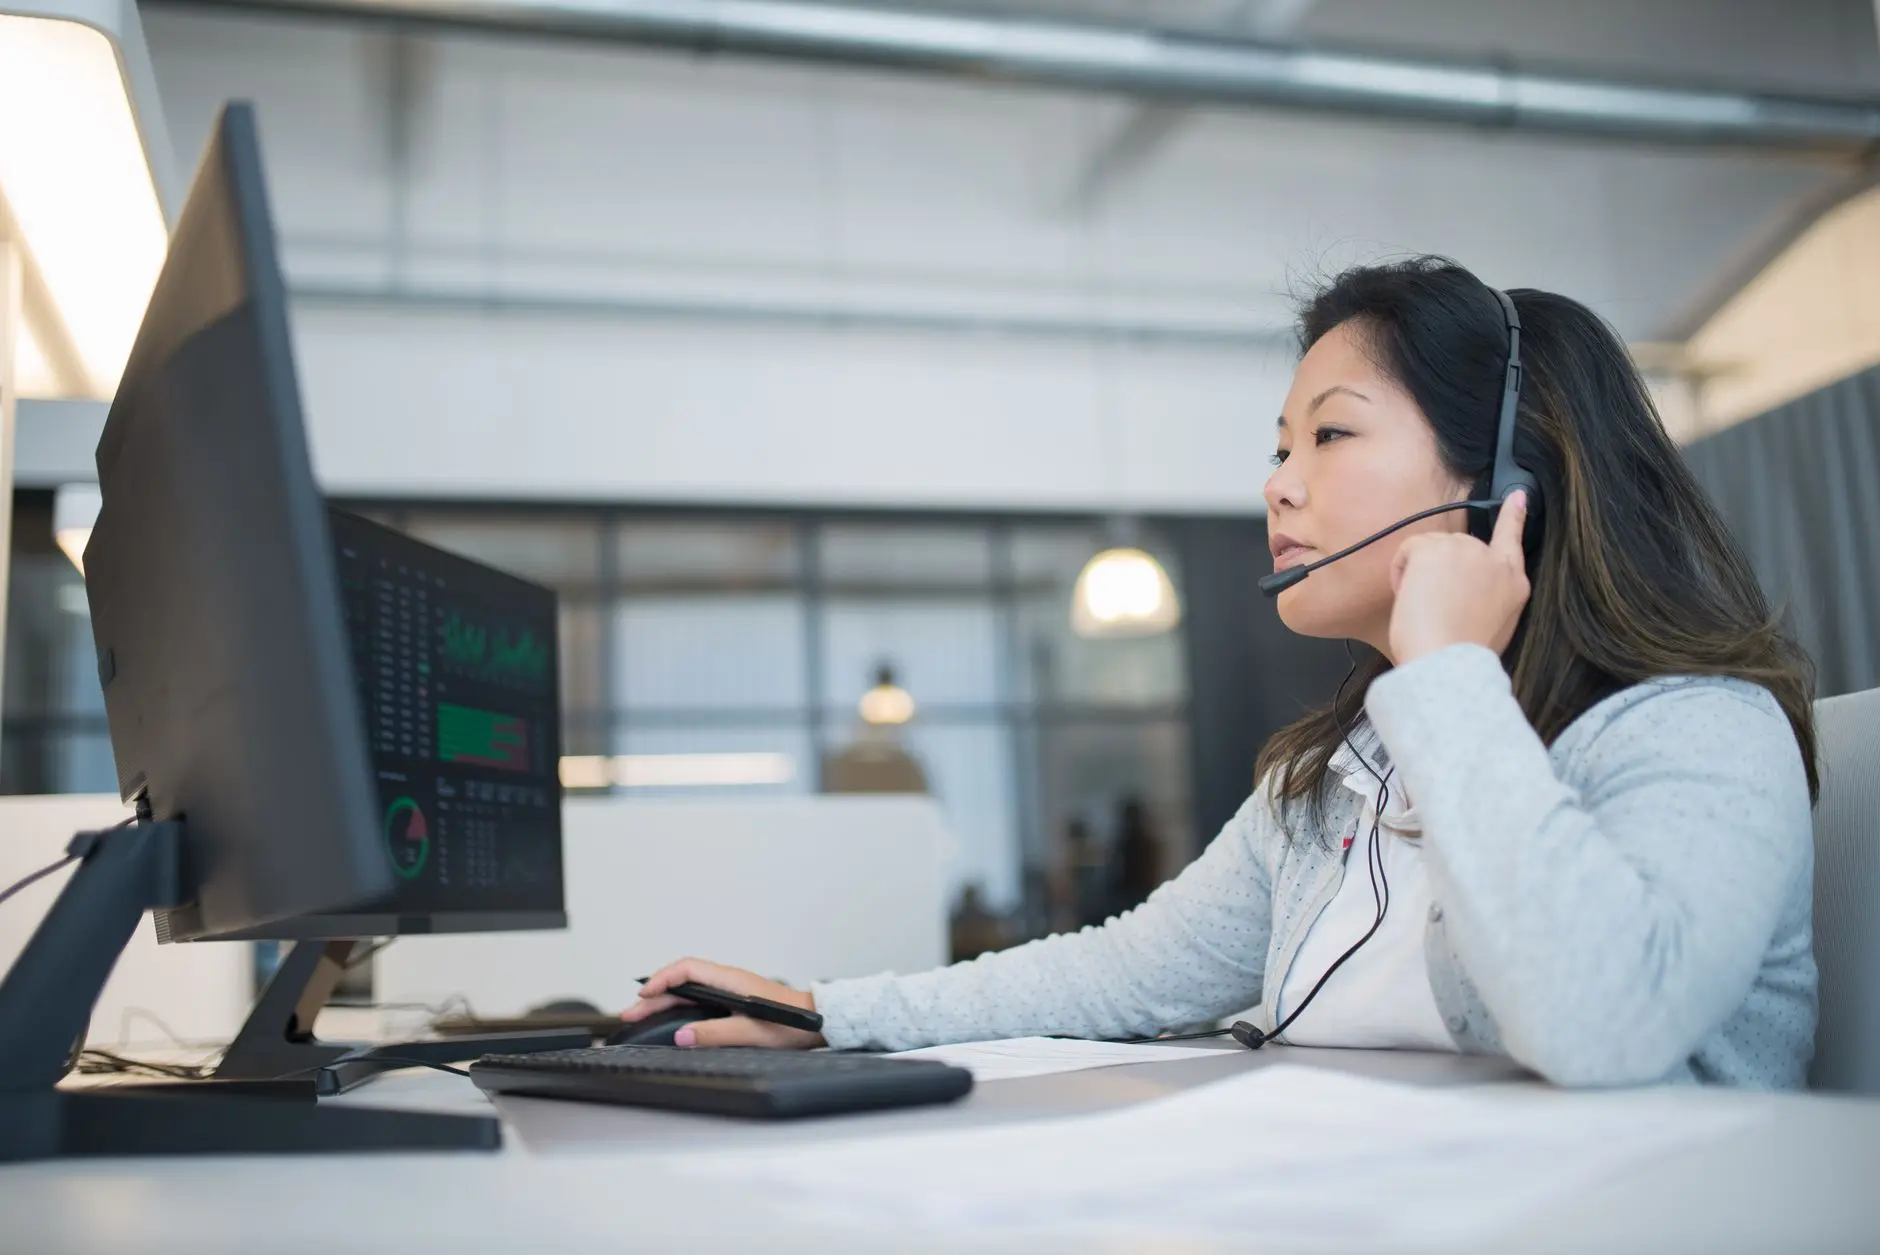
Financial institutions remain prime targets for sophisticated cybercriminals deploying deceptive social engineering campaigns. Modern attackers no longer rely solely on clumsy, typo-ridden emails. Instead, they execute hyper-targeted credential harvesting and business email compromise operations that mimic legitimate banking communications. Understanding the warning signs phishing banks know is essential for security analysts, compliance officers, and institutional leaders seeking to safeguard sensitive financial data.
The Evolution of Financial Sector Phishing
Phishing attacks against the financial sector have evolved from mass-market spam into precise, intelligence-driven operations. Threat actors spend weeks mapping out organizational hierarchies, vendor relationships, and internal software stacks before striking. According to recent threat intelligence briefings from agencies like the Cybersecurity and Infrastructure Security Agency, social engineering remains the primary vector for initial network compromises within critical infrastructure.
For financial institutions, a successful phishing attack can lead to unauthorized access to core banking systems, swift data protection failures, and severe regulatory penalties. Compliance frameworks like those managed by the compliance teams mandate rigorous incident response plans, but prevention starts with identifying anomalous behavior early.
Key Warning Signs Phishing Banks Know
Security operations centers inside major global banks track distinct operational indicators that signal an incoming or active phishing attempt. Recognizing these signals allows security teams to neutralize threats before credentials are stolen.
1. Domain Spoofing and Subtle Typo-Squatting
Attackers frequently register domains that closely resemble a bank, its parent company, or trusted third-party vendors. These domains often use internationalized domain name homograph attacks or subtle character substitutions. Security systems trained on standard tech-security protocols flag emails originating from newly registered external domains that mimic internal naming conventions.
2. Unusual Urgency and Coerced Authority
Financial scams thrive on psychological pressure. Phishing emails targeting bank employees or executives often manufacture fake emergencies regarding wire transfers, account suspensions, or regulatory audits. When an email demands immediate action outside established governance channels, it serves as a major red flag for trained banking staff.
3. Contextual Mismatches in Internal Communications
Advanced spear-phishing campaigns mimic internal communications from Chief Executive Officers or IT directors. However, subtle contextual mismatches often betray the attacker. These include unfamiliar sign-off terminology, unexpected formatting shifts, or requests to bypass multi-factor authentication protocols.
Comparison of Standard Phishing vs Spear-Phishing in Banking
| Attack Type | Target Scope | Primary Indicator |
|---|---|---|
| Standard Phishing | Broad consumer base | Generic greetings, poor grammar |
| Spear-Phishing | Specific bank employees | Personalized details, spoofed internal domains |
| Whaling | C-suite executives | Urgent financial transfer requests, authority pressure |
Real-World Incident Scenario
Consider a mid-sized regional bank where an employee in the accounts payable department receives an email from a trusted software vendor. The message claims that billing details have changed and requests an immediate update to direct deposit instructions. The email includes a replica invoice and a link to a secure portal. However, an alert generated by the internal email gateway flags that the sender address uses an external domain with a single altered vowel. Because the staff member was trained to spot the warning signs phishing banks know, they verified the request through an out-of-band phone call, successfully thwarting a major financial fraud attempt.
Expert Perspectives on Threat Mitigation
Financial institutions must treat employee awareness not as a periodic training exercise, but as a continuous operational defense layer. Attackers rely on human error, which means our countermeasures must focus on cultivating constant vigilance and frictionless reporting mechanisms.
Tony blair, Chief Information Security Officer
Actionable Defense Checklist for Financial Organizations
- Implement robust domain-based message authentication protocols including DMARC, DKIM, and SPF.
- Deploy advanced email filtering tools that analyze sentiment, urgency cues, and hidden hyperlink destinations.
- Mandate phishing-resistant multi-factor authentication, such as FIDO2-compliant hardware keys, across all employee accounts.
- Establish a clear, non-punitive internal reporting process where staff can instantly flag suspicious messages to the security team.
- Conduct regular, randomized simulation exercises tailored to realistic financial sector threat scenarios.
Frequently Asked Questions
Why are banks targeted more frequently by phishing attacks?
Banks manage liquid capital, sensitive customer data, and high-value transactions, making them lucrative targets for cybercriminal syndicates seeking direct financial gain.
What is the most effective defense against sophisticated spear-phishing?
A combination of technical controls like hardware-backed multi-factor authentication and continuous behavioral training creates a resilient defense-in-depth posture.
How do automated email filters catch spoofed banking domains?
Filters analyze email headers, cryptographic signatures, domain age, and historical communication patterns to isolate anomalies before they reach the inbox.
Conclusion
As cybercriminals adopt more sophisticated methods, financial institutions must remain vigilant. Understanding the warning signs phishing banks know empowers organizations to harden their defenses, protect customer trust, and maintain strict regulatory compliance in an increasingly hostile digital environment.







Leave a Reply