



How Startups Build Design Their Products Early for Privacy

Share
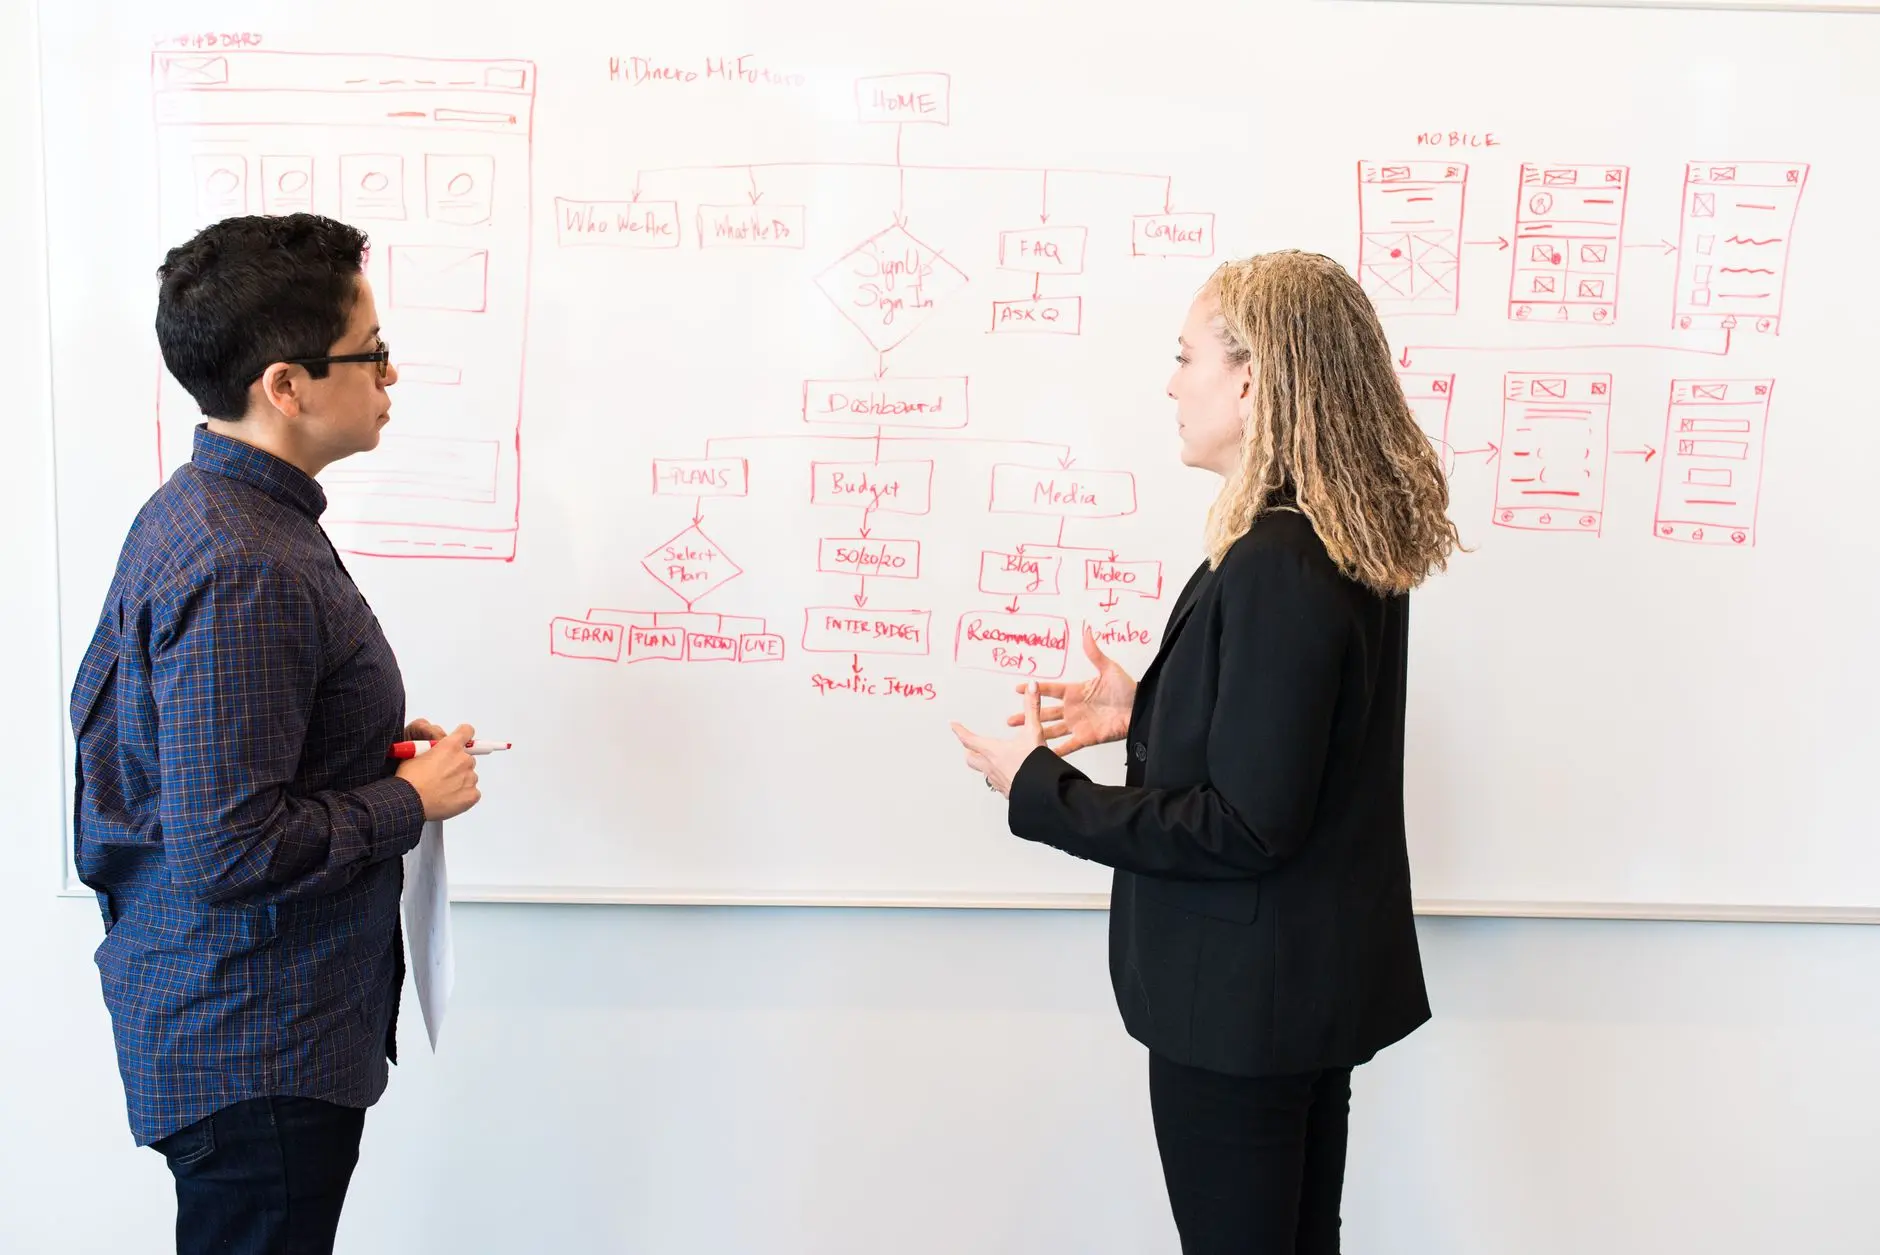
Startups prioritize velocity. Founders move fast to ship features, secure market validation, and acquire initial users. In this sprint toward product-market fit, privacy is frequently treated as an afterthought or a bureaucratic hurdle reserved for later funding rounds. This approach creates an invisible, compounding liability known as privacy debt. When startups treat user data as an unmanaged exhaust product rather than a protected asset, retrofitting software architectures later becomes financially and operationally devastating.
A proactive architectural approach changes the dynamic entirely. When startups build design their products early around data minimization, governance, and cryptographic protection, they protect user rights while establishing a competitive differentiator that accelerates enterprise sales and investor due diligence.
The True Cost of Retrofitting Privacy
Engineering teams understand the burden of technical debt: shortcutting code architecture today requires rewriting foundational systems tomorrow. Privacy debt operates identically, but carries severe legal liabilities. Rewriting an existing relational database schema to accommodate data residency, consent revocation, or automated retention policies takes months of engineering sprints that could otherwise go toward revenue-generating product improvements.
According to the Cisco Data Privacy Benchmark Study, 94 percent of organizations report that customers will not buy from them if their data protections are unclear or insufficient. Furthermore, the European Data Protection Board emphasizes in their Guidelines 4/2019 on Data Protection by Design and by Default that data protection principles must be embedded into the development lifecycle from the earliest stages of system architecture, rather than added as a superficial layer after release.
“Privacy by Design advances the view that the future of privacy cannot depend solely on compliance with regulatory frameworks; rather, privacy assurance must ideally become an organization’s default mode of operation.”
This observation from Dr. Ann Cavoukian, who established the seven foundational principles of Privacy by Design, highlights why startups must shift their mindset. Privacy is an engineering discipline, not a legal disclosure page.
Why Startups Build Design Their Products Early to Win Market Trust
In B2B SaaS and consumer tech alike, customers increasingly scrutinize data handling practices before signing contracts or granting platform permissions. Early architectural discipline signals maturity to enterprise procurement teams who routinely reject vendors unable to demonstrate granular access controls or zero-knowledge storage configurations.
The table below contrasts the operational reality of building privacy early versus attempting to patch legacy systems after launch:
| Operational Dimension | Privacy-by-Design from Inception | Retrofitting Privacy Post-Launch |
|---|---|---|
| Database Architecture | Normalized, segmented personal data with pseudonymization | Monolithic tables mixing identifiers with operational logs |
| Engineering Overhead | Low, predictable incremental cost per sprint | Massive code freezes and painful database migrations |
| Subject Access Requests (SARs) | Automated querying and export mechanisms | Manual database scripts requiring senior developer time |
| Sales Cycle Velocity | Fast security review approvals for enterprise pilots | Protracted redlining and lost enterprise contracts |
| Regulatory Exposure | Documented risk assessments and data minimization | Heightened vulnerability to statutory fines and enforcement |
A Practical Scenario: The Tale of Two Early-Stage Fintechs
Consider two early-stage financial analytics platforms, Startup Alpha and Startup Beta. Both launched with three engineers building an aggregation engine for personal investment portfolios.
Startup Alpha opted for raw speed. They routed user banking credentials, full names, and account balances directly through unencrypted background queues into a centralized PostgreSQL instance. Application logs routinely recorded raw payload details to assist with quick debugging. Within eighteen months, Alpha reached twenty thousand users and prepared for an enterprise partnership with a regional bank. During technical diligence, the bank’s security auditor discovered that Alpha stored unencrypted personal identifiers in cloud backups and third-party observability dashboards. The partnership collapsed, and Alpha spent four months in complete code refactoring to sanitize their pipeline.
Startup Beta implemented structured data protection fundamentals during sprint zero. They separated authentication identifiers from financial activity records using randomly generated pseudonymous UUIDs. They configured their API gateways to strip sensitive headers before routing logs to third-party monitoring vendors, and applied field-level encryption to sensitive financial tokens. While this framework required two additional days of initial architecture planning, Beta passed the exact same bank audit within forty-eight hours, closing a multi-year enterprise contract without writing a single line of remedial code.
The Core Engineering Blueprint for Early-Stage Products
Integrating privacy into modern agile product workflows does not require enterprise-scale legal budgets. Software teams can implement a reliable blueprint through four concrete technical practices:
1. Enforce Aggressive Data Minimization
Every field stored in your database represents a liability. Before adding a field to an entity model, engineers should ask a fundamental question: Is this data strictly necessary to deliver the immediate user value? If an analytics tool only requires aggregate metrics, never store personal email addresses or IP addresses alongside the interaction logs.
2. Implement Data Partitioning and Pseudonymization
Isolate personally identifiable information (PII) from transactional and operational data. By storing direct identifiers (such as names, phone numbers, and physical addresses) in an encrypted, access-restricted datastore separate from the core application data, startups drastically limit attack surfaces. The application interacts solely with pseudonymous tokens, mitigating the blast radius if an individual service is compromised.
3. Establish Automated Retention from Day One
Startups often stockpile historical data indefinitely under the mistaken assumption that it will prove useful for future machine learning models. Unused data accumulates storage costs, creates regulatory exposure under global privacy statutes, and expands breach vulnerability. Implement automated time-to-live (TTL) policies on database records, temporary cache stores, and staging environments to purge discarded data automatically.
4. Audit Third-Party SDKs and SaaS Integrations
A software product is only as private as its external dependencies. Integrating marketing pixels, session replay scripts, or external analytics SDKs often inadvertently broadcasts private user actions to outside platforms. Review every third-party script, configure strict Content Security Policies (CSPs), and maintain clear internal documentation on external data flows to satisfy ongoing compliance requirements.
Fortifying Your Infrastructure Layer
Robust software privacy depends fundamentally on underlying infrastructure security. Teams must enforce strict role-based access control (RBAC), multi-factor authentication, and end-to-end transport layer encryption across all microservices. Discover practical guidance on hardening your development stack by reviewing modern tech security architectures designed to protect modern cloud environments.
Frequently Asked Questions
When should an early-stage startup begin implementing privacy by design?
Privacy by design should begin during initial system architecture design, before writing the first production database migration. Establishing clean schemas and data boundaries at the outset requires negligible effort compared to restructuring a live production environment.
Does privacy by design slow down rapid product iteration?
No. When modular architecture, pseudonymization, and data isolation are baked into standard development templates, software teams ship new features faster because they work with clean, well-defined data models that do not carry hidden compliance risks.
Is privacy by design only relevant for European companies under GDPR?
No. Modern data protection principles are global standards, reflected across North American regulations, Asian data protection frameworks, and corporate procurement policies worldwide. Building with privacy by default ensures seamless international scalability.
Conclusion
The belief that early-stage ventures must choose between development speed and user privacy is a false dichotomy. Data protection is not an impediment to innovation; it is a foundational pillar of modern software engineering. By ensuring that startups build design their products early around accountability, transparency, and data minimization, founders eliminate compounding technical liabilities, protect their users, and establish the enduring digital trust required to dominate their markets.









Leave a Reply