



Useful Privacy Policy Templates for Banks and Financial Institutions

Share
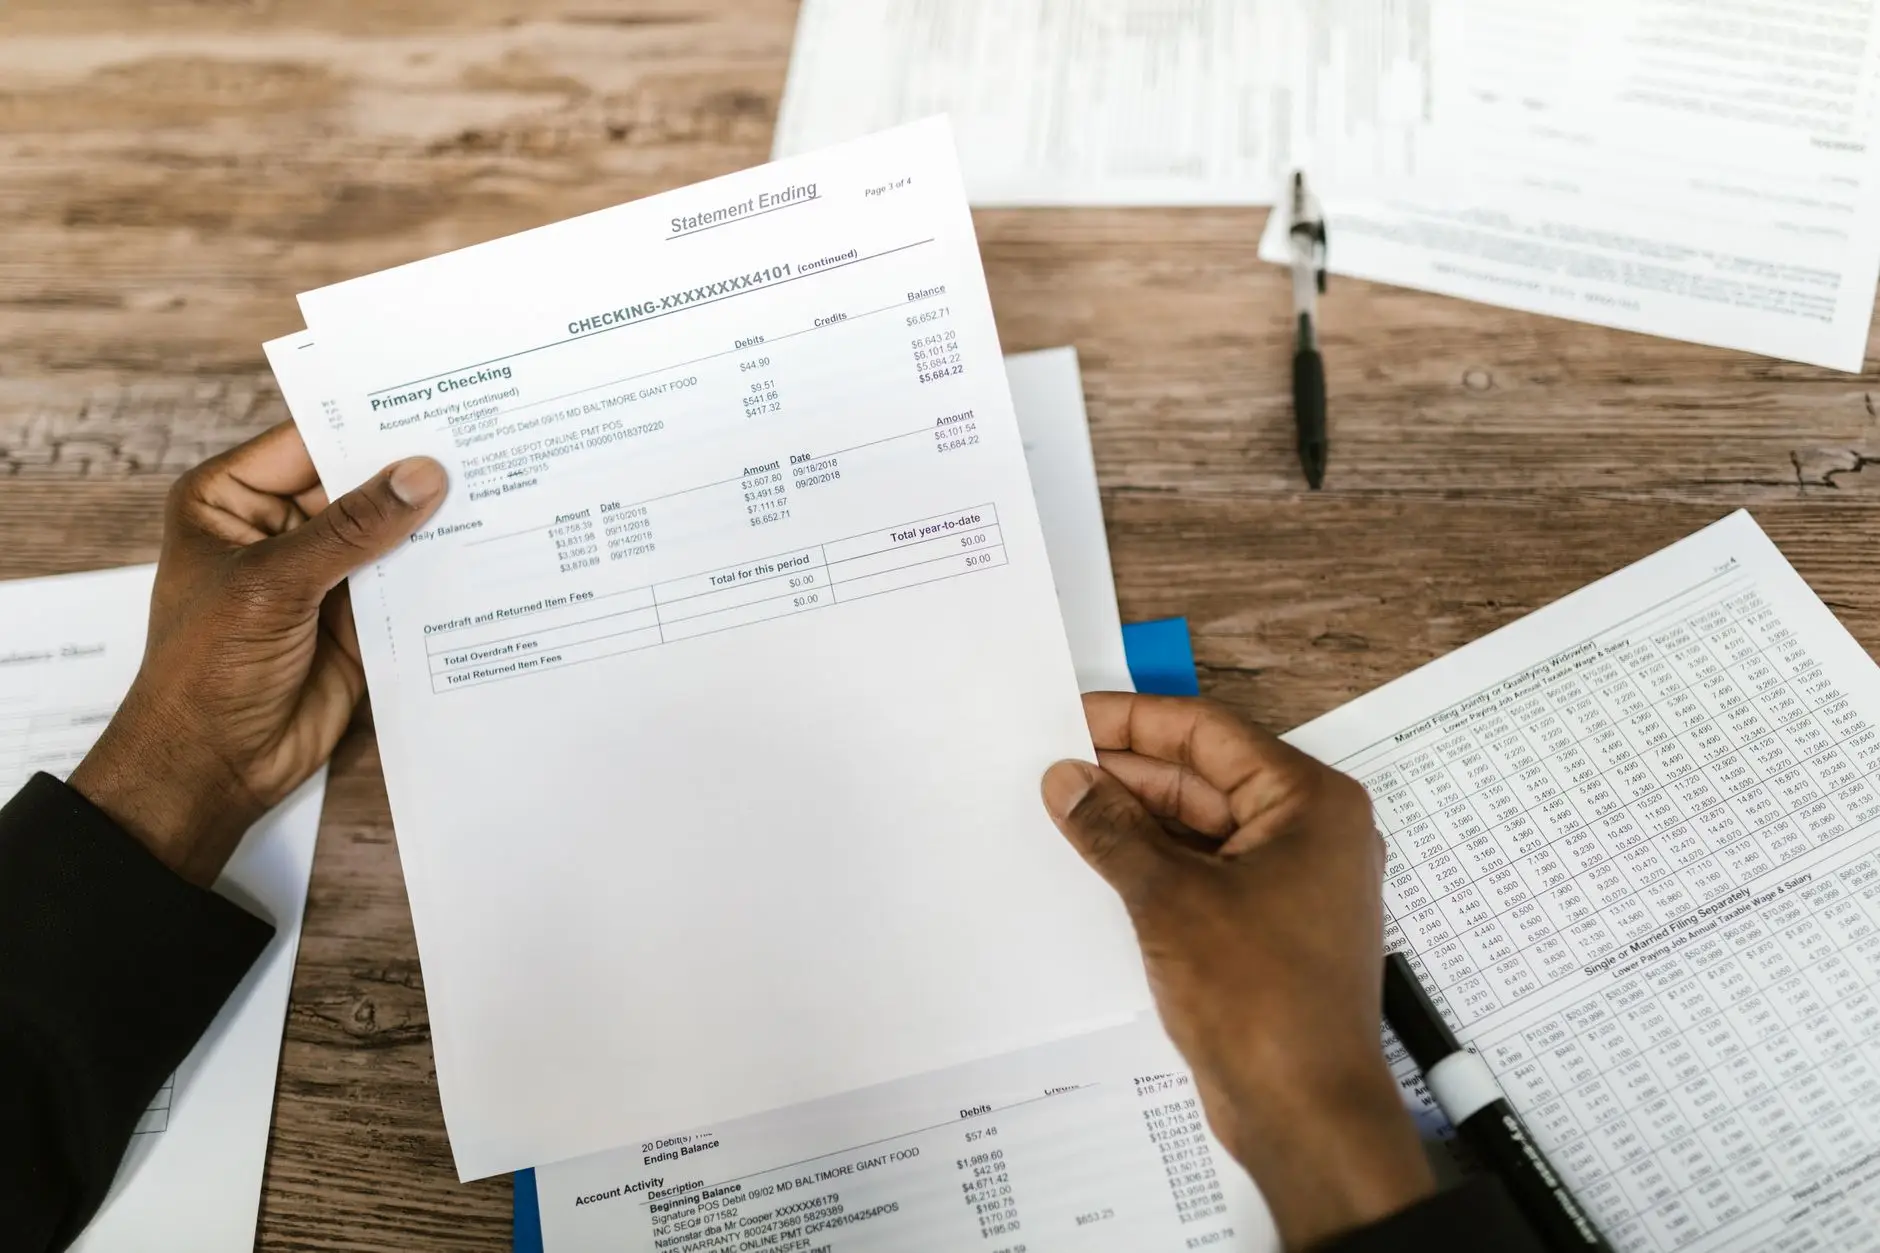
Financial institutions handle vast amounts of sensitive consumer data every second, ranging from social security numbers and transaction histories to credit scores and investment portfolios. Drafting a clear, legally sound privacy notice is not just a regulatory checkbox; it is the cornerstone of consumer trust. When building or updating a financial platform, legal and compliance teams frequently search for Useful Policy Templates banks can adapt to meet complex regional mandates like the Gramm-Leach-Bliley Act (GLBA), GDPR, and local compliance frameworks.
A poorly constructed notice can lead to severe regulatory penalties, consumer backlash, and reputational damage. This guide examines essential structural elements, provides practical drafting tips, and outlines why generic web templates fail in the highly regulated banking sector.
The Regulatory Burden on Modern Financial Institutions
Banks operate under stringent regulatory scrutiny. Unlike e-commerce platforms or lifestyle blogs, financial organizations must account for specific statutory requirements regarding how they collect, share, and protect consumer financial information. Regulators across jurisdictions expect transparency, meaning disclosures must be written in plain language rather than dense legalese.
According to Federal Trade Commission guidelines, consumer notices must clearly explain what data is collected, why it is gathered, with whom it is shared, and how individuals can exercise their data protection rights. Failing to outline third-party data sharing practices transparently often triggers costly enforcement actions.
Key Components Required in Bank Privacy Policies
When selecting and customizing policy templates, compliance officers must ensure the document covers specific operational realities unique to banking operations. Below is a breakdown of critical sections that must be included in any institutional privacy notice.
- Data Collection Scope: Clear categorization of personal, financial, biometric, and technical data gathered through mobile apps, websites, and branch visits.
- Sharing and Disclosure Practices: Explicit details regarding sharing with affiliates, credit bureaus, marketing partners, and law enforcement agencies.
- Opt-Out Rights: Instructions on how customers can limit the sharing of their personal information with non-affiliated third parties.
- Security Safeguards: A summary of administrative, technical, and physical safeguards used to protect accounts from unauthorized access.
- Consumer Rights & Contact Information: Direct channels for customers to request access, correction, or deletion of their records.
Comparison of Privacy Policy Approaches
| Approach | Pros | Cons |
|---|---|---|
| Generic Web Templates | Quick and inexpensive to deploy | Misses vital banking regulations and exposes institution to fines |
| Custom Legal Drafting | Tailored precisely to institutional risk profile | High cost and time-intensive development cycle |
| Regulator-Provided Model Forms | High compliance certainty under specific laws like GLBA | Rigid formatting limits brand customization and clarity |
Real-Life Scenario: The Cost of Ambiguity
Consider a mid-sized regional bank that recently launched a mobile budgeting app. The legal team relied on a standard e-commerce privacy template found online, failing to include specific disclosures regarding automated credit scoring and third-party analytics trackers embedded in the software. Within months of launch, privacy advocates and regulators flagged the application for collecting geolocation data without explicit opt-in consent. The resulting audit forced an immediate redesign of the app interface, expensive legal remediation, and public relations damage that eroded consumer confidence.
“Transparency is not merely about disclosing what you do with data; it is about giving individuals meaningful control over their digital footprint in a way they can actually understand.”
Global Privacy Compliance Director
Actionable Checklist for Compliance Teams
Before publishing or updating a financial privacy notice, compliance professionals should run through this practical checklist to ensure operational alignment:
- Audit all software development kits (SDKs) and tracking pixels currently active on banking portals to verify data collection matches policy statements.
- Ensure opt-out mechanisms for financial data sharing are easily accessible within online banking dashboards.
- Review third-party vendor contracts to confirm data processors adhere to the privacy standards promised to consumers.
- Test the readability of the notice using plain language standards to ensure ordinary customers can comprehend their rights.
- Establish a routine review schedule, updating the policy at least annually or whenever new digital banking services launch.
Frequently Asked Questions
Can banks use standard commercial privacy templates?
No. Standard commercial templates usually omit mandatory financial disclosures required by banking regulators, such as GLBA opt-in and opt-out provisions for sharing nonpublic personal information.
How often should a bank update its privacy policy?
Financial institutions should review and update their privacy notices annually, or immediately whenever introducing new data collection practices, AI-driven credit tools, or expanding into new jurisdictions.
Conclusion
Navigating regulatory requirements demands precision, accountability, and proactive planning. Utilizing structured guidance and well-designed resources helps compliance teams build robust documentation without starting from scratch. By treating the privacy notice as a living commitment to consumer protection rather than a static legal shield, financial institutions can foster enduring trust and maintain seamless compliance in an increasingly digital economy.










Leave a Reply