



Editorial: Why AI Regulation Can No Longer Be Treated as an IT Problem

Share
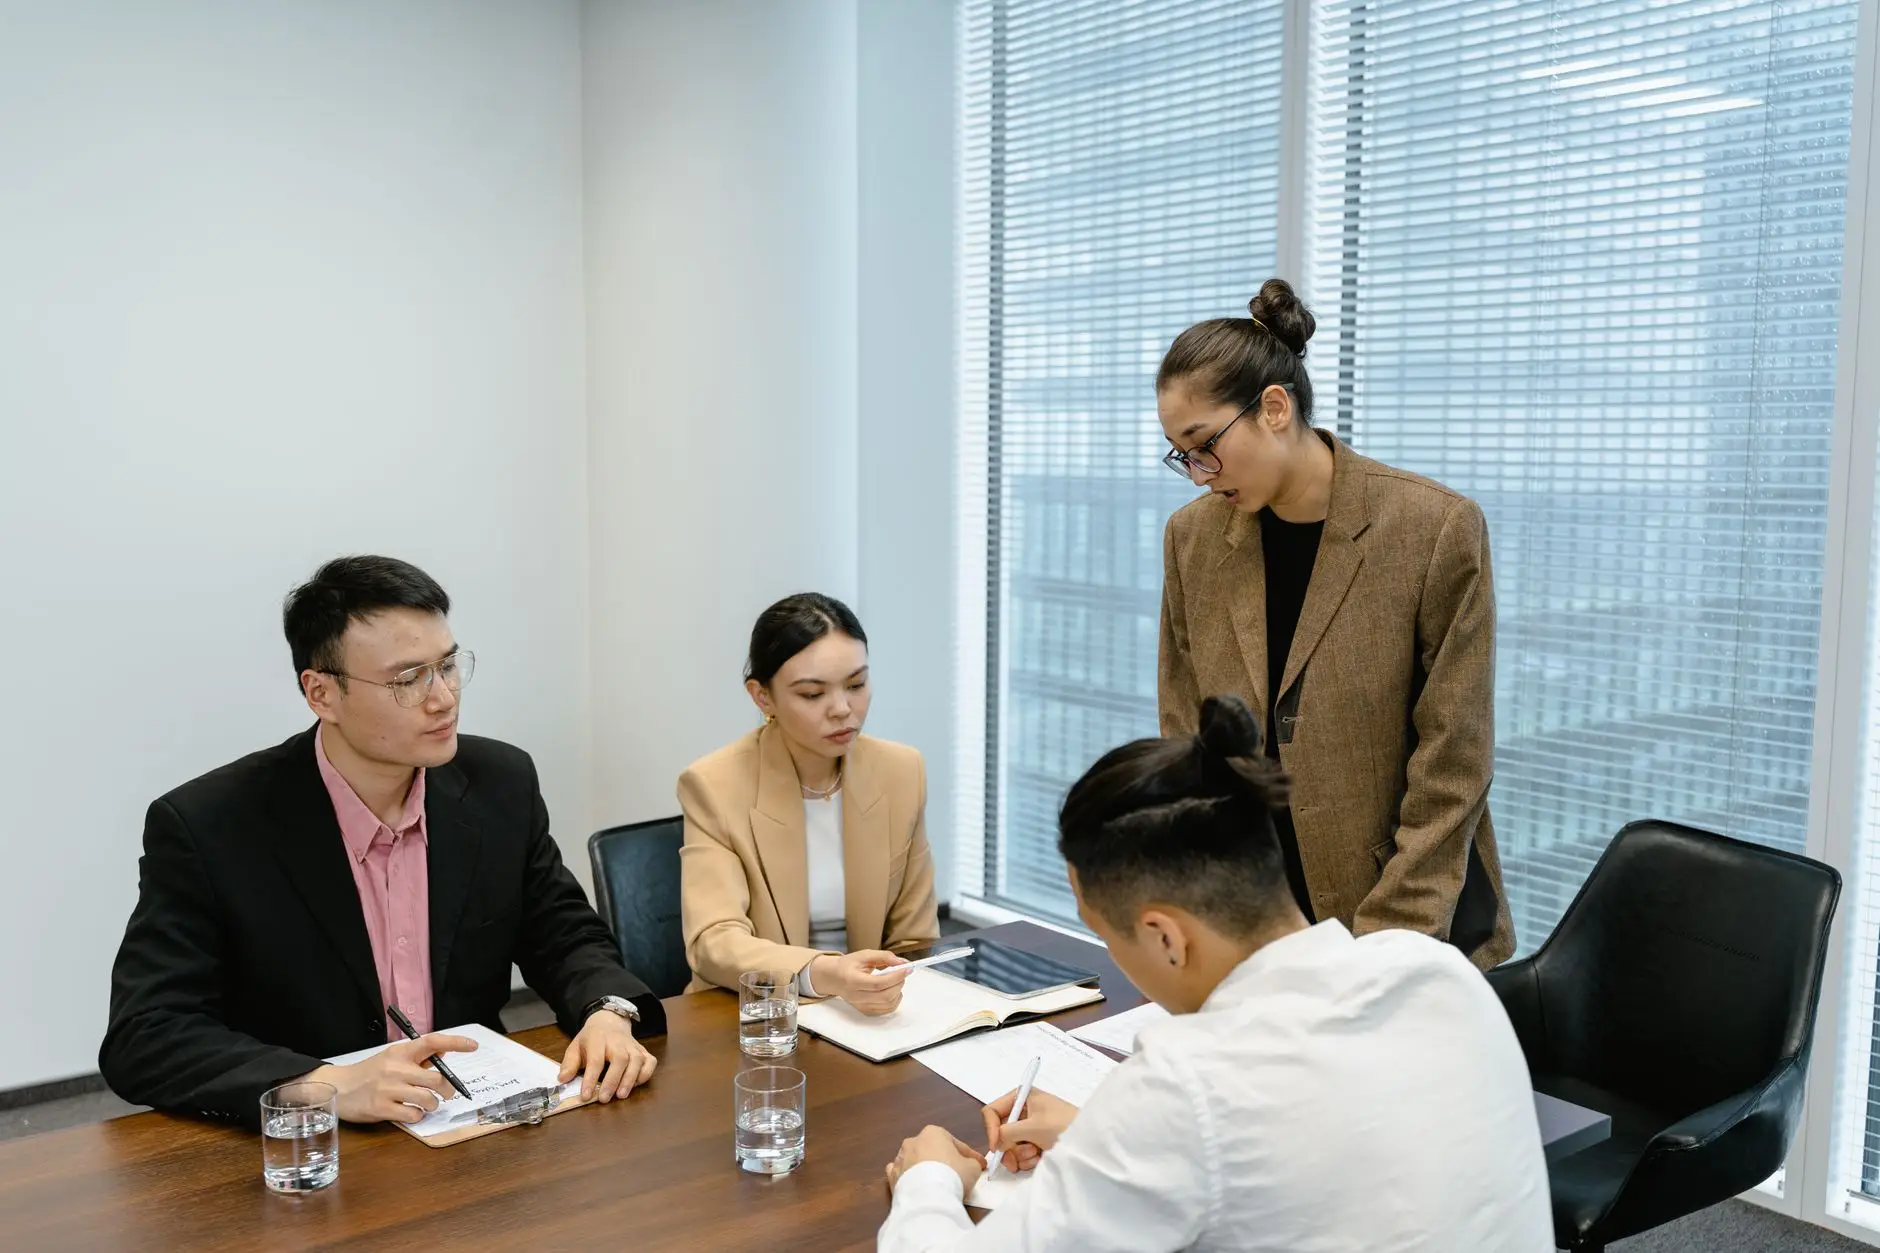
When artificial intelligence tools first entered the mainstream corporate workspace, organizations instinctively routed them through the IT department. After all, setting up enterprise software, managing cloud deployments, and provisioning API keys have traditionally fallen squarely within the technical domain. However, as global legislative bodies roll out binding frameworks such as the European Union Artificial Intelligence Act, treating artificial intelligence compliance as merely another software patch or infrastructure upgrade is a dangerous strategic miscalculation.
An Editorial AI Regulation No Longer Treated as a simple IT headache reveals a deeper operational truth. Modern artificial intelligence systems touch every facet of an enterprise, from human resources recruitment pipelines and customer data processing to financial risk modeling and intellectual property management. When regulatory penalties can reach millions of euros or a percentage of global turnover, the governance of these tools demands active oversight from legal teams, chief executive officers, risk officers, and privacy professionals.
The Shift from Infrastructure to Governance
Historically, IT departments focus on performance, uptime, system integration, and cybersecurity hardening. While these technical safeguards remain vital, they do not automatically address the complex legal mandates embedded in modern data protection and artificial intelligence laws. Technical teams configure models, but they cannot legally determine whether a training dataset violates copyright law, whether a predictive scoring algorithm causes unlawful bias, or whether a consumer consent mechanism meets strict regulatory standards.
According to the Organisation for Economic Co-operation and Development, effective artificial intelligence frameworks require robust accountability mechanisms that span organizational leadership, not just technical operators. When an organization deploys a machine learning model for automated decision-making, the resulting legal liability rests with the business entity and its executive leadership, not the systems administrator who configured the server.
Real-World Consequences of Compartmentalized Thinking
Consider a mid-sized financial services firm that deployed an automated credit-scoring tool developed by a third-party vendor. The IT department successfully integrated the application programming interface into the customer portal within two weeks, declaring the project an operational success. Six months later, regulatory auditors discovered that the model systematically denied credit to applicants based on proxy variables correlated with protected demographic categories.
Because the deployment was treated strictly as an IT project, no fairness audits were conducted, no data protection impact assessment was completed, and the legal team was never consulted prior to launch. The resulting regulatory investigation and reputational damage far outweighed any efficiency gains the software provided.
| Traditional IT Approach | Holistic Enterprise Governance |
|---|---|
| Focuses purely on software deployment and uptime | Evaluates legal liability, bias, and ethics |
| Relies solely on vendor technical documentation | Performs independent compliance and privacy audits |
| Maintains siloed communication within tech teams | Involves legal, compliance, executive, and IT stakeholders |
Building a Cross-Functional Artificial Intelligence Committee
To navigate this complex regulatory environment, forward-thinking organizations are dismantling traditional silos and establishing multidisciplinary artificial intelligence governance boards. These committees bridge the gap between technical execution and legal compliance. By bringing together chief information security officers, compliance officers, data protection specialists, and legal counsel, businesses can evaluate risks before deployment rather than scrambling after a regulatory inquiry.
Organizations must implement several foundational steps to transition their compliance posture:
- Mandate comprehensive risk assessments before procuring or deploying any generative or predictive artificial intelligence tool.
- Establish clear internal lines of accountability across business units rather than defaulting responsibility to the technical team.
- Involve data protection officers early in the procurement lifecycle to evaluate data provenance and consent trails.
- Provide ongoing education for non-technical executives regarding emerging technological liabilities.
Frequently Asked Questions
Why cant IT departments handle artificial intelligence compliance alone?
Information technology teams manage systems and software performance, whereas compliance requires legal interpretation, ethical evaluations, bias testing, and regulatory alignment that fall outside standard technical duties.
Who should be held accountable for artificial intelligence regulatory violations?
Executive leadership and the board of directors bear ultimate organizational responsibility for compliance, supported by dedicated risk, legal, and privacy professionals.
What is the primary risk of treating artificial intelligence as a purely technical tool?
Organizations face severe regulatory fines, algorithmic bias, data protection violations, and reputational damage when legal and ethical risks are overlooked during deployment.
Conclusion
The maturation of digital markets means that artificial intelligence governance is now a core pillar of corporate strategy. As regulatory oversight intensifies worldwide, organizations must recognize that an Editorial AI Regulation No Longer Treated as an isolated IT concern is the baseline for survival. By elevating governance to the boardroom and fostering collaboration across all departments, businesses can innovate safely while protecting both their customers and their operational longevity.











Leave a Reply