



How Healthcare Providers Should Handle Access Requests Under Data Protection Law

Share
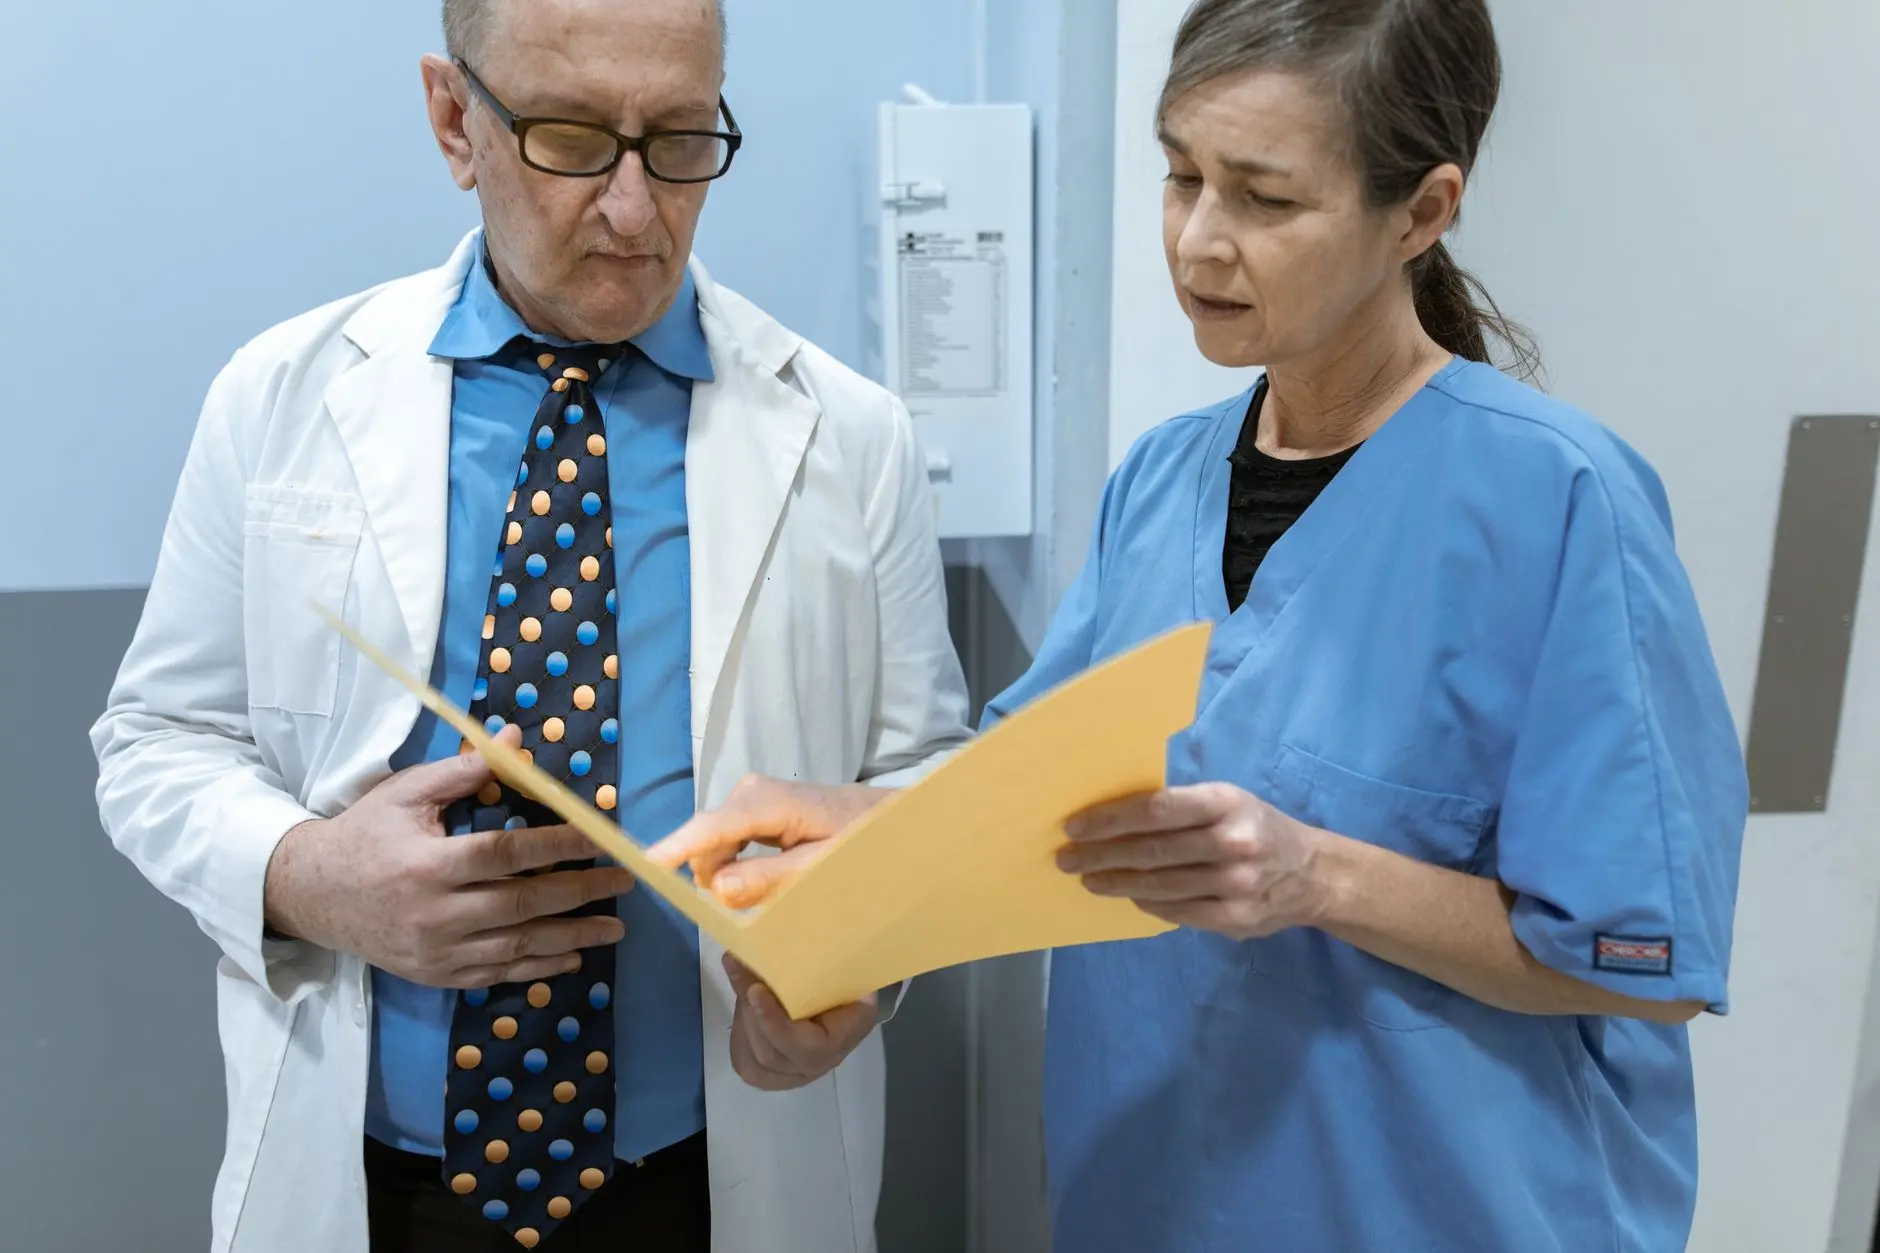
Medical practices and hospital networks handle vast amounts of sensitive personal data daily. When a patient requests copies of their medical history, clinical notes, or billing records, administrators face strict legal obligations. Failing to manage these inquiries properly can result in heavy regulatory fines, reputational damage, and eroded patient trust. Understanding how healthcare providers Handle Access Requests Law is vital for maintaining lawful, transparent operations in modern medicine.
The Legal Framework Governing Medical Data Access
Data protection frameworks worldwide, including the General Data Protection Regulation (GDPR) and the Health Insurance Portability and Accountability Act (HIPAA) in the United States, grant individuals fundamental rights over their personal information. For medical institutions, this means patients possess a legal right to inspect and obtain copies of their health records.
Compliance teams must balance transparency with absolute security. While patients have a broad right of access, providers must verify identity rigorously before releasing sensitive clinical details to prevent malicious data exposure. Navigating this balance requires documented internal workflows and regular staff training.
Core Timelines and Statutory Deadlines
Time is of the essence when processing formal record applications. Under most statutory frameworks, organizations must fulfill requests without undue delay and typically within 30 days of receipt. In complex cases, extensions may apply, but patients must receive formal notification explaining the delay before the initial window closes.
| Jurisdiction / Regulation | Standard Response Window | Permitted Extension |
|---|---|---|
| GDPR (EU/UK) | 1 Month | An additional 2 months for complex requests |
| HIPAA (United States) | 30 Days | One 30-day extension with written notice |
| Local Data Protection Acts | 14 to 30 Days | Varies by regional statutory guidelines |
Real-Life Scenario: Preventing Unauthorized Disclosures
Consider a busy metropolitan clinic receiving an email from an estranged family member asking for a patient’s recent surgery notes. Without proper verification protocols, a front-desk employee might mistakenly send the records, triggering a severe data breach. To prevent such incidents, healthcare entities must ensure that compliance programs mandate strict identity authentication before any file leaves the secure network.
Regulators emphasize that convenience must never override security. As noted in guidance from the U.S. Department of Health & Human Services, covered entities must provide individuals with timely access while safeguarding electronic health information against unauthorized interception or viewing.
Step-by-Step Action Plan for Compliance Teams
Implementing a structured approach helps organizations process applications smoothly without disrupting daily clinical workflows. Business leaders and IT directors should establish clear operational baselines:
- Centralize Intake Channels: Route all incoming inquiries through a dedicated, secure portal or email address monitored by trained privacy officers.
- Verify Identity Securely: Use multi-factor authentication or secure in-person checks to confirm the requester is indeed the patient or an authorized legal representative.
- Review for Third-Party Data: Carefully examine records to redact confidential information about other individuals, such as family members mentioned in clinical notes, unless consent is provided.
- Deliver Securely: Transmit digital records via encrypted email or secure client portals rather than unsecured public web forms.
- Maintain Audit Logs: Keep detailed records of every request received, dates of fulfillment, and staff members involved for accountability.
Handling Exemptions and Refusals
Not all information is automatically releasable upon demand. Privacy laws recognize specific exceptions where disclosure could cause serious harm. For instance, if a licensed mental health professional determines that sharing certain psychotherapy notes would endanger the physical safety of the patient or others, the request may be lawfully restricted.
When refusing or limiting a request, providers must provide a clear written explanation, detailing the legal grounds for the restriction and outlining the patient’s right to lodge a complaint with the relevant data protection authority.
Frequently Asked Questions
Can healthcare providers charge fees for supplying records?
Under most modern legal frameworks, providing the first copy of electronic records must be free of charge. Reasonable cost-based fees may apply only for physical copies, postage, or manifestly excessive subsequent requests.
What happens if a patient requests data belonging to a deceased relative?
Access rules for deceased individuals vary significantly by jurisdiction. Compliance teams must consult regional laws to determine whether personal representatives, executors, or close family members hold inheritance rights to health records.
Conclusion
Mastering how healthcare providers Handle Access Requests Law requires a blend of rigorous administrative procedures, secure technology, and compassionate patient communication. By treating subject access inquiries as an operational priority rather than a burdensome administrative chore, medical organizations protect patient rights, mitigate legal liabilities, and build lasting digital trust.










Leave a Reply