



How Insurance Companies Handle Access Requests Under Data Protection Law

Share
The Unique Challenges of Insurance Data Processing
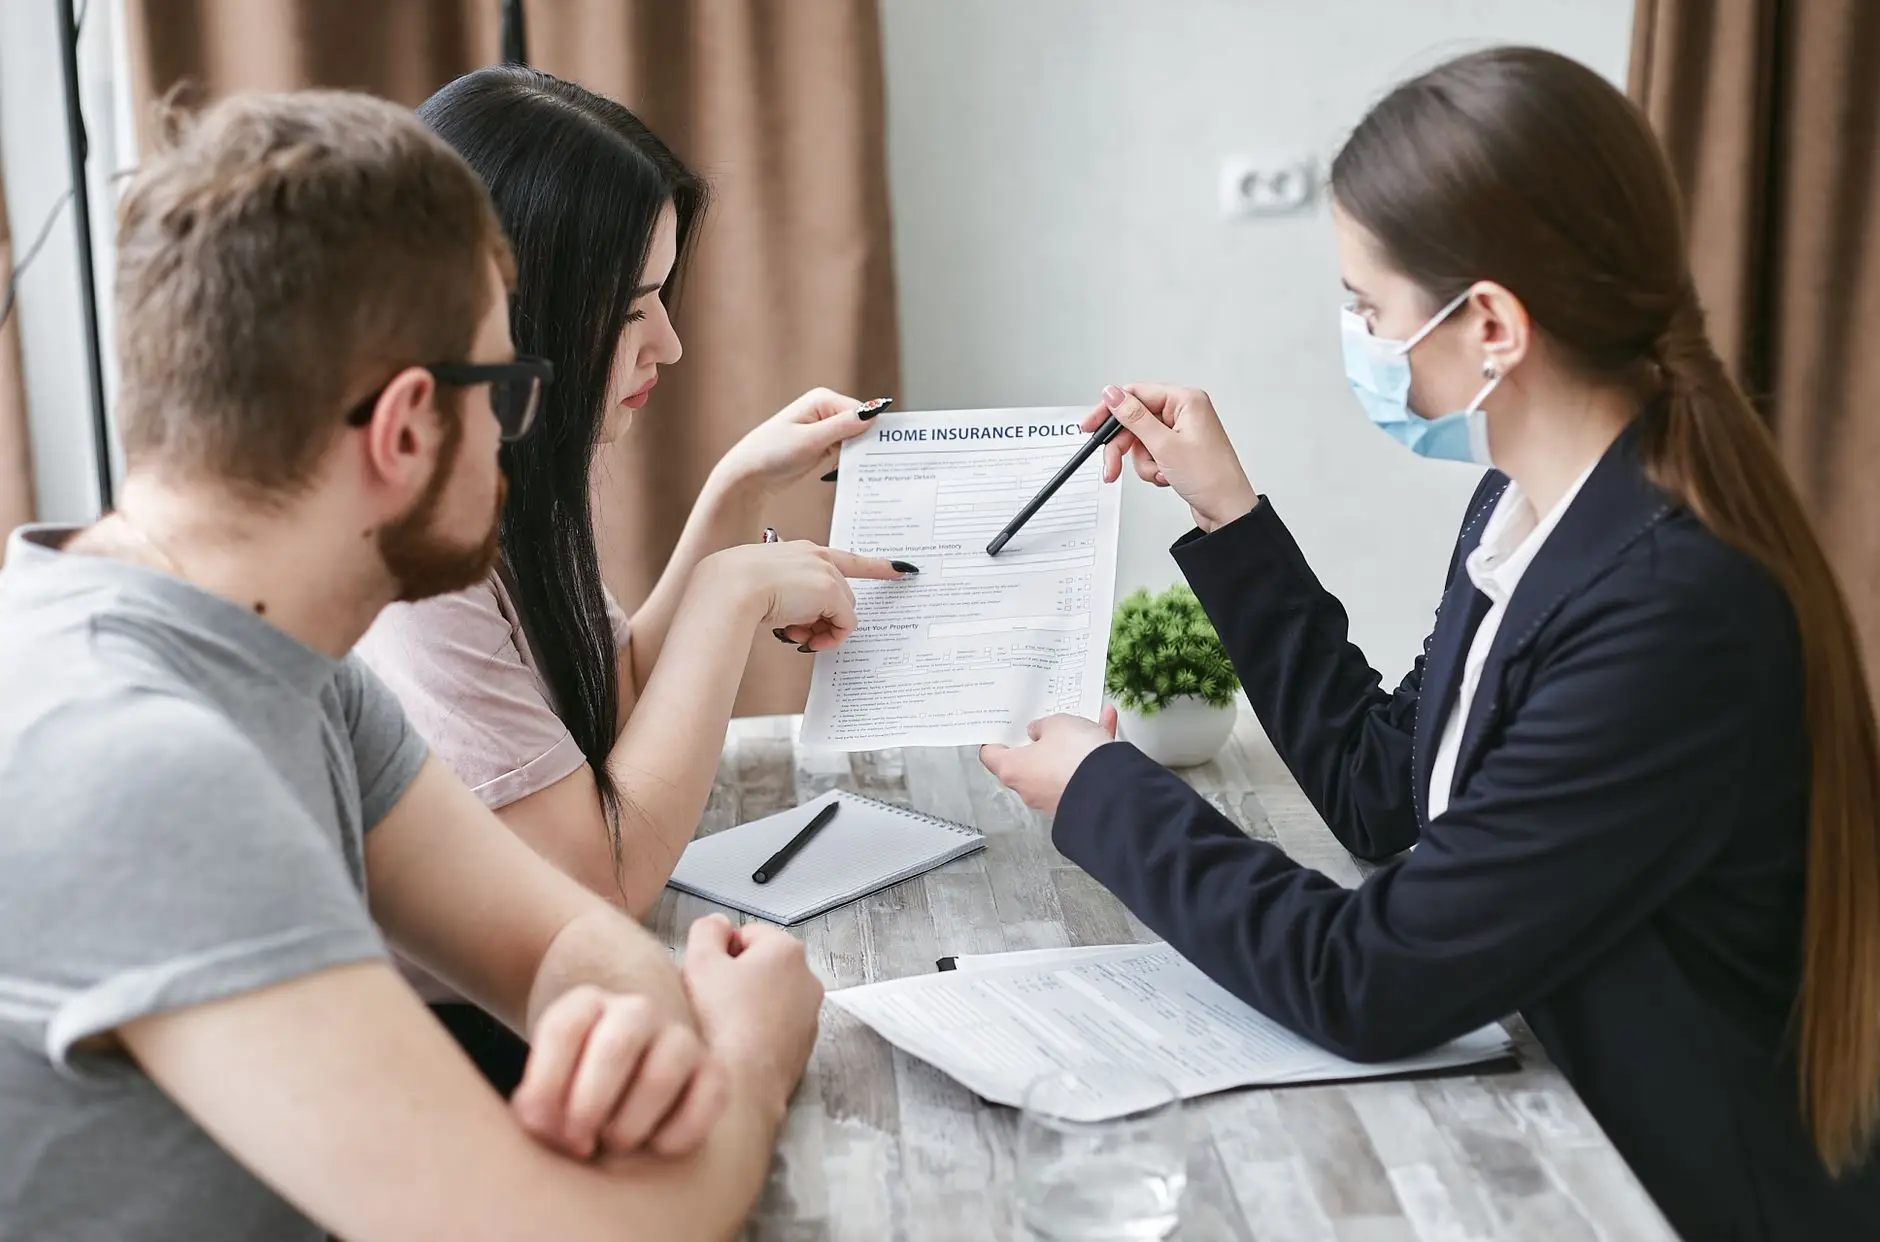
Insurance companies process some of the most sensitive personal data in the modern economy. From medical history and financial records to detailed claims notes and fraud investigations, insurers maintain vast dossiers on their policyholders and claimants. Because of this high volume of sensitive information, learning how insurance Handle Access Requests Law is a vital compliance necessity rather than a back office administrative task.
Under modern data protection frameworks such as the General Data Protection Regulation (GDPR) and various global privacy statutes, individuals hold the right to obtain a copy of their personal data. For insurers, fulfilling these Data Subject Access Requests (DSARs) often involves navigating legacy systems, unstructured notes, third-party medical reports, and complex exemptions regarding fraud detection and legal privilege.
Understanding the Scope of an Access Request in Insurance
When an individual submits an access request to an insurance provider, they are typically looking for more than just their policy documents. They want to know every piece of information the company holds about them, why it was processed, and who it was shared with. This includes underwriting algorithms, risk scoring metrics, call center recordings, and adjuster notes.
Many organizations struggle because insurance data is siloed across different departments. A single customer file might touch sales, underwriting, claims management, and actuarial analysis. To comply with statutory timelines, usually one month under laws like the GDPR, compliance teams must coordinate quickly across these business units.
| Insurance Department | Common Data Types Held | DSAR Challenge |
|---|---|---|
| Underwriting | Medical questionnaires, financial history | Unstructured notes and risk scoring variables |
| Claims | Accident reports, medical records, investigator logs | Protecting third-party personal data |
| Fraud Detection | Suspicious activity indicators, background checks | Navigating anti-fraud exemptions |
Balancing Privacy Rights and Commercial Confidentiality
One of the most complex hurdles when insurance companies handle access requests is protecting third-party data and confidential business secrets. For example, if a claims file contains notes about a witness or a medical professional’s independent assessment, releasing that information raw could breach another individual’s privacy rights.
Regulatory authorities emphasize that the existence of third-party data does not automatically give an insurer the right to refuse a request entirely. Instead, compliance teams must redact or summarize the information where feasible. As noted by data protection authorities, transparency is the cornerstone of trust, but organizations must carefully balance disclosure obligations against legitimate exemptions.
Real-Life Scenario: Navigating a Contentious Claims Dispute
Consider a scenario where a policyholder has their disability claim denied. Frustrated by the decision, the claimant submits a comprehensive DSAR asking for all internal notes, underwriting assessments, and investigator files. The insurance company’s claims department discovers that an external investigator marked the claimant as potentially suspicious.
If the insurer simply dumps all raw notes into a portal without review, they risk disclosing the confidential methodology of their anti-fraud investigators, which may trigger an exemption under local law regarding the prevention and detection of crime. However, withholding the entire investigative file without a valid legal basis will invite regulatory complaints and potential fines. The correct approach requires a line-by-line review to separate factual personal data about the claimant from protected proprietary methodology.
Key Steps for Insurance Compliance Teams
To streamline operations and minimize regulatory risk, insurance executives and compliance officers should implement a structured framework for handling access requests:
- Centralize Intake: Establish a dedicated channel for DSAR submissions so requests do not languish in regional sales or customer service inboxes.
- Deploy Smart Discovery Tools: Use modern compliance technology to scan legacy databases, unstructured email archives, and audio recordings.
- Train Frontline Staff: Ensure customer-facing employees know how to recognize a formal access request, even if the customer does not explicitly cite data protection legislation.
- Apply Exemptions Judiciously: Document every instance where data is redacted or withheld, ensuring reliance on clear legal grounds such as legal privilege or fraud prevention.
Frequently Asked Questions
Can insurance companies charge a fee for processing access requests?
Under most modern data protection laws, initial access requests must be fulfilled free of charge. A fee can only be charged if a request is manifestly unfounded or excessive, particularly if it is repetitive.
Are insurance underwriting algorithms subject to access requests?
Yes. Individuals have the right to obtain meaningful information about the logic involved in automated decision-making, including automated risk profiling used in insurance underwriting.
Conclusion
Mastering how insurance Handle Access Requests Law protects both the organization and its customers. By treating data subject rights as a core operational priority rather than a regulatory burden, insurers can build lasting digital trust while avoiding costly regulatory penalties and reputational damage.









Leave a Reply