



A Step-by-Step Guide to Managing Location Data Responsibly

Share
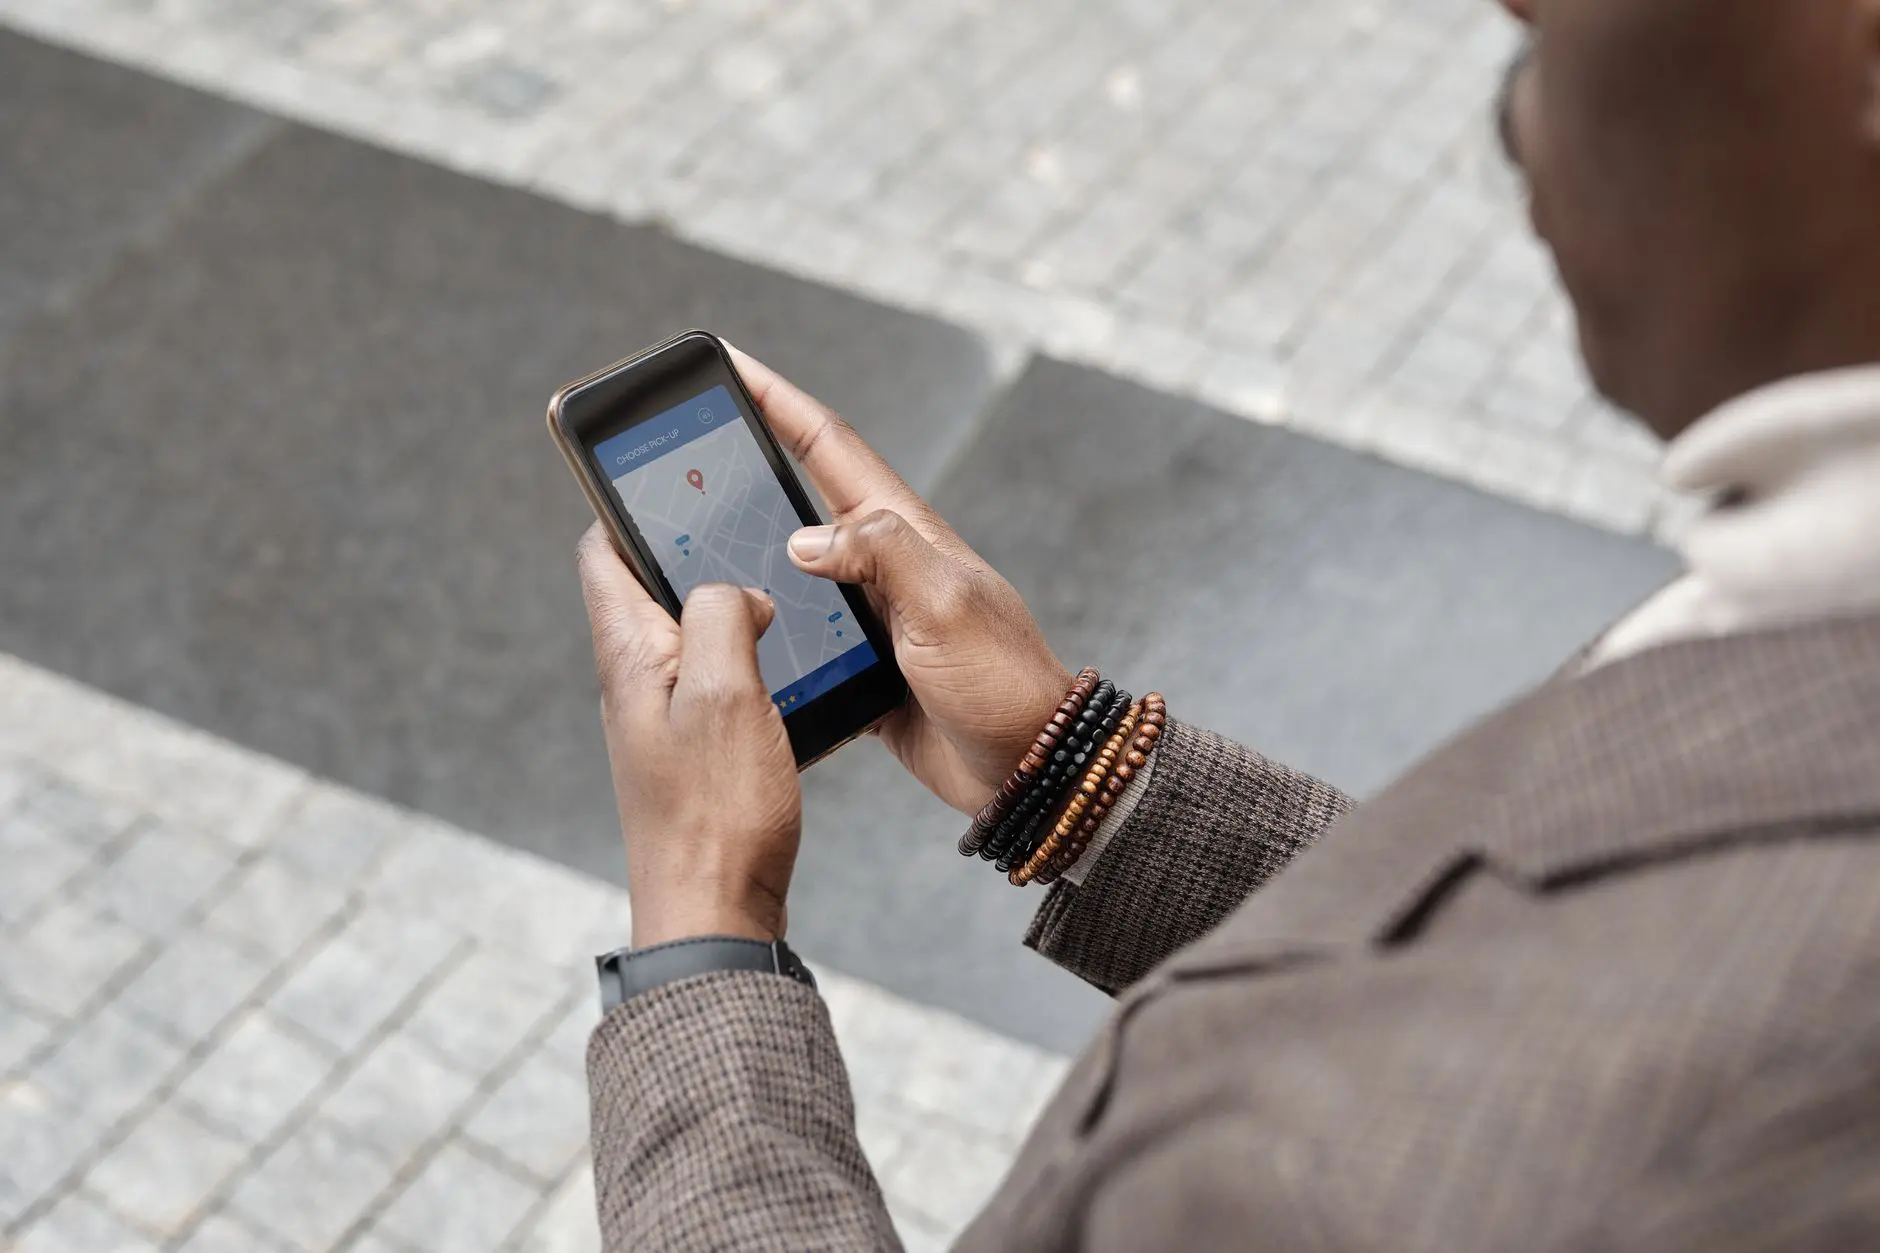
Introduction to Location Data Risks
Geolocational information is among the most sensitive categories of personal data processed by modern organizations. Whether captured through mobile applications, Internet of Things devices, or website tracking beacons, precise coordinates reveal intimate details about daily habits, religious practices, healthcare visits, and political affiliations. For privacy professionals and compliance officers, executing Step Step Managing Location Responsibly is no longer just a technical checkbox. It is an operational necessity required by strict regulations such as the GDPR and international data protection laws.
When businesses collect and store geographical points without robust governance, they expose themselves to severe regulatory fines, catastrophic data leaks, and a permanent loss of consumer trust. According to research from the European Union Agency for Cybersecurity (ENISA), poor telemetry handling remains a primary vector for unauthorized profiling and invasive surveillance. Building a responsible tracking framework protects both the enterprise and the data subject.
Understanding the Regulatory Landscape
Global privacy regulators treat geographical telemetry as uniquely identifying information. Under modern compliance mandates, tracking a user device across coordinates requires explicit consent, strict minimization, and transparent disclosure. Businesses must understand that IP addresses, GPS points, Wi-Fi triangulation, and Bluetooth beacon data all fall under regulated data definitions.
When planning how to implement Step Step Managing Location Responsibly, compliance teams must evaluate jurisdiction-specific requirements. For instance, European regulators enforce stringent rules under the General Data Protection Regulation, while various states in the USA have introduced comprehensive privacy statutes targeting precise consumer tracking.
To navigate these regulatory expectations, organizations should establish clear internal policies. You can explore our foundational insights on data protection principles to align your operational workflows with legal mandates. Furthermore, integrating compliance frameworks ensures your data processing activities withstand regulatory audits.
Core Steps for Responsible Location Governance
Implementing a sustainable privacy-first operational model requires a structured workflow. The following step-by-step approach helps organizations balance utility with privacy preservation.
Step 1: Conduct a Data Mapping and Necessity Audit
Before collecting any geographic telemetry, organizations must answer a fundamental question: Is this information strictly necessary for the core product offering? Audit every software development kit, third-party vendor, and internal database that touches tracking telemetry. Eliminate unnecessary collection points to minimize overall risk exposure.
Step 2: Implement Granular Consent Mechanisms
Users must understand why their coordinates are being tracked and how long the information will be retained. Avoid dark patterns or pre-checked consent boxes. Provide clear toggles that allow individuals to share coarse locations (such as city-level data) rather than precise GPS coordinates whenever exact positioning is not strictly required.
Step 3: Apply Technical Minimization and Obfuscation
Data minimization protects organizations if a breach occurs. Store only what is needed, and do it for the shortest possible duration. When long-term storage is necessary for analytics, apply cryptographic hashing, differential privacy, or geographic perturbation to blur exact coordinates.
| Telemetry Type | Risk Level | Recommended Control |
|---|---|---|
| Precise GPS Coordinates | Critical | Real-time masking, delete within 24 hours |
| Wi-Fi Triangulation | High | Aggressive pseudonymization and tokenization |
| IP-based City Data | Moderate | Truncation and standard retention limits |
Real-Life Scenario: The Cost of Over-Collection
Consider the cautionary case of a popular fitness application that aggregated running routes without proper anonymization. Although the company believed it was sharing benign fitness statistics, malicious actors successfully reverse-engineered the data points to reveal sensitive military installations and the daily routines of high-profile individuals. This incident resulted in intense media scrutiny, regulatory investigations, and a massive churn of active users. The lesson is clear: failing to practice responsible geographic governance can turn seemingly harmless analytics into a severe security vulnerability.
Expert Perspectives on Telemetry Governance
Industry leaders emphasize that transparency builds long-term brand resilience. As noted by privacy researcher and legal scholar Dr. Elena Vance, organizations must look beyond basic legal compliance:
“Treating geographic telemetry with the same rigor as biometric or financial records is no longer optional. True digital trust requires giving individuals absolute control over where their digital shadow travels.”
Engineering teams must collaborate closely with legal advisors to ensure that code execution matches privacy policies. When developers and compliance officers speak the same language, security gaps close rapidly.
Frequently Asked Questions
What makes geographic telemetry legally sensitive?
Coordinates can be easily linked back to an individual identity over time, revealing sensitive personal attributes such as medical clinic visits, home addresses, and personal associations.
How long should tracking logs be retained?
Retention periods should be as short as possible and tied directly to the specific business purpose for which the information was gathered.
Can anonymized tracking data be shared with third parties?
Even anonymized datasets carry re-identification risks. Organizations should conduct formal privacy impact assessments before sharing aggregated geographic information with external marketing partners.
Conclusion
Mastering Step Step Managing Location Responsibly requires a proactive commitment from every level of the organization, from developers writing the code to executives signing off on data strategies. By prioritizing data minimization, transparent consent, and robust technical safeguards, businesses can innovate safely while respecting the digital rights of their users. Protecting personal information is not just about avoiding penalties; it is the cornerstone of sustainable digital trust.










Leave a Reply