



How Law Firms Should Handle Access Requests Under Data Protection Law

Share
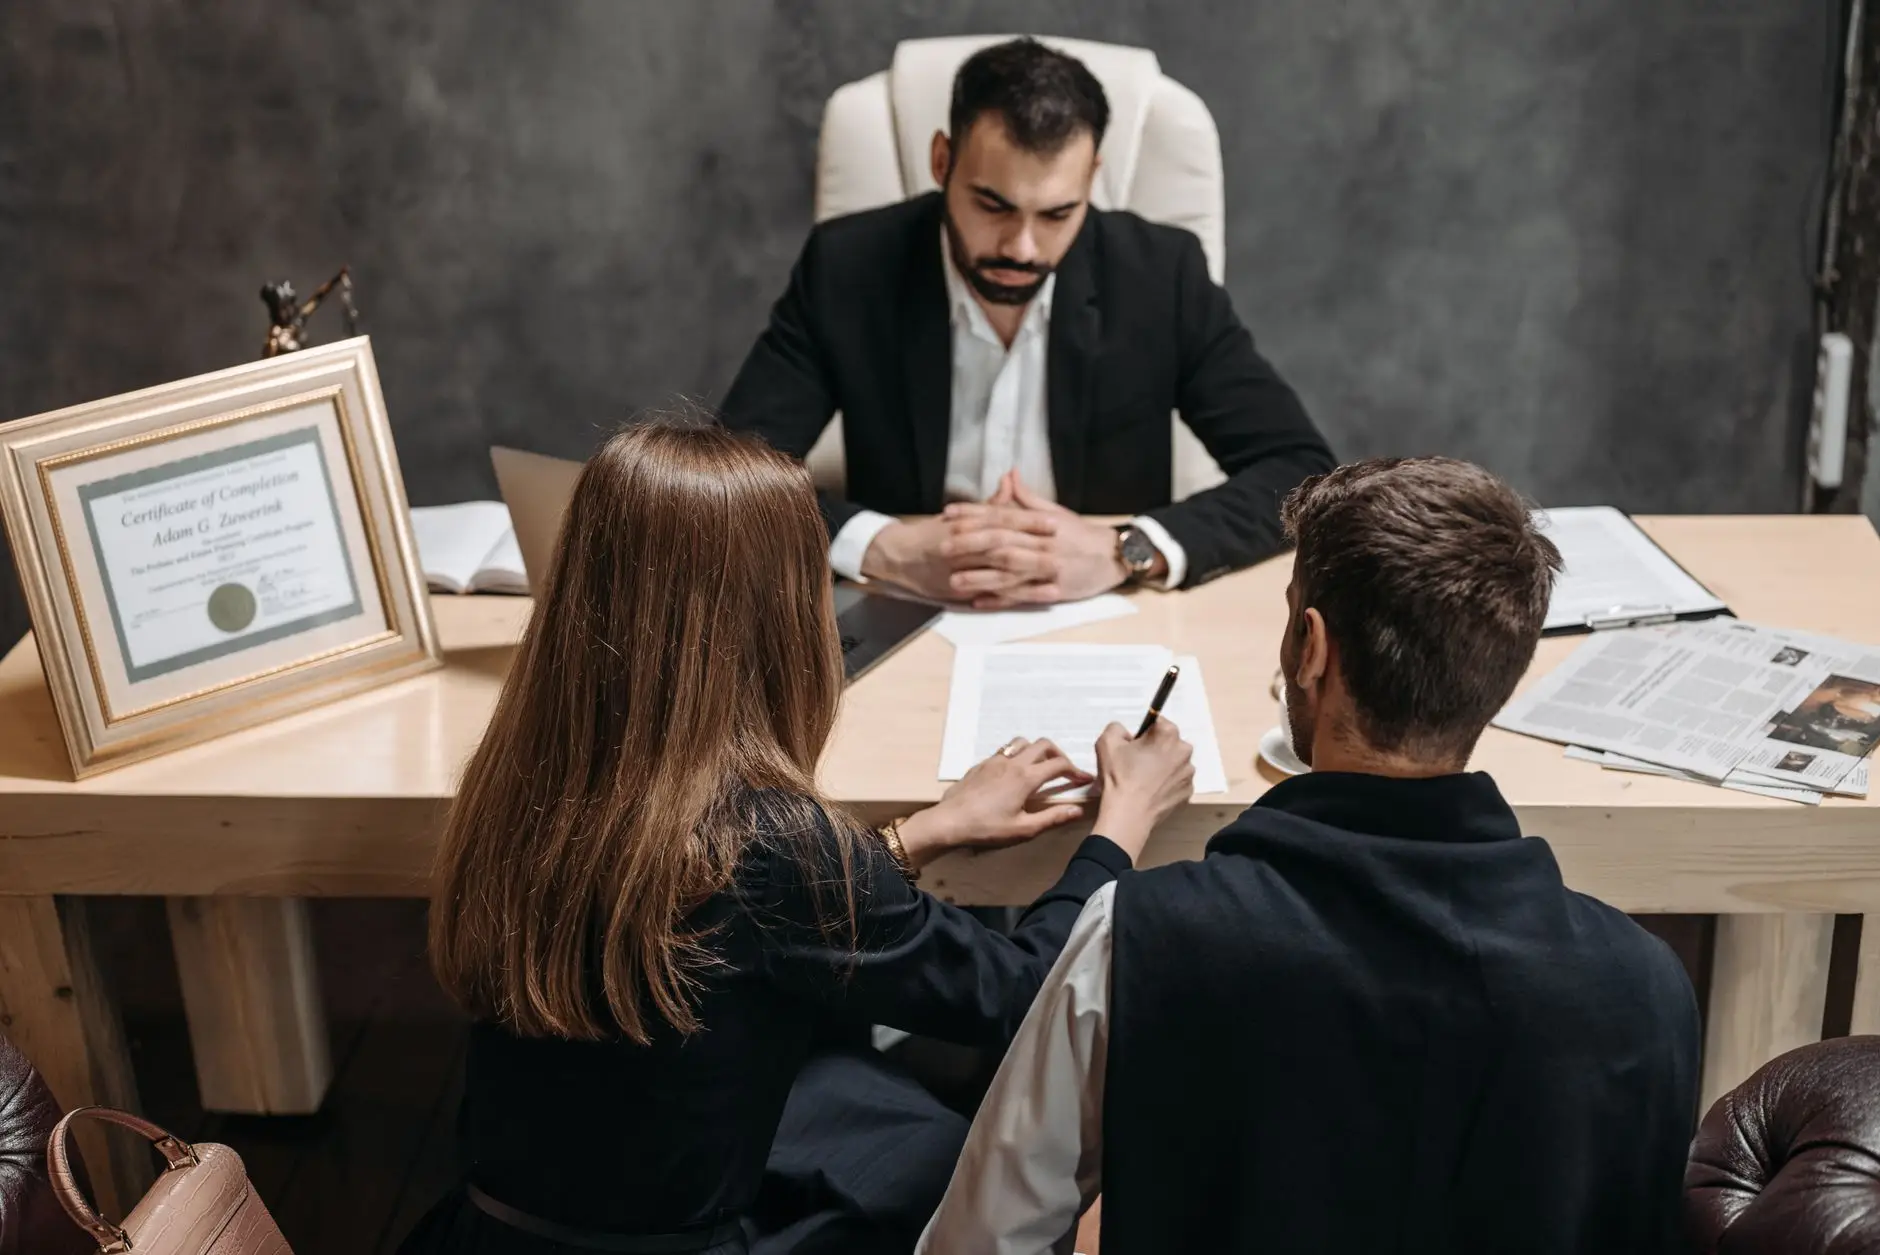
Law firms operate in a unique regulatory intersection. They hold vast amounts of sensitive personal data on behalf of clients, adversaries, employees, and third parties. When a data subject exercises their right of access under frameworks like the GDPR or modern privacy statutes, legal practices face an immediate operational puzzle. Unlike standard corporate entities, law firms must navigate strict professional secrecy obligations, attorney-client privilege, and complex file management systems.
Understanding how law firms handle access requests under data protection law requires balancing transparency mandates with sacred duties of confidentiality. Failing to respond correctly can result in severe regulatory penalties and reputational damage. This guide explores best practices for legal practices managing these intricate workflows.
The Core Challenge for Legal Practices
Data subject access requests, commonly known as DSARs, require organizations to provide individuals with copies of their personal data. For law firms, this obligation immediately collides with existing legal duties. Client files often contain a mix of personal data, confidential work product, and legally privileged communications.
Regulators frequently receive complaints regarding delayed or improperly rejected access requests from legal service providers. According to the Information Commissioner’s Office, organizations must respond to requests without undue delay and within one month in most jurisdictions. Law firms cannot ignore these deadlines simply due to heavy caseloads or complex file structures.
Navigating Legal Professional Privilege
The single most important exemption law firms rely on during a data subject access request is legal professional privilege, or attorney-client privilege. Personal data that falls under privilege is generally exempt from disclosure.
However, privilege is not a blanket exemption that covers an entire client file. Law firms must conduct a granular document-by-document review. Merely storing personal data within a privileged case file does not automatically shield it from disclosure if the underlying information is routine administrative data.
Key Exemptions to Consider
- Legal Professional Privilege: Communications between lawyer and client for the purpose of legal advice or litigation.
- Third-Party Confidentiality: Data that reveals confidential information about another individual, unless that person has consented.
- Pending Negotiations: Information related to ongoing settlement negotiations where disclosure would prejudice legal proceedings.
Step-by-Step Response Framework
Establishing a repeatable workflow ensures compliance without overwhelming fee-earners. When a request arrives, the internal privacy or compliance team should execute a structured protocol.
- Log and Verify: Record the date of receipt and verify the identity of the requester to prevent unauthorized data exposure.
- Assess Scope: Determine whether the request is manifestly unfounded or excessive, and communicate with the requester to narrow overly broad requests if permitted by local law.
- Coordinate with Case Teams: Alert the relevant attorneys or case managers handling the subject’s files to begin identifying relevant repositories.
- Execute Privilege Review: Conduct a rigorous legal review to redact or withhold privileged material and third-party data.
- Deliver Securely: Provide the collated data through a secure encryption channel, maintaining an audit trail of the transmission.
Managing Conflicts: DSAR vs. Client Confidentiality
A common friction point occurs when a disgruntled former client submits an access request hoping to bypass standard discovery rules or obtain internal firm evaluations. Law firms must maintain clear distinctions between data protection rights and procedural discovery rules.
Data protection law is designed to give individuals insight into how their data is processed, not to serve as a substitute for litigation discovery. If a request targets internal staff notes or subjective assessments, privacy teams must evaluate whether withholding is justified under exemptions for confidential references or management planning.
| Request Type | Primary Objective | Law Firm Action |
|---|---|---|
| Client Access Request | Obtain case files and personal records | Review for privilege, redact third-party data, release non-exempt personal data. |
| Employee Access Request | Review HR files, emails, and performance notes | Disclose personal data, withhold management planning data and confidential references. |
| Adversary Access Request | Gather intelligence on active disputes | Scrutinize carefully; apply litigation exemptions and privilege strictly. |
Practical Scenario: The Disgruntled Ex-Client
Consider a scenario where a law firm represents a client in a contentious divorce proceeding. Following the resolution of the matter, the former client submits a sweeping access request demanding all emails, internal notes, and billing records referencing them.
The firm cannot simply dump the entire case management system into a secure portal. The privacy officer collaborates with the managing partner to isolate personal data from true work product. Communications offering legal strategy and advice are redacted under privilege. Routine billing details and contact records are compiled and securely delivered within the statutory timeframe.
Best Practices for Law Firm Compliance
To mitigate risk and streamline operations, law firms should embed data protection principles directly into their practice management software. Maintaining structured document retention policies ensures that personal data is not retained longer than necessary, which naturally limits the scope of future access requests.
Training fee-earners and administrative staff on recognizing access requests is equally critical. Front-desk staff and junior associates must know how to forward formal requests immediately to the designated data protection officer rather than attempting ad-hoc responses.
Frequently Asked Questions
Can a law firm charge a fee for fulfilling an access request?
Under most modern data protection laws, initial access requests must be fulfilled free of charge. Fees can only be charged if a request is manifestly unfounded, excessive, or repetitive.
Are internal emails between partners exempt from access requests?
Not inherently. While emails containing legal advice are protected by privilege, casual internal correspondence discussing administrative matters or scheduling involving the data subject may be disclosable.
What is the penalty for failing to respond on time?
Regulatory authorities can issue formal reprimands, enforcement notices, and substantial financial penalties for non-compliance with statutory timelines.
Conclusion
Handling access requests requires legal practices to balance statutory transparency with the protection of client confidentiality and legal privilege. By implementing structured review protocols, training fee-earners, and maintaining clear distinction lines between data rights and discovery, law firms handle access requests effectively while safeguarding their core duties of professional secrecy.









Leave a Reply